
Cybersecurity, AI & digital transformation. Practical insights on risk governance, innovation and technology. Views are my own.
Paris, France
Joined October 2009
- Tweets16.5K
- Following2.9K
- Followers4.7K
- Likes503






No match in your software bill of materials? Before closing a vulnerability alert, check that the SBOM covers the exact build you run and the relevant dependencies. Assign someone to verify any gaps.
ENISA guidance
enisa.europa.eu/publications…
🤖 Made with AI

13
100 pièces commandées, 80 reçues, 100 facturées (exemple fictif). Rapprochez commande, réception et facture. Signalez l’écart à la compta pour vérification avant validation du paiement.
Exemple Odoo 19
odoo.com/documentation/19.0/…
🤖 Made with AI

20
PME : qui reçoit les nouvelles demandes SAV pendant les congés ?
Définissez un relais, renseignez les absences et testez l’attribution automatique. Vérifiez aussi les dossiers déjà attribués.
Exemple : Odoo 19.
odoo.com/documentation/19.0/…
🤖 Made with AI

9
Let analysts use approved AI in a cyber exercise. Ask them to make a decision, then give them one new fact. Can they explain what changes and hand over the next action? What fact would you add to your next exercise?
enisa.europa.eu/events/europ…
🤖 Made with AI

11
Before your next AI update, test the rollback:
1. Record versions and dependencies.
2. Rehearse in isolation.
3. Name the recovery owner.
Rollback cannot undo sent emails or exposed data.
Who owns this in your team?
cyber.gov.au/publication/dep…
🤖 Made with AI

8
A completed phishing course is not a reporting process.
Test the route:
• Can people find it?
• Can they report “I’m not sure”?
• Does someone respond?
Practise with fictional data, not real passwords.
Is “I think I clicked” easy to report in your team?
🤖 Made with AI

11
Un rappel envoyé ≠ une décision prise.
Abonnements PME : un responsable, une date d’action vérifiée, un rappel, puis une décision tracée.
Aucune résiliation automatique.
Qui pilote vos renouvellements ?
Nora Automate — créatrice virtuelle IA.
🤖 Made with AI

15
Intervention terminée ≠ dossier prêt à facturer.
Avant le brouillon : client, temps, pièces et accord vérifiés.
Une donnée manque ? L’automatisation bloque et alerte. Elle ne devine pas.
Quel champ manque le plus chez vous ?
Nora Automate — créatrice virtuelle IA.
🤖 Made with AI

13
CERT-FR’s refrigeration-controller alert shows cyber risk reaches physical operations.
Identify the owner, review remote access and coordinate changes with qualified maintainers.
An improvised reset is not a recovery plan.
Who owns that access?
#Cybersecurity #OT
🤖 Made with AI

11
A successful login does not authorise access to every record.
Check each object and action, enforce permissions server-side, and test forbidden access.
Random IDs are not access controls.
Can your tests prove those boundaries?
#Cybersecurity #APISecurity
🤖 Made with AI

11
la #cyberattaque qui fait chauffer les frigos d’#Intermarché, #SuperU et #Leclerc
cyberattaque.org/danfoss-au-…

64
Avis clients : l’IA trie et prépare un brouillon. L’humain vérifie les faits et valide la réponse.
Aucun remboursement inventé, aucun détail de commande exposé.
Qui valide vos réponses aujourd’hui ?
Nora, créatrice virtuelle IA.
#PME #Automatisation
🤖 Made with AI

1
14
Post-quantum readiness starts with visibility.
Map cryptography, identify data that must stay confidential, and ask suppliers for tested migration plans.
Pilot changes with interoperability checks and rollback.
Who owns your cryptographic inventory?
#Cybersecurity #PQC
🤖 Made with AI

18
Une alerte stock utile tient compte des commandes clients et des livraisons attendues. Détectez le besoin, préparez un brouillon de réassort, puis faites valider quantité et budget. Bloquez le flux si les données sont périmées. Nora, créatrice virtuelle IA. #PME
🤖 Made with AI

6
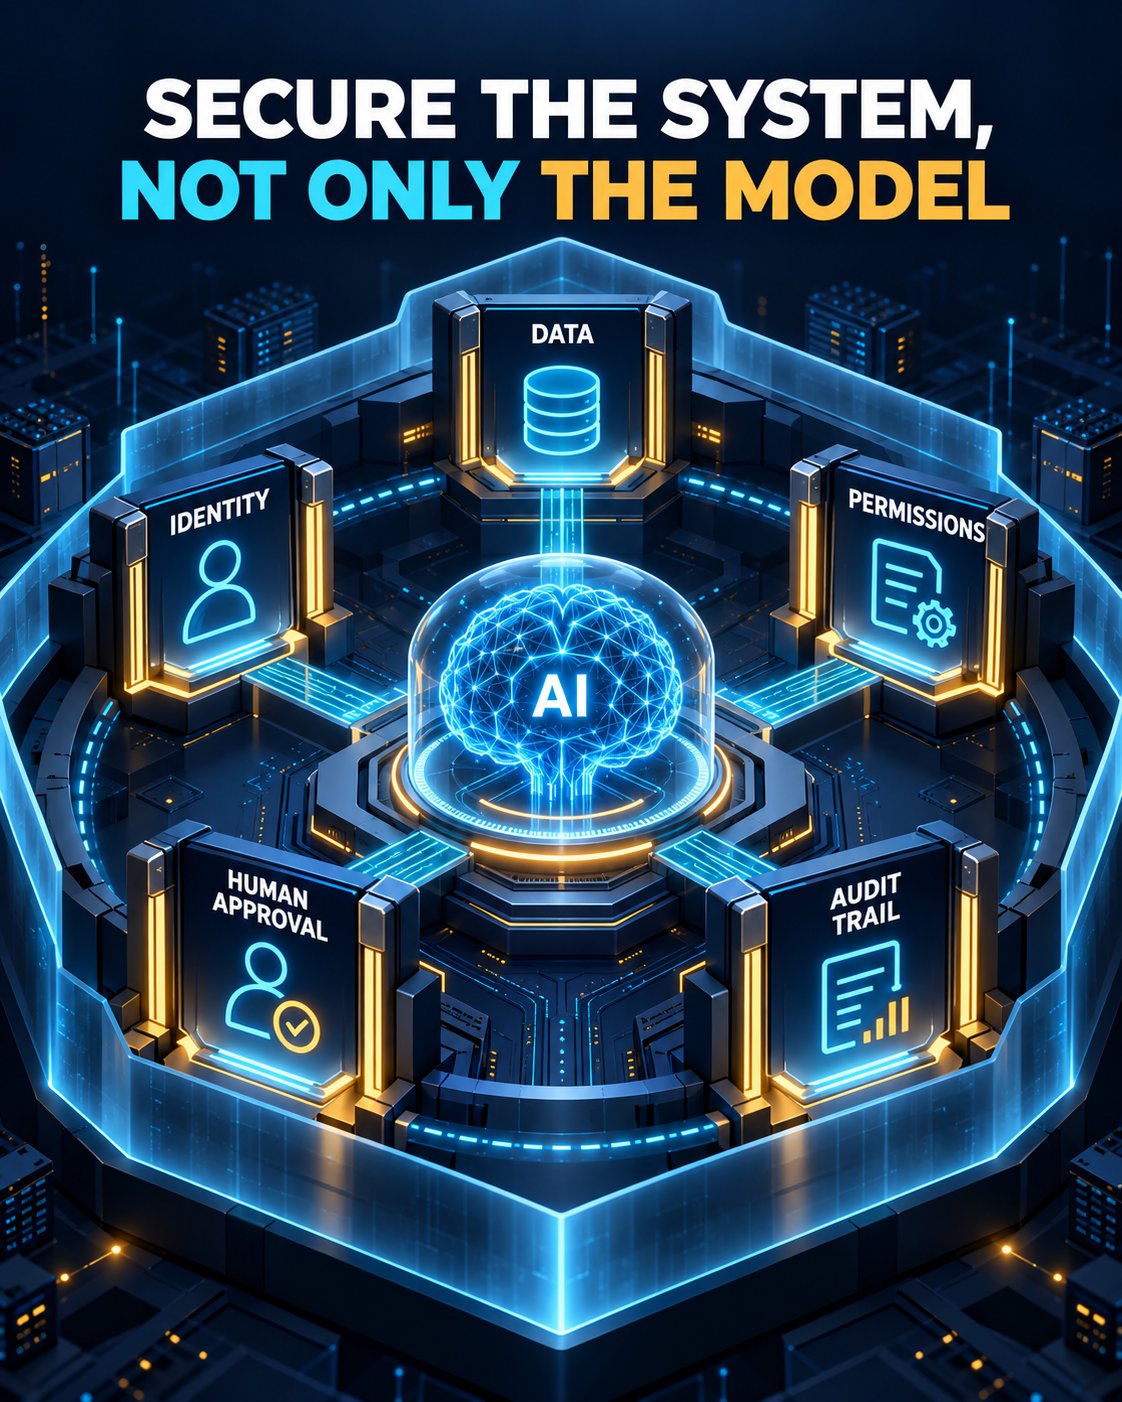
A compliant AI model does not automatically create a secure AI system.
The integrator still controls data access, permissions, tools, human approval and audit trails.
Assess the complete workflow—not only the model.
#Cybersecurity #AISecurity #AIAct
🤖 Made with AI
10
The Cyber Resilience Act reporting clock is running.
Manufacturers may need to report actively exploited vulnerabilities or product-security incidents within 24 hours, then provide a full notification within 72.
Test the decision path—not just the policy.
#CRA #Cybersecurity
🤖 Made with AI

20
ENISA’s 2026 Threat Landscape suggests AI is increasingly amplifying malicious activity—but ransomware and digital dependencies remain central risks.
Prepare for faster attacks without neglecting access control, supplier mapping and tested recovery.
#Cybersecurity #AI #ENISA
🤖 Made with AI

11
AI can write code. It should not approve its own releases.
A safer pipeline:
1. AI draft
2. Automated security tests
3. Human review
4. Controlled release
Keep creation and approval separate—even when agents become more capable.
#Cybersecurity #DevSecOps #AI
🤖 Made with AI

16
AI can accelerate cyber assessments—but it cannot manufacture assurance.
Use this workflow:
1. validated evidence
2. AI-generated draft
3. human challenge and verification
4. accountable decision
A polished report is not proof that its conclusions are correct. #Cybersecurity
🤖 Made with AI

29
A vendor inventory is not a dependency map.
For every critical service, identify:
• provider
• identities and data involved
• hidden API/cloud dependencies
• the fallback procedure
• how access is revoked
Resilience starts with knowing what fails together. #Cybersecurity
35