

ethical-hacker | bug-bounty 🇮🇳
That’s Life !!
Joined March 2023
- Tweets4.2K
- Following614
- Followers473
- Likes42.6K




sandesh 𓊝 retweeted

You should ask Opus 5.5 (or any other model) to identify signs of malware compromise on your personal computer and VPS instances


sandesh 𓊝 retweeted

All those years of refusing to learn excel and PowerPoint is about to pay off

sandesh 𓊝 retweeted
I'm done watching triage fail small businesses.
165 times, I've found a critical or high bug that someone had already reported. Still unfixed. Customer data still exposed. My report gets closed as a duplicate, and the business never hears a thing.
It isn't getting better. So I'm going around it.
I'll test your website, APIs and Android apps the way an attacker would. You get a plain-English report straight from me within 7 business days.
Then you pay what you think it was worth.
I know this is a weird offer.
So do me a favour drop a comment or repost so I can get some reach please


sandesh 𓊝 retweeted

.@sanjeevsanskrit tears into the argument that India should lower its age of consent because it is 16 in several US states


sandesh 𓊝 retweeted
Watch @SanjeevSanskrit, founder of @GemsOfBollywood and @sewanyaya, destroy the mindset behind attempts to legalise sex with schoolgirls
The talk was delivered at a recent event at Constitution Club of India, Delhi, where more than 200 leaders and activists from diverse sections of society gathered and signed a declaration opposing the lowering of the age of consent
sandesh 𓊝 retweeted

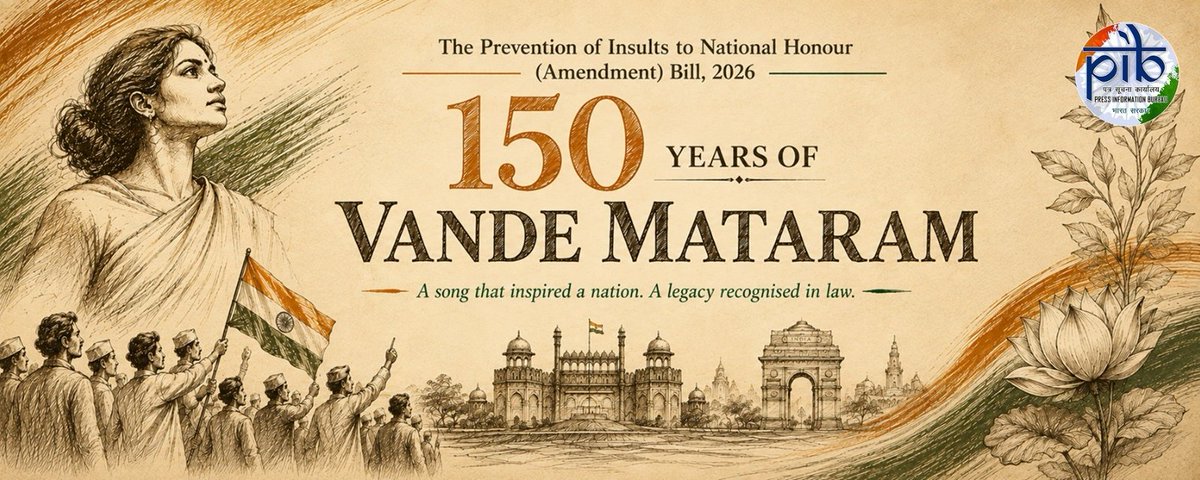
Vande Mataram has been accorded statutory protection under the Prevention of Insults to National Honour (Amendment) Act, 2026.
Read the article to explore its enduring legacy and renewed recognition as a national symbol 🇮🇳
#VandeMataram @MinOfCultureGoI

sandesh 𓊝 retweeted

Submit new reports using the HackerOne API with Quarry VRC 🔥
Manage your leads, monitor your HackerOne reports, and much more 🎉
Check it out👉github.com/skraft9/quarry-vr…
#TogetherWeHitHarder


sandesh 𓊝 retweeted
I can feel that OpenAI and Claude have tunable “hallucination” and “efficiency” settings at their main HQs, and the Lords of AI are instructed to reduce and increase these so consumers are forced to buy subscription after subscription and hop between these choices continually.
sandesh 𓊝 retweeted

I’ve noticed that most new folks who reach out for guidance in bug bounty feel overwhelmed early on trying to learn everything at once. That often leads to half-baked knowledge across multiple areas and slower overall progress.
Here's what I recommend instead 👇
1/
Pick one vulnerability type and go all in.
Master the ins and outs of that category - how it works, how it breaks, real-world examples, and ways to find it.
Once you’ve got depth in one area, the rest will follow naturally.
2/
To put this into perspective, here’s a snapshot of the types of issues I’ve reported over the last 5 years - gradually expanding focus as I grew more confident:
2020:
• Local cache issues
• Rate limit issues on Login
• Session invalidation
• MFA bypass
2021:
• Rate limit
• MFA bypass
• CSRF
• IDOR
• RBAC
2022:
• CSRF
• IDOR
• RBAC
• XSS
• Business logic
• Info disclosure
2023:
• Everything from 2022 +
• BBP automation
• Cache deception
• DoS Issues
• Subdomain takeover
• Auth bypass / misconfig
• SQLi
• SSRF
• RCE
2024:
• Everything from 2023 +
• AI-related issues
• Vhost misconfigurations
2025:
• Everything from 2024 +
• Many more new things that I will talk about soon :)
3/
There are more, of course, but this covers most of what’s worked well for me.
The key takeaway: you don’t need to know everything.
Play to your strengths. Stay consistent. And let your scope expand naturally.
Hope this helps someone starting out 💪