

ᴄʏʙᴇʀꜱᴇᴄᴜʀɪᴛʏ 🛡️ | ᴅꜰɪʀ 🕵️ | ᴄᴛꜰ ᴘʟᴀʏᴇʀ @teampwnus 🤖 | ʜᴏᴍᴇʟᴀʙʙᴇʀ 🐋 | ʀᴏᴄᴋ 🎸| ᴄᴀꜱᴜᴀʟ ɢᴀᴍᴇʀ 🎮| ɢᴏʟꜰ 🏌️♂️ | ᴄʜᴇꜰ 👨🍳 | ᴄᴀᴛ ᴅᴀᴅ 😸 | ꜰᴀʀᴍᴇʀ 👨🌾
127.0.0.1
Joined March 2020
- Tweets10.9K
- Following6K
- Followers6.6K
- Likes47.6K




Pinned Tweet
Comparison is the thief of joy.
Practice Gratitude, Set Personal Goals, Celebrate Small Wins 😎💪
4
544


Oste retweeted

Free Internal Red Team PenTest!
Your annual pentest shows one day. Attackers have the other 364.
SIMAPTIC runs a real attack in your environment and shows what your defenses missed.
Try it free: simaptic.ai/pricing/?utm_sou…
#redteam #pentest #cybersecurity #infosec

Oste retweeted

🚨 Critical Java4Shell vulnerability allows hackers to remotely execute code in Jira, Confluence, Jenkins, and other major platforms; CVE-2026-114938
YouTube Video (attached): youtube.com/watch?v=-EOYmL4U…
Security researchers at Calif have disclosed a critical OpenJDK vulnerability (CVSS 9.2) that could allow unauthenticated attackers to steal sensitive server memory and execute malicious code remotely.
Dubbed Java4Shell, the flaw affects OpenJDK's Base64 decoder. Researchers successfully demonstrated remote code execution against Keycloak, Jira, Confluence, Jenkins, JFrog Artifactory, and PingFederate in their default configurations.
The vulnerability affects supported Java distributions running on certain x86-64 processors with AVX-512 support. Researchers used AI to discover the flaw in approximately one hour and develop a working exploit in two more hours.
Security updates are now available. Administrators are urged to patch immediately or disable the vulnerable Base64 optimization.
Oste retweeted

Curated, simulated dataset of security logs (Windows, Web, Firewall, Cloud) with embedded attack vectors for SOC analysts to practice SIEM ingestion, threat hunting, and log analysis github.com/mahialjaber/SOC-L…

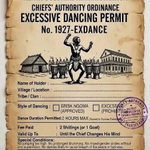
Not sure if this is a joke but if its actually true, we've come from far😂😂😂
WDYM 2shillings or goat

87


Oste retweeted

Microsoft Threat Intelligence observed an active phishing campaign exploiting the Microsoft 365 service disruption on November 12. The messages impersonate Microsoft 365 service health notifications and reference the legitimate Exchange Online incident EX1550543.
Some of the phishing emails Microsoft detected on November 13 falsely claim that messages were held during the outage and will be deleted within 24 hours unless recipients click to restore them.
Observed subjects follow the pattern "Outage - [six-character code]," with sender display names using organization-specific prefixes followed by "Outage Notification" or "Service Health."
The campaign uses three sender domains, moments-notice[.]com, planetmaison[.]com, and newbooker[.]com, with recipient-specific SendGrid click-tracking links redirecting to reallifeaccounting[.]com, including the observed path /themelist0.html. Similar messages targeted organizations across multiple US sectors.
The activity is consistent with credential phishing, although credential collection and malware delivery have not been confirmed.
Security teams can use Microsoft Defender for Office 365 Threat Explorer and Microsoft Defender XDR advanced hunting (EmailEvents, EmailUrlInfo, and UrlClickEvents) to identify suspicious messages, examine embedded URLs, and investigate user clicks.
Microsoft Defender for Office 365 Safe Links provides time-of-click protection against malicious URLs when properly configured. Organizations should verify their Safe Links policies, investigate potential user interactions, and confirm service disruptions directly through the Microsoft 365 admin center.

ALT Screenshot of phishing email using the Microsoft outage as lure
Oste retweeted

Your field guide to all things Kerberoasting.
From @TimMedin's original DerbyCon talk to SiegeCast episodes, attack breakdowns, detection tips, and defenses, we've got it all in one place.
Dig in, straight from the source: redsiege.com/kerberoasting/

Oste retweeted

Trivium v0.2.0 is out!
A simple log investigation tool inspired by Eric Zimmerman's Timeline Explorer. Explore CSV/JSON logs with search, filtering, timeline analysis, IOC matching, and annotations.
github.com/sumeshi/trivium #dfir

Oste retweeted

Back in May 2017, I got called to take portraits of the Kenyan President and his Deputy.
When I realised the assignment was too huge for me, I called on @allangichigi and made it a collaborative project.
This is the story of your gift taking you before important people (Proverbs 18 : 16), the power of collaboration and how having a camera has opened doors I never thought I'd walk through.


Oste retweeted

Did you know you can run ngrok (without installing it) by using tunnel.us.ngrok.com as a reverse tunnel?
Try this:
ssh -R 80:localhost:80 tunnel.us.ngrok.com http
It's the equivalent of `ngrok http 80`

Oste retweeted

New technique to identify if LDAP signing bypass has been patched on DCs. @GrayHatKiller found a creative way to determine patch status, and the best part is you can check it unauthenticated. His PR is merged to RelayInformer!

Oste retweeted

Bypassing LDAP signing🔥
Thanks to @snowpeacock, NetExec's enum_cve module now has a check for the patches that fix the LDAP signing bypass.
If the DC isn't patched, even enforcing signing does not prevent a relay.
Link to the blog post by @GrayHatKiller: specterops.io/blog/2026/10/2…

Oste retweeted

أداة بحث لأدوات ومصادر التحقيق الجنائي الرقمي (DFIR) ويمكن البحث حسب نوع artifact أو نظام التشغيل .
dfir-toolkit.github.io/
#الأمن_السيبراني #DFIR
