
🦅 The changelog says "bug fixes." The diff says "security patch." We track CVE-less fixes so defenders don't fly blind. New drop every Thursday. @78_lab
- Tweets163
- Following2
- Followers73
- Likes1


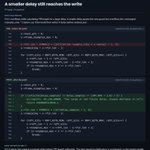
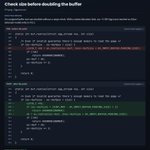
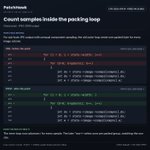
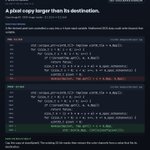
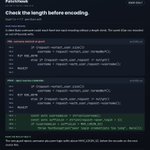


ALT CVE-2026-46675 in libpng. The PRE panel says this helper did not exist in 1.6.58. The POST panel shows the full new function: it sets next_in and next_out to NULL, then avail_in and avail_out to zero. The other card shows where libpng calls it before releasing the stream.

ALT CVE-2026-46675 in libpng. Two stacked code panels show the compressed-text release path. In 1.6.58, it only sets zowner to zero. In 1.6.59, it calls png_inflate_detach_buffers first. The error check above and the end of the block remain visible. For a crafted PNG and a read-end call before any image rows, the old path could use a pointer to freed data.