B. Wolfenden ๐Ÿณ๏ธโ€๐ŸŒˆ (@pwnsolvewin) header
B. Wolfenden ๐Ÿณ๏ธโ€๐ŸŒˆ (@pwnsolvewin) profile picture

Turning cyber into a sport, one competition at a time. Director, Cyber Sports, @KatzcyPlayCyber & @USCyberGames. #cybergames #pwnsolvewin

Denver, CO
Joined June 2022
Photo by B. Wolfenden ๐Ÿณ๏ธโ€๐ŸŒˆ (@pwnsolvewin)Photo by B. Wolfenden ๐Ÿณ๏ธโ€๐ŸŒˆ (@pwnsolvewin)Photo by B. Wolfenden ๐Ÿณ๏ธโ€๐ŸŒˆ (@pwnsolvewin)Photo by B. Wolfenden ๐Ÿณ๏ธโ€๐ŸŒˆ (@pwnsolvewin)Photo by B. Wolfenden ๐Ÿณ๏ธโ€๐ŸŒˆ (@pwnsolvewin)Photo by B. Wolfenden ๐Ÿณ๏ธโ€๐ŸŒˆ (@pwnsolvewin)Photo by B. Wolfenden ๐Ÿณ๏ธโ€๐ŸŒˆ (@pwnsolvewin)Photo by B. Wolfenden ๐Ÿณ๏ธโ€๐ŸŒˆ (@pwnsolvewin)Photo by B. Wolfenden ๐Ÿณ๏ธโ€๐ŸŒˆ (@pwnsolvewin)Photo by B. Wolfenden ๐Ÿณ๏ธโ€๐ŸŒˆ (@pwnsolvewin)
B. Wolfenden ๐Ÿณ๏ธโ€๐ŸŒˆ retweeted
Looking to increase your cybersecurity knowledge, skills, and experience? Explore upcoming cybersecurity training and professional development opportunities for K-12 educators, federal employees, Veterans, and the public on NICCS. niccs.cisa.gov/news-events/fโ€ฆ
4
31
3
128
11,840
B. Wolfenden ๐Ÿณ๏ธโ€๐ŸŒˆ retweeted
Welcome to the Pipeline! 38 athletes are invited to the Season VI, USCG Pipeline Program, our path to future US Cyber Teams. Training runs Janโ€“May 2027. 12 of this year's draftees are Pipeline alumni. Meet the cohort: hubs.li/Q04CV5q10 #USCyberGames #HumanEdge
1
3
111
B. Wolfenden ๐Ÿณ๏ธโ€๐ŸŒˆ retweeted
The results for the ECSC 2026 are in: ๐Ÿฅ‡ Overall: Sweden ๐Ÿ‡ธ๐Ÿ‡ช ๐Ÿฅˆ Overall: Finland ๐Ÿ‡ซ๐Ÿ‡ฎ ๐Ÿฅ‰ Overall: Austria ๐Ÿ‡ฆ๐Ÿ‡น ๐ŸŽฏ Jeopardy winners: Germany ๐Ÿ‡ฉ๐Ÿ‡ช โš”๏ธ Attack & Defence winners: Finland ๐Ÿ‡ซ๐Ÿ‡ฎ ๐ŸŒŸ Best Guest Country: USA ๐Ÿ‡บ๐Ÿ‡ธ
4
27
2,291
Couldnโ€™t be any more proud of the US Cyber Team as they showed off this week in Bochum, Germany, defending our 1st place Guest Bracket finish from 2025! ๐Ÿฅ‡ @USCyberGames
1
21
B. Wolfenden ๐Ÿณ๏ธโ€๐ŸŒˆ retweeted
One day down, more challenges ahead! ๐Ÿ’ป๐Ÿ”ฅ Day 1 of the European Cybersecurity Challenge delivered plenty of action. Here's where things stand after the first round! ๐Ÿ“Š
4
23
1,145
Day 1 of @ECSC_openECSC from Bochum, Germany w. the US Cyber Team is a 12hr CTFโ€ฆ Help cheer us on as we look to defend our 1st place Guest Bracket finish from 2025! @USCyberGames
44
B. Wolfenden ๐Ÿณ๏ธโ€๐ŸŒˆ retweeted
The United States joins ECSC 2026 in Bochum as a guest country. @USCyberGames ecsc2026.de #ECSC2026
3
1
6
294
B. Wolfenden ๐Ÿณ๏ธโ€๐ŸŒˆ retweeted
Today at noon EDT I'm launching a book I've been working on for 20 months: Dynamic Incident Response, an iterative IR framework designed for how security teams actually work. Free in all formats. Join me for the launch today: sans.org/engage/dynamic-inciโ€ฆ
๐Ÿค– Made with AI
1
24
4
63
8,220
B. Wolfenden ๐Ÿณ๏ธโ€๐ŸŒˆ retweeted
Made a Cybersecurity Resume Reviewer AI skill that I've been using for some mentees, made it public for anyone who is interested in using it as well. Hope others find it useful (also open to feedback or pull requests). github.com/mubix/cyber-resumโ€ฆ
12
105
2
523
28,509
B. Wolfenden ๐Ÿณ๏ธโ€๐ŸŒˆ retweeted
I work at GitHub. yesterday was rough and i'm not pretending otherwise. full root cause report is up if you want the timeline and numbers, and what we are doing to prevent this from happening again. githubstatus.com/incidents/zโ€ฆ
281
472
102
5,234
1,276,012
B. Wolfenden ๐Ÿณ๏ธโ€๐ŸŒˆ retweeted
๐Ÿฅ Ducks are invading #DEFCON! Find US Cyber Gamesยฎ at NOOB Village (Aug 7โ€“9) to grab an exclusive duck sticker while they last. ๐ŸŽฎ Learn about Cyber Sports ๐ŸŒŽ Meet the US Cyber Teams ๐Ÿ† Train. Compete. Win. ๐Ÿ“ NOOB Village ๐Ÿ”— hubs.li/Q04qlXMT0 #Cybersecurity #DEFCON34
1
1
158
B. Wolfenden ๐Ÿณ๏ธโ€๐ŸŒˆ retweeted
Lost my phone at the office and spent 30 minutes turning the place over. Find My was disabled by MDM. Out of ideas, I asked Claude how I could find it. It suggested tracking the Bluetooth signal strength, then wrote me a meter in about a minute. I walked around watching the number climb. Found it. Apparently you can just make the tool you need now. Code: github.com/ben-z/findphone
857
4,052
527
47,996
4,047,330
B. Wolfenden ๐Ÿณ๏ธโ€๐ŸŒˆ retweeted
Sometimes I feel silly for not knowing basic things - I always thought etc/group was the only file that had group memberships and when removing users sometimes I would hand-edit this file. If you do this, you are missing one critical piece as there is also the GSHADOW file. If a user is only in that file the id/group command won't show their membership but if that user types `newgrp groupname` it will open a new session with the user being in that group. Found this out when solving Kobold. This was an unintended path as I believe the creator just removed a user from the "Docker" group by editing the file. So later when you get a shell as this user, you can just do the newgrp command to regain docker permissions. I went back and saw this mistake happen on many machines with both docker/lxd groups. Anyways, there's a lot of other cool stuff in the video for the machine, check it out. youtube.com/watch?v=qmkQ6Ighโ€ฆ
5
35
1
373
41,272
B. Wolfenden ๐Ÿณ๏ธโ€๐ŸŒˆ retweeted
Anthropic engineer: "At Anthropic, we donโ€™t write prompts anymore. We build loops." In 45 minutes she shows how the Claude team builds loops that prompt themselves. If this cost $300, people would call it the best agents course of the year. It's free. Watch it, then build your first loop with the step-by-step guide below.
4
34
145
19,464
B. Wolfenden ๐Ÿณ๏ธโ€๐ŸŒˆ retweeted
CrowdStrike ๆœˆๅˆๅ‘่กจblog๏ผŒๆญ้œฒๆ–ฐ็š„ๆ็คบ่ฏๆณจๅ…ฅๆŠ€ๆœฏใ€‚ๆœฌๆฌกๆ–ฐๅขž18้กนๆณจๅ…ฅๆŠ€ๆœฏ๏ผŒ้กน็›ฎ็ดฏ่ฎก่ฆ†็›–200ๅคš็งไธๅŒ็š„ๆณจๅ…ฅๆŠ€ๆœฏใ€‚CrowdStrike AIๅฎ‰ๅ…จ็ ”็ฉถๅ›ข้˜Ÿๅท็งฐ็ปดๆŠคไธšๅ†…ๆœ€ๅคง่ง„ๆจก็š„ๆ็คบ่ฏๆณจๅ…ฅๅˆ†็ฑปไฝ“็ณป๏ผŒๆไพ›ไบ†ไธ€ไธช็ป“ๆž„ๅŒ–็š„ๅฑ‚็บง็ป“ๆž„๏ผŒๆธ…ๆ™ฐ็š„ๅฑ•็คบไบ†ไบบๅทฅๆ™บ่ƒฝๅจ่ƒ็š„ๅ…จ้ƒจ้ฃŽ้™ฉใ€‚
5
167
3
747
40,863
B. Wolfenden ๐Ÿณ๏ธโ€๐ŸŒˆ retweeted
Mondayโ€™s @Google Threat Intelligence report got a fraction of the attention it earned. Call it Salt Typhoon Jr.: a PRC-linked group sat inside North American military research and medical networks for more than a year, undetected, and walked out with the research that decides who wins the next decade. It was easy to miss under the flood of Mythos, Fable, and zero-days-for-days coverage. (Which tells you we still rank threats by how frightening they sound to a general audience, not by what they cost national security.) GTIG tracks the group as UNC6508. Their collection list reads like a tasking order: nearly 150 keywords spanning: Defense intelligence Indo-Pacific operations Artificial intelligence (AI) Uncrewed systems Cyber offensive programs Medical research This was public-health surveillance running inside a military espionage campaign, out of the same institutions, on the same wire. The attackers used a Google Workspace content-compliance rule to silently BCC matching emails to a Gmail account they controlled. Any operator can copy that playbook tomorrow against every university, hospital, and defense contractor running Workspace. This is a clean test case for the question I get in CISO rooms: where would AI have helped the defenders? 1. Admin control-plane monitoring. A brand-new rule that BCC-forwards sensitive mail to a consumer Gmail account should trip an alert the day it is created. That is pattern-spotting across thousands of admin events, which is what a model is good for. 2. Cross-victim correlation. The same campaign hit multiple organizations at once, and each intrusion looked isolated because nobody had visibility across all of them. Correlation across organizations, identity providers, and SaaS logs could have surfaced the pattern months earlier. 3. Behavioral EDR over the dwell window. INFINITERED sat on the REDCap server for more than a year, harvesting credentials, before the attackers used them to pivot into the internal network. That is a long baseline, long enough for behavior-based detection to flag a novel dropper and its callbacks even on malware nobody had seen before. (In theory. In practice, most shops never tuned the baseline.) Where AI would not have helped? What should you do this week? Read here: robtlee73.substack.com/p/salโ€ฆ
3
20
2
52
11,837
B. Wolfenden ๐Ÿณ๏ธโ€๐ŸŒˆ retweeted
โš”๏ธLIVE ATTACK & DEFENSE 10 teams. 1 arena. Infinite bragging rights. ๐Ÿ“HyperX Arena, Las Vegas ๐Ÿ“… August 6 โค๏ธCompete for charity ๐Ÿ”ฅRegister by July 4 to save 20% PLAY. HACK. DONATE. hubs.li/Q04m38Wr0 #USCyberCON #USCyberGames #DEFCON34 #AttackDefense #Cybersecurity
3
1
92
B. Wolfenden ๐Ÿณ๏ธโ€๐ŸŒˆ retweeted
Tonight at 8:30 PM EDT: ๐Ÿ›ก๏ธโš”๏ธ What Blue Teams Wish Red Teams Understood (and Vice Versa) Featuring Rain Baker (@Nightwing), Steven Hullander (@SimSpace), Trey Bilbrey (@SCYTHE), and Jeremy Mill (@VaroBank), moderated by Chris Haller, US Cyber Team Attack & Defense Coaching Lead
1
1
1
146
B. Wolfenden ๐Ÿณ๏ธโ€๐ŸŒˆ retweeted
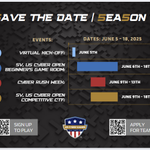
Cyber Rush Week kicks off TONIGHT! ๐Ÿ•ขJoin us at 7:30p Eastern Time | 4:30p Pacific Time for "From Hacking to Hiring: US Cyber Games Talent Night" w/ @Battelle! #uscybergames #cybergames #ctf #seasonvi #womenincyber #Battelle #cyberjobs #cyberworkforce
1
2
1
388
This is cool stuff. @USCyberGames
SANS is hosting a hackathon to dramatically improve forensic analysis tools for AI systems. Sign up now, cash prizes to the most amazing contributions! Start anytime, submit contributions by June 15th. findevil.devpost.com/?is=dddโ€ฆ
3
23