




Rey Bango retweeted

See Empire C2 in action in Part 3 of the DarkHaven Range walkthrough with @reybango and Jake Krasnov 🎉
Watch how Empire is run through a live target environment:
youtube.com/watch?v=bkHhwzKt…
#EmpireC2 #RedTeam #CyberSecurity

php2shell is no joke and is being compared to log4shell in terms of severity. CVE-2026-109618 and CVE-2026-109619 are critical (CVSS 9.2) vulnerabilities in PHP that can allow unauthenticated remote code execution.
It’s also reported that these are under active exploitation!!
The best solution is to upgrade to PHP 8.2.35, 8.3.36, 8.4.27, or 8.5.12, or install distribution or LTS vendor packages containing the fixes. Please do this ASAP and stay safe!
You can read the Horizon3.ai advisory here: horizon3.ai/attack-research/…


Rey Bango retweeted

Railway is compromised, rotate all API keys as soon as possible
Deployments are down so don’t wait to redeploy
Attackers are draining keys in real time, we didn’t lose much but can confirm this is still an active attack
Stay safe friends


Rey Bango retweeted

🚨 BREAKING: Node.js just dropped its OWN security bombshell.
4 HIGH-SEVERITY vulnerabilities patched TODAY, including one that could let hackers remotely execute malicious code on vulnerable servers.
→ 10 SECURITY FLAWS were addressed in today's Node.js release, FOUR rated HIGH severity.
→ REMOTE CODE EXECUTION: CVE-2026-111497 is a serious flaw in Node.js's Brotli decoder that could allow attackers to execute malicious code remotely.
→ TLS SECURITY BYPASS: Two separate vulnerabilities could trick affected applications into accepting certificates for the WRONG server under certain conditions.
→ Think about that. Your application could establish an encrypted connection while failing to properly verify WHO it's talking to.
→ THREE MAJOR NODE.JS VERSIONS AFFECTED: Node.js 22, 24 and 26 all required emergency security updates.
→ RUNNING NODE.JS 18 OR 20? Those versions are END-OF-LIFE and aren't receiving these official security patches.
→ PATCH IMMEDIATELY: Update to Node.js 22.23.4, 24.22.1 or 26.12.1, depending on your release line. If you're using Docker, rebuild and redeploy your containers.
PHP AND Node.js both facing major security disclosures on the SAME DAY.
If you run a website or application, TODAY is the day to check your servers.
And remember: the public release of security patches can give attackers a roadmap to systems that haven't updated.
Don't be the last one to patch.

🚨 A MASSIVE internet security emergency is unfolding right now. 🚨
Two CRITICAL vulnerabilities have been discovered in PHP, potentially putting millions of websites at risk.
→ NEARLY 70% of websites with a known server-side language run PHP. The potential scale is ENORMOUS.
→ TWO CRITICAL security flaws have been confirmed, each scoring 9.2/10 in severity.
→ Attackers could potentially take control of vulnerable servers remotely, without authentication.
→ Reports suggest PHP versions dating back to 2004 could be affected. The exact scope is still unconfirmed.
→ EMERGENCY PATCHES are scheduled for TOMORROW at 10 AM ET. Website owners are being urged to prepare immediately.
→ Europe's CERT-EU is warning organizations to patch ASAP or consider TAKING EXPOSED APPLICATIONS OFFLINE if they cannot be secured.
→ WordPress, Magento, Laravel and potentially millions of other PHP-powered websites could be at risk.
→ Once patches go public, hackers could reverse-engineer them and race to attack servers that haven't updated.
The vulnerabilities are CONFIRMED. The full technical details remain secret.
Tomorrow, the race between hackers and defenders begins.
This could get ugly. FAST.
Rey Bango retweeted

Effective Immediately, all organizations using PHP for their systems are advised to be prepared for an update addressing two critical vulnerabilities. PHP is widely used for web applications. These vulnerabilities often provide a direct path to the server's file system or database. If an immediate update is not feasible, it is recommend that organizations take the system offline until it can be fully mitigated. NSA will follow up shortly with more specific guidance.

Clever use of common area for promoting security. Never seen this before. Well done @_GuidePointSec 👍👍
#gpsec

Part 3 of using the Empire C2 on Hack Smarter's DarkHaven range is now out. Once again I partner with @_Hubbl3 on how he would approach this Active Directory cyber range from Hack Smarter Labs as a red team operator. In this video we dive more into on-box recon, password cracking and payload obfuscation.
In addition, Tyler Ramsbey has generously donated a 12 month All Access voucher which I've added into the video as a giveway!
Go check out the vide here:
youtu.be/bkHhwzKtT8I
🤖 Made with AI


Rey Bango retweeted

Check out our latest deep-dive for #AhsayCBS, an enterprise backup solution.
Reported as exploited in-the-wild by @HuntressLabs, CVE-2026-105133 and CVE-2026-105134 allow an unauthenticated attacker to execute commands as SYSTEM or root on the server.
horizon3.ai/attack-research/…

Rey Bango retweeted

Rapid Response Threat Advisory
The Horizon3 Attack Team is currently investigating CVE-2026-105133 and CVE-2026-10534. These vulnerabilities, when chained, can result in remote code execution on AhsayCBS (Cloud Backup Server).
More info to come.


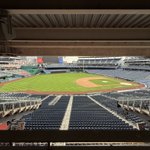
The view from the @Horizon3ai Attack Path Tour in Washington DC is incredible!!
Hacking and baseball make for a great event!! ⚾️⚾️⚾️😈😈😈


Rey Bango retweeted
Part 2 of our Empire C2 series with @reybango is up, featuring a special giveaway! 🎁
Watch the latest demo, then check the caption to find out how you can win a Hack Smarter All-Access Voucher!
youtube.com/watch?v=HA_bMzlR…
#redteaming #empirec2 #infosec

Using the Empire C2 on Hack Smarter's DarkHaven Range - Part 2 is now out. Once again I partner with @_Hubbl3 on how he would approach this Active Directory cyber range from Hack Smarter as a red team operator.
In addition, @Tyler_Ramsbey has generously donated a 12 month All Access voucher which I've added into the video as a giveway!
Go check out the vide here:
youtu.be/HA_bMzlRJ9Y
@EmpireC2Project @bcsecurity

Rey Bango retweeted

New: from 404 Media. The catastrophic FBI hack also exposed the FBI's own hacking unit. The Remote Operations Unit is a highly secretive part of the FBI, responsible for making tools to break into peoples' devices. Some of their names are in the data 404media.co/fbi-hack-exposed…
