

Secure Cyber Defense is a global Cybersecurity consulting and solutions provider firm.
Miamisburg, OH
Joined May 2015
- Tweets1K
- Following196
- Followers283
- Likes501




Could your organization keep operating if your usual systems went down?
Imagine starting tomorrow with no email, no shared files, and no access to the software your team relies on.
Who would make decisions? How would employees communicate? Which services would need to continue, and what approved backup procedures could your team safely use?
This Cybersecurity Awareness Month, go beyond asking, “How do we prevent an attack?” Ask “Have we practiced what happens next?”
Start with a response plan that clearly identifies responsibilities, includes an alternative way to communicate, and is accessible even when your network is unavailable. Test your backups, too. Having a backup is not the same as knowing you can restore what you need.
Set aside time this week to walk through a hypothetical outage with your team. Discuss what would stop, who would take action, and what needs to improve. Practicing your response is part of being prepared, not something to save for an actual emergency.
The goal is more than getting computers back online. It is protecting the services people depend on.
Small Steps. Stronger Communities.
#CybersecurityAwarenessMonth #SecureCyber #Cybersecurity #BusinessContinuity #IncidentResponse

Still tapping “Remind me later”? This is your reminder. 🔔
Software updates do more than add features or change how an app looks. They often fix security weaknesses that criminals can exploit. Putting them off can leave those weaknesses unaddressed.
This Cybersecurity Awareness Month, give your family’s devices a checkup. Look for updates on your phones, laptops, and tablets, and enable automatic updates where available. Don’t forget your home router and smart devices. They need attention, too.
One important reminder: Check for updates through your device’s settings or the manufacturer’s official website. Don’t install an “urgent update” from a link in an unexpected email.
Make checking for updates part of your weekend routine, and help someone in your household do the same.
Small Steps. Stronger Communities.
#CybersecurityAwarenessMonth #SecureCyber #CybersecurityAtHome #OnlineSafety

Our CEO, Shawn Waldman, recently spoke at the Ohio Rural Water Association Fall Expo and an OAWWA event, sharing lessons from recent cyberattacks and practical steps water and wastewater teams can take to protect their operations.
Thank you to both organizations for welcoming Shawn and to everyone who joined the conversation! We’re proud to support the people who keep our communities’ water flowing.
#SecureCyber #ORWA #OAWWA #WaterUtilities #Cybersecurity


PHP2Shell needs your IT team’s attention.
Two critical PHP vulnerabilities could put websites and business applications at risk. Our latest blog explains who is affected, what steps to take now, and how SecureCyber is helping protect customers.
Read the full breakdown: PHP2Shell: What You Need to Know and What SecureCyber Is Doing: hubs.ly/Q04BV5M50
#SecureCyber #PHP2Shell #Cybersecurity

Did you know SecureCyber does incident response?
Watch this short video to learn more!
#Ohio #IncidentResponse #cybersecurity #SecureCyber #LocalGov
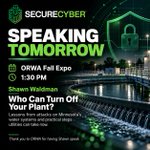
Our CEO, Shawn Waldman, is speaking at the ORWA Fall Expo tomorrow at 1:30 PM!
His session, “Who Can Turn Off Your Plant?”, covers lessons from attacks on Minnesota’s water systems and practical steps operators can take to protect their facilities, regardless of size or budget.
Thank you to ORWA for having Shawn out to speak. We’re looking forward to connecting with everyone!
#SecureCyber #ORWA #WaterUtilities #Cybersecurity #OTSecurity

🎃 Scammers wear disguises, too. And AI can help make them more convincing.
AI generated images, fake reviews, and bogus celebrity endorsements can make fake product listings look legitimate. What looks like an amazing deal could be a counterfeit product, something nothing like the photo, or an order that never arrives.
A convincing picture is not proof of a real product.
Before you click “Buy”:
🔎 Research the seller and check reviews outside the listing.
🛒 Compare prices and read the return policy.
💳 Pay with a credit card when possible. Avoid sellers who insist on gift cards, wire transfers, or cryptocurrency.
This Cybersecurity Awareness Month, SecureCyber’s reminder is simple: keep the tricks in your Halloween celebrations, not your shopping cart. 👻
#SecureCyber #CybersecurityAwarenessMonth #AIScams #OnlineShoppingSafety #Halloween

We’re grateful to OAWWA for having Shawn out to speak today!
His session will break down what happened during this summer’s attacks on U.S. water and wastewater systems, how attackers gained access, and the practical steps utilities can take right now to reduce risk.
It is an important conversation for any organization responsible for critical infrastructure!
#SecureCyber #OAWWA #WaterUtilities #Cybersecurity #CriticalInfrastructure #OTSecurity

SecureCyber is proud to be listed as a supporter of OpenAI’s call for collective cyber defense!
This initiative calls on cybersecurity companies, technology leaders, and governments to work together, share knowledge, and put better AI tools in the hands of the teams protecting our businesses and communities.
Why does this matter? As attackers gain more powerful AI capabilities, defenders need better resources too. The effort emphasizes support for water utilities, hospitals, local governments, and other essential services with limited security staff and budgets.
We’re proud to support that mission. Protecting the systems our communities depend on takes all of us working together.
#SecureCyber #OpenAI #CyberDefense #CriticalInfrastructure #Cybersecurity

The request is urgent. That doesn’t make it real. 🚩
“Update your payment details today.” “Your account will be locked unless you act now.”
An urgent request is not automatically a scam. But scammers use pressure and familiar names to make you act before you question what you’re being asked to do. A message that appears to come from your boss or a trusted vendor still deserves verification.
This Cybersecurity Awareness Month, remember three words: Pause. Verify. Report.
Pause before clicking a link, opening an unexpected attachment, or sharing information, take a moment. Do not let someone else’s deadline push you into skipping your organization’s security procedures.
Verify. Confirm unusual requests through a separate, trusted channel. Call the person using a number you already have, not one supplied in the suspicious message. Be especially careful with changes to payment details.
Report. Use your organization’s reporting process to alert your IT or security team. You do not need to be certain a message is malicious before raising a concern.
Share this reminder with your team, and make sure everyone knows where to report
something suspicious.
Small Steps. Stronger Communities.
#CybersecurityAwarenessMonth #SecureCyber #PhishingAwareness #Cybersecurity

A strong password is a start. It should not be your entire defense.
For this week’s Cybersecurity Awareness Month tip, start with your accounts. Use a long, unique password for each one and a company-approved password manager to create and store them. Reusing the same password means one exposed password could put multiple accounts at risk.
Then add multifactor authentication, or MFA. That extra verification step, such as a code from an authenticator app, helps protect your account even if someone steals your password.
Here’s one question to ask your IT team this week: “Which of our important accounts still rely on a password alone?”
Small Steps. Stronger Communities.
#CybersecurityAwarenessMonth #SecureCyber #Cybersecurity #MFA

October is Cybersecurity Awareness Month. Let’s turn awareness into action. 🔐
This month at SecureCyber, our focus is simple: Small Steps. Stronger Communities.
Throughout October, we’ll share practical ways to protect your accounts, recognize suspicious requests, keep technology supported, and prepare for disruptions. You’ll also meet some of the people behind the work and hear their advice.
Because cybersecurity is about more than protecting computers. It’s about keeping water flowing, businesses operating, and essential services available to the people who depend on them.
Follow along this month, share these tips with your team, and put them into practice.
#CybersecurityAwarenessMonth #SecureCyber #Cybersecurity #CriticalInfrastructure

Congratulations to our CEO, Shawn Waldman, on being named one of The 25 Leaders Protecting Ohio’s Digital Future.
This recognition highlights the important work being done across Ohio to protect businesses, public services, critical infrastructure, and the communities that rely on them every day.
At SecureCyber, we see firsthand how important cybersecurity leadership is, especially for organizations like local governments, water and wastewater utilities, and other critical infrastructure sectors. Shawn’s commitment to threat hunting, incident response, education, and strengthening Ohio’s cyber readiness continues to make a real impact.
We are proud to see his leadership recognized alongside so many others working to protect Ohio’s digital future.
Congratulations, Shawn!
Read the full article here: hubs.ly/Q04zb3Bv0
#SecureCyber #Cybersecurity #OhioTech #CyberLeadership #CriticalInfrastructure #IncidentResponse #CyberDefense

When we got the call asking if SecureCyber would host a delegation of Ukrainian leaders, the answer was an easy yes. What took longer to sink in was what it meant.
The group was visiting Ohio through the Congressional Office for International Leadership (COIL), a program of the U.S. Congress that brings emerging leaders from other countries to see how Americans work in their own communities. Their Dayton-area hosts reached out and asked us to be one of their stops, alongside the University of Dayton.
That is a humbling request for a company our size. It says something about the work our team does every day, and it says something about Dayton as a place where cybersecurity is taken seriously.
But honestly, I think we walked away with more than we gave.
Ukraine has lived through cyber attacks that most of the world has only read about, including attacks that turned off the lights in the middle of winter. Sitting across the table from people who have defended their country under that kind of pressure changes how you think about your own work.
Thank you to COIL, Grant Neeley, and the University of Dayton for trusting us with this visit. And thank you to the entire SecureCyber team for their support and participation.
Дякую.


Thank you to the Cincinnati Area Manager’s Association for inviting our CEO, Shawn Waldman, to speak on AI and policy risk.
AI is moving quickly, and organizations of every size are having to think through what it means for security, policy, operations, and leadership. Conversations like this are important because they help leaders better understand the risks, ask the right questions, and prepare their teams for what is ahead.
We appreciate everyone who attended, asked questions, and took part in the discussion. Thank you again for having SecureCyber be part of it!
#SecureCyber #AI #Cybersecurity #PolicyRisk #Leadership #CyberAwareness

Please join us in welcoming Adam Thomas as SOC Manager!
Adam’s leadership, technical knowledge, and dedication to supporting our clients make him a great fit for this position. We are excited to see the continued impact he will have on our SOC team and the organizations we protect every day.
Congratulations, Adam!

We are excited to highlight Tidiane in his role as SOC I Analyst!
Our SOC team plays a critical role in monitoring, detecting, and responding to threats for our clients, and we are grateful to have Tidiane as part of that mission.
Congratulations, Tidiane!

Congratulations to Marcus Childs Taylor on his role as Lead SOC Analyst!
Marcus brings strong technical skill, focus, and commitment to the SecureCyber SOC. We are excited to recognize his growth and the important role he plays in helping our team detect, respond, and protect our clients.
Great work, Marcus!

Please join us in congratulating James Fisher on his role as Cybersecurity Advisor!
James will play an important role in helping organizations better understand their cybersecurity needs, identify areas of risk, and find the right path forward.
We are excited to see the impact he will make in this role. Congratulations, James!

As we head into Labor Day, we want to take a moment to recognize the people who make SecureCyber what it is.
Our team works hard every day to support our clients, protect the communities they serve, and keep important systems secure. From our SOC analysts and engineers to our sales, operations, leadership, and support teams, every person plays a role in the work we do.
This week, we are dedicating our content to celebrating some of the people behind SecureCyber, including new team members and recent role changes.
We are grateful for our employees, their hard work, and the impact they make every day.
Be on the lookout this week as we highlight a few of the great people on our team.
#SecureCyber #LaborDay #EmployeeAppreciation #TeamSecureCyber #WorkplaceCulture #Cybersecurity
