

· Software Engineer · Musician · Technology Communicator · DM for collaborations 📧 [email protected]
London
Joined September 2013
- Tweets15.9K
- Following296
- Followers2.2K
- Likes80.1K





Pinned Tweet
🧑🏼🏫APRENDE PROGRAMACION GRATIS CON MIS VIDEOS
🔸 HTML: youtube.com/watch?v=bNV6iw13…
🔸 CSS: youtube.com/watch?v=rTtC6Q-7…
🔸 JAVASCRIPT: youtube.com/watch?v=N8Xt5rP_…
🔸 REACT: youtube.com/watch?v=ladwC6Lr…
🔸 TYPESCRIPT: youtube.com/watch?v=UTA5bykC…
🔸 ANGULAR: youtube.com/watch?v=soInCF7n…
🔸 GIT Y GITHUB: youtube.com/watch?v=7ylE8cm3…
🔸 NODE JS: youtube.com/watch?v=I17ln313…
🔸 JAVA: youtube.com/watch?v=BdNqW63Z…
🔸 PYTHON: youtube.com/watch?v=_uPVSW0c…
y mucho más
#cursogratis #cursosgratis #cursos #tutorial #html #css #js #javascript #typescript #react #reactjs #angular #git #github #nodejs #node #java #python #frontend #backend #fullstack #fullstackdeveloper

¿Síndrome del impostor? Amigo, despreocupate, este "experto en ciberseguridad" no sabía lo que era PHP y estaba dando consejos en la BBC

Hasta el FBI! Lo que se viene en los próximos meses en Ciberseguridad es duro

The FBI continues to warn about two critical security flaws in PHP, a programming language used to build many websites and online services. Attackers could exploit these vulnerabilities to break into systems, putting sensitive information and business operations at risk. Security updates are available and should be applied immediately.
If you are a business owner or website operator, check whether your systems are affected. Contact your IT support team, website developer, or hosting provider for help identifying vulnerable systems and applying the necessary updates.
The FBI urges organizations to take the following steps now:
➡️ If an immediate update is not feasible it is recommended that organizations take the system offline until it can be fully mitigated.
➡️ Immediately update affected PHP installations following the guidance on php.net. Inventory where PHP runs in your environment, prioritizing internet-facing systems and vendor products that bundle PHP.
➡️ Monitor web servers for suspicious activity, including PHP processes unexpectedly launching command shells or downloading files. Ensure appropriate process-monitoring capabilities are in place to help identify potential exploitation.
➡️ If you find signs of compromise, isolate affected systems, preserve your web server and PHP logs, and report it to your local FBI field office or ic3.gov. Those reports help us identify the actors involved and warn other organizations before they become victims.
For the latest information on these vulnerabilities (CVE-2026-109618 and CVE-2026-109619), follow PHP’s announcements on php.net, CERT-EU Security Advisory 2026-018, and CISA’s Known Exploited Vulnerabilities catalog.

ALT Critical vulnerability alert for PHP Core with CVE-2026-109618 and CVE-2026-109619, CVSS score 9.2, urgent patch required.
HAHA this is the most British joke I’ve ever laughed at

Philomena: Some people have been writing PHP for over 20 years. Is that because it's particularly difficult to finish?
Expert: No, software is constantly evolving.
Philomena: So they've been writing the same website for 20 years?
Expert: No, different projects.
Philomena: Have they tried finishing one before starting another?
Expert: That's not how software development works.
Philomena: My mate Paul spent 20 years building a shed. Turned out he was just an alcoholic.
Expert: Right.
Philomena: Is PHP like that?

Mi hermana tiene un perrito nuevo y me hizo acordar al gatito que falleció antes de venirme a Londres uff me partió al medio
Yo matandome para conseguir una entrevista en la BBC y llaman a este que hasta ayer no sabía lo que era PHP
🎩✨Thanks for sharing our last song, "You Loved The Cage" by Spinors!

Discover "You loved the cage" By Spinors
#music #ArtistsOnTheRise #IndieVibes #MusicalMinds #Soundscapes #MusicMonday #NewMusicFriday #IndieArtists #MusicDiscovery #ArtistSpotlight #IndieArtistry #Vikings #Cheers #DiscoverNewMusic
cheerstothevikings.com/2026/…

eMudhra es la empresa india que cometió el error de seguridad: se dedica, entre otras cosas, a emitir certificados digitales q permiten q los navegadores comprueben q una web es confiable, y una de sus claves secretas era simplemente el número 4 en lugar de un clave compleja

Siempre le mandas la conversación entera cuando superas la cantidad de tokens que puede procesar tenes que compactar la información y enviar el resumen mas el nuevo mensaje


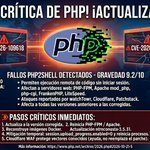
⚠️ PHP2Shell: actualizá PHP hoy.
PHP publicó parches de emergencia para dos vulnerabilidades críticas (CVE-2026-109618 y CVE-2026-109619), con gravedad 9.2 sobre 10. Permiten que un atacante ejecute código de forma remota en servidores web sin necesidad de iniciar sesión

🔴 Afecta a toda instalación de PHP que atienda peticiones web: PHP-FPM, Apache con mod_php, php-cgi, FrankenPHP y LiteSpeed. Los más expuestos son quienes usan mod_php
Que maravilla esto! Muchos recuerdos!

I took apart the music of Prince of Persia (DOS, 1990) note by note.
22 original MIDI files, played through the game's own AdLib patches, turned into a free 15-step tutorial: from one note to your own cutscene.
Music by Francis Mechner, game by @jmechner
🎩✨ Thank you very much for sharing our last single "You loved the cage" by Spinors!

Two people. One cage. One way out. ⚛️ Spinors on "You Loved The Cage": the video's twist, steampunk, and who we're meant to side with. #AlternativeRock #Spinors Full interview on Soundevote 🎤 soundevote.com/post/spinors-…

🎩✨ Thank you very much for sharing our last single "You loved the cage" by Spinors!

Discovery: Spinors Reveal Heartbreak In Alternative Rock Single yorkcalling.co.uk/2026/10/19…


Many thanks for sharing our new single!

Spinors [@sergiecode] Explore Addiction, Heartbreak, and Freedom in “You Loved the Cage”
musicearshot.com/2026/10/spi…
