

Making software security autonomous. Free for open source. (YC W24)
San Francisco
Joined May 2023
- Tweets813
- Following27
- Followers2.7K
- Likes847



Capchase runs the gold standard playbook for how to secure their stack in the new age of cyber attacks.

We flew down to Spain, got kicked out of the connecting flight. Drove 6h in the middle of the night to meet with our customer.
@Capchase is a New York-based fintech that helps software and hardware vendors offer flexible payment terms.
Their team uses @superagent_ai to automate their security work.
BIG NUMBERS
Wow! @superagent_ai just crossed 100K red-team runs across over 4000 code bases (gray) and applications (black).


Superagent retweeted

It is tough these days to build secure software - especially if you are under a major attack like OpenCode. So I feel for them and they build great product.
But this is another example of why you should use a model like Dotenvx or SOPS. Split your secrets cryptographically so that an attacker has to attack both the providers secret store (in this case that is what was attacked) AND the encrypted secret in your code (which was not attacked or even reachable here).
This is why we wrote our whitepaper. Meanwhile, every other provider retweeting OpenCode and saying 'use our secrets store' is repeating the same systematic problem - centralizing your secrets to their secrets store yet again.
Dotenvx or solutions like SOPS are the only way to solve this for your organization.
xitter.cf/opencode/status/211151…

We had a security breach last night related to a large scale distillation attack that impacted 1.4% of OpenCode Console users
We have notified them all this morning via email. If you did not get an email you were not impacted, it was a subset of users who had external providers linked
The incident is ongoing so we cannot share more details at this point but we are working with Anthropic, OpenAI, and Google to remediate
Superagent retweeted
Huge milestone for @papercliping. Very excited to support them!

One hundred thousand Github Stars!!
This makes Paperclip one of the top 150 open-source projects of. all. time.
All computer work is becoming agentic work so you need tools to harness the army of agents at your disposal
We've built 📎 for companies to get a handle on agent sprawl and it's popular is because it's good
Paperclip is multi-player and you can use any model, any harness, any time. It's the layer for every connection, every agent, and every human to collaborate on work
The self hosted version is completely free (and you can sign up for the waitlist for the hosted version)
📎📎📎 ITS TIME TO CLIP 📎 📎📎
Superagent retweeted

🔥 Official London 🇬🇧 Agent Week is here.
🗓️ Tue 13 Oct: Interrupt by @LangChain at Outernet London. @hwchase17 and the team are bringing the agent conference to the city with workshops and production stories.
🗓️ Fri 16 Oct: Agent Engineering, London by @AgentEngHQ bring together CEO/CTO and leaders from Agent Infra companies from UK 🇬🇧 and Europe 🇪🇺
@samuelcolvin @abreslav @pelaseyed @tobiemh @jonbratseth @MeryemArik9 @bartheletf @sbichenko @Jocelyn_K_DArcy and more
🍕🍻Plenty more meetups and workshops across the week too.
If you are an agent builder, you should be in London this week.
Open-source is the backbone of every major technological leap. That's why Superagent is completely free for open-source while others just try to sell tokens.

SOTA for everything security
security-one is the strongest cyber decision model 🙌
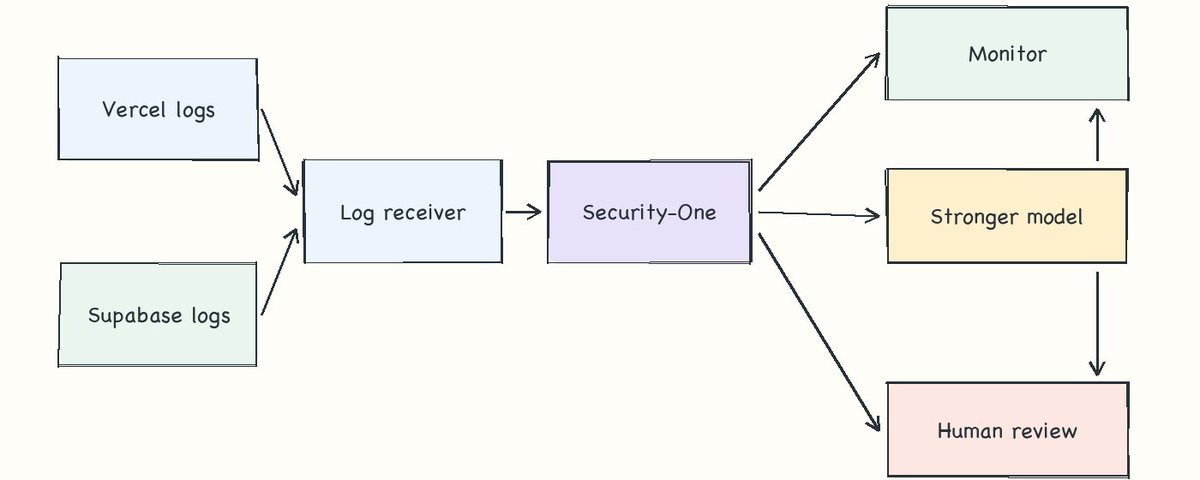
Most security signals do not need to be sent directly to a large frontier model. security-one is designed to operate continuously, classifying activity, identifying suspicious behavior and escalating the cases that require deeper analysis to a stronger model or a human.

Superagent retweeted
🎙️ 🇸🇪 Meet the Speaker Ismail Homan Pelaseyed @pelaseyed : Co-founder & CTO, Superagent @superagent_ai
Ismail is building at the intersection of AI agents, developer infrastructure and security. At Superagent, he is focused on security for AI-native developers helping teams control what agents can do, protect the context they consume, and secure the software they generate and modify. He will be talking about security for developer in his talk that you should not ignore:
🎙️ Security for AI-Native Developers
He is coming all the way from Sweden 🇸🇪 to meet you all. Please engage with him and learn the tips and tricks about securing AI applications.
📍 Everyman Canary Wharf, London
📅 16 October 2026
🎤 Ismail Homan Pelaseyed: Co-founder & CTO, Superagent
💡 Security for AI-Native Developers
🙏 Join us at Agent Engineering London 🇬🇧
👉 agentengineering.world/


security-one is built to run 24/7. This was achieved by working hard on bringing down latency and cost so it becomes viable for teams of all sizes to run it.
AI for defense has to diffuse into every part of your stack to be truly effective against adversaries. It also has to be open-source/weights.
huggingface.co/superagent-ai…

Superagent retweeted

I was curious to see when dm-based always-on security triage would appear.
And, unsurprisingly 👇
I'm super excited to introduce security-one: our open-weight model for security decisions.
Designed to:
✅ Run 24/7
✅ Assess signals across apps, agents and infra
✅ Return structured probabilities to guide routing
✅ Route suspicious events to stronger models/humans
huggingface.co/superagent-ai…
Superagent retweeted
I'm super excited to introduce security-one: our open-weight model for security decisions.
Designed to:
✅ Run 24/7
✅ Assess signals across apps, agents and infra
✅ Return structured probabilities to guide routing
✅ Route suspicious events to stronger models/humans
huggingface.co/superagent-ai…
Today we are releasing security-one: a system one model trained to catch attacks across agents, infrastructure and applications.
security-one is designed as an always-on that protects your stack from the Hugging Face incident.


Superagent retweeted
Faster than Node's native parseEnv?
No, way.
Yes. Yes, way.
Dotenv's fast mode now beats Node's native parser on Node 22 and 24 across Linux and Windows in our benchmarks.
Five months ago, the wildest PR ever landed in dotenv. Most contributions are small parser changes, type fixes, or feature proposals.
This was a new parser, claiming 2x speedup.
Some guy from Sweden, @pelaseyed. A character scanning approach. Pretty sick, tbh.
So what did I do? What any maintainer does for a package depended on by tens of millions.
I sat on it. lol.
But we also got in touch. He and his cofounder run @superagent_ai, securing PRs. They generously offered to secure Dotenvx's, and today they do that for all kinds of open source projects—even Firecrawl.
Back to Dotenv. The parser was contributed as a full replacement. That's too risky, so we put it behind a fast flag.
On September 17th, five months after that initial PR, we released it.
It's fast.
With dotenv 18 or later:
require('dotenv').config({ fast: true })
Or from the CLI:
npx dotenv run --fast -- node index.js
The community has already found edge cases, and we've patched them. That's exactly why we made it opt-in.
Node's native parser still wins in some configurations. Full benchmark breakdown in the post below.
Maintaining dotenv means maintaining the past while still moving .env forward. This parser is a small piece of that.
Huge thank you to @pelaseyed and @superagent_ai for bringing it to the dotenv community.
dotenvx.com/blog/2026/09/28/…

Superagent retweeted
🦾 Proud to share this: London 🇬🇧 Agent Engineering Conference (AgentEng): the agenda is LIVE! 🍾 @AgentEngHQ
🙌 Excited to unveil the final speaker lineup for the founding edition of Agent Engineering London, bringing together the companies building the infrastructure, platforms and systems behind the next generation of AI agents.
✨Our speakers include CEOs, CTOs, founders and engineering leaders from leading Agent Infrastructure companies and labs across the UK 🇬🇧 and Europe 🇪🇺.
For our founding edition, wanted to keep AgentEng intentionally lean: limited seats, a curated audience, a single track and high-signal conversations.
🎙️Incredibly excited to welcome our 10 speakers:
@samuelcolvin : CEO @pydantic
@abreslav : Founder @codespeak_dev
@pelaseyed : CTO @superagent_ai
@tobiemh : CEO @SurrealDB
@sergey__ignatov : Director of Engineering @jetbrains
@jonbratseth : CEO @vespaengine
@MeryemArik9 : CEO @Doubleword_
@bartheletf : CTO @alpic_ai
@sbichenko : CEO @RecombineAI
@Jocelyn_K_DArcy : CEO @Poindexter_Labs
🙏Thank you to all of our speakers and their teams for joining the founding edition.
😅 A lot went into shaping this first edition and the hardest part was curating the speaker lineup.
If you’re building AI agents, agent infrastructure, developer tooling or production AI systems, join us in London and be part of the founding Agent Engineering Conference.
Speakers 🎙️, Agenda 🗓️ and ticket 🎟️:
👉 agentengineering.world
🗓️ 17 days to go and seats are limited
New milestone unlocked: 4,000 code bases connected to our Security Factory.
Firecrawl, Mastra, Nango, OpenRoll, Capchase and thousands more have deployed our autonomous security workers to their apps, repos, agents and infra.
Thanks for trusting us 🫶
Superagent is free for open-source maintainers. Get access here: superagent.sh
This is the fruit of many discussions with developers over the past week.
The number of dependency updates have led to dependency fatigue coupled with fear of getting hacked through a supply-chain attack.
Secure Dependency Updates fixes that

Instead of flooding you with bump PRs we run a second security pass to make sure the update doesn't contain any phishy/vulnerable updates.
If everything is 🟢 we make a bump PR and send out a ping to your coding agent. Your coding agent then runs integrity and integrations tests before merge.
We wrote a tutorial on how to setup secure dependency updates with @cognition Devin to help you get started. As always, this is free fro open-source:
superagent.sh/docs/use-cases…