

schizo - market maker trust no 1
earth
Joined May 2025
- Tweets2.8K
- Following306
- Followers352
- Likes2.6K






Noid built on rust

They already have quantum comupters buy noid

Last night, three of my wallets were drained. I still don’t know exactly how this happened or what the attack vector was.
Over the past week, we’ve seen multiple security incidents and vulnerabilities being discussed across the industry, including PHP-related security concerns and other potential exploits. I don’t know whether any of these incidents are connected to what happened to me.
The amount involved is significant, and honestly, I’m struggling to process what has happened. I’ve spent years in this space, and experiencing something like this is absolutely heartbreaking.
Right now, I’m trying to trace the transactions, investigate the affected wallets, and understand how my security was compromised.
If anyone has experience with wallet drainers, compromised devices, malicious browser extensions, or on-chain investigations, please reach out to me via DM. Any genuine help in identifying the source of this attack would mean a lot.


yo the NoidGuy retweeted

I think he got this backwards.
Crypto is the only industry that is guaranteed to survive.
I am not saying it will be smooth sailing.
What I am stating is that:
1. It has been battle tested for 10+ years.
2. It does not rely on the same standards as the rest of the Internet (CAs, php, etc.).
3. It operates within its own protocols. It shares the same fabric as the rest of the Internet but it is its own thing.
When the whole world begins to burn down, when banks start failing, the only place to run to will be crypto.
It's almost payback time, folks, for all the crap we've endured for the last 5 years.


Every cloud will do the same eventually
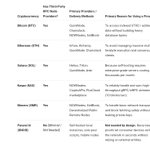
Now tell me what are the coins that rely on rpc valditors?


【速報】GMO、パソコン電源落とすよう呼びかけ
news.jp/i/148762435443094372…


Same happening with banks is now happening to crypto
Return to decentralization

Hackers managed to steal authentication keys for devices made by @KeystoneWallet
I don't understand one thing here however. During manufacturing, as part of the factory self test in initial boot you have the device generate & save a private key on its own, and take note of the public key.
If you have private keys to be stolen, it means that *somehow* a copy of the key exists outside of the secure element on the device?
If the manufacturing process involves each device's private key existing outside of the device, there's something that needs urgent improvement. Have the device generate the key and include its own public key as part of its self test report, not the other way around.
xitter.cf/tayvano_/status/211475…


Money in history
Trading goods ---> silver & gold ---> bank notes ---> digital money ---> bitcoin --> eth ---> $noid
This is exactly how i would describe noid to anyone
Humanity doesn't stay the same we evolve we went from riding hourses to walk on the moon .
Thinking that sol eth or any major is the future is so wrong .
With technology getting advanced every second ai superintelligence quantum computing the money evolve with it aswell .
My price target for $noid is way ahead from anyone out there.