

Information Security Audits, TSMC, ELINT, OSINT, SIGINT, System Integration, Digital Forensics, MSSP.
India
Joined October 2018
- Tweets420
- Following612
- Followers112
- Likes1K




Threat actor selling 0 day exploit for Chromium browser on Android 14 to 16. Exploit RCE to infect the Android once the user visits a malicious webpage/advertisement loaded/webview used by a third party app. No user interaction required.
#0days #exploit #remotecodeexecution

Pakistan based threat group named EvilMarkhors allegedly leak 50 GB of data, threatens to leak another 1.8 TB. The threat group claims the data is collection from military, police and government institutions.
#databreach #criticalinformation #CyberSecurity

Chinese EV charging service provider named NIO Power, allegedly breached and data put on sale. 850,000 PII records of customers in leak.
#databreach #electricvehicles #CyberSecurity

Threat actors allegedly puts Huazhu Hotel, customer data on sale. There are approximately 311 million records in the leak.
#databreach #hotels #reputationdamage

Scarlett ransomware group breaches Rajasthan Police portal and puts extracted sensitive data on sale.
#ransomwareattack #poliçe #CyberAttack

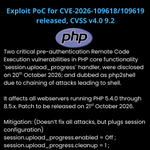
Exploit PoC for CVE-2026-109618/109619 released, it has a severity of CVSS v4.0 9.2. Affects all webservers running PHP 5.4.0 to 8.5.x, patch to be released on 21st Oct 2026. Dubbed as php2shell, attack chaining leads attacker to gain shell access.
#exploit #vulnerability #rce

Pakistani threat actor defaces Chhabua Municipal Board website, allegedly extracted data.
#geopolitics #defacement #CybersecurityAwarenessMonth

Threat actor allegedly leaks 375,000 records of SBI customers, including 2722 PDF documents. Analysts discover ERROR messages in leaked data.
#banksecurity #databreach #cybersecurity

Threat actor claims access to PII data of Unit 9900 of IDF, Israeli PM and his son. Puts data on sale in one-on-one transaction, to oppose the Israeli forces deployment.
#geopolitics #databreach #sensitivedata

CartelCorp & Blacknet-00 alliance hits email server of Chiayi City, TW fire department. Sensitive data extracted and encrypted.
#ransomware #criticalinfrastructuresecurity #cyberattack

Threat actor claims to have breached the admission application portal of US Military Academy for the upcoming session of Explosive Ordinance Disposal, 2027. Claims have not been confirmed by US Army departments.
#databreach #cyberattack #usarmy

Threat actor claims to have compromised US Army email server, threatens to leak credentials and emails soon. The claim has not been verified yet.
#databreach #usarmy #cyberattack

Qilin ransomware publishes names of five new victim organizations, on it's blog. Proofs of ransom, encrypted data has not been shared yet.
#ransomware #cybersecurity

Jamco Aerospace which suffered a ransomware attack in Aug 2025, has it's data published by the threat actor. Approximately, 154 GB in 139 archived chunks.
#ransomware #aerospace #databreach

Threat actor selling 750 million records of ShunFeng Express, a Chinese quick commerce delivery and logistics company; that was attacked in 2020 as well.
#darkweb #cybersecurity #quickcommerce

Al Rasheed Co, a military supplier of Saudi Arabia was hit with a cyber attack by Ansarallah and Uways Qarani group. Claims of disarming and disabling the military hardware have been made. 9.5 GB of sensitive military data dumped.
#databreach #cybersecurity #military

Hackers rig refrigerators across France, by compromising Danfoss manufactured thermostats. Temperatures were raised to 50 degree Celsius that spoiled the food stored.
#otsecurity #cybersecurity

Threat actor allegedly compromises a popular payment gateway of MENA region, named Geidea, though data is not leaked but SQLi proof has been shared.
#cybersecurity #paymentgateway #vulnerability

Uttar Pradesh Metro Rail Corporation data has been put for sale if the organization fails to pay ransom of USD 15K by the threat actor.
#cybersecurity #criticalinfrastructureprotection #ransomware
