






Estonian email provider mail.ee was exploited to target a small number of email accounts according to The Estonian Internal Security Service.
Sounds like it was an XSS vulnerability that can be very powerful if wisely used.
kapo.ee/sites/default/files/…


Probably the first relevant post in Twitter when it comes to the POC of CVE-2019-0708.

CVE-2019-0708 remote scan tool by 360Vulcan team. Detect the recent RDP bug via RDP packet behavior, without trigger the final bug path(no BSOD or any side effect on the target system), ask for it to scan your network by sending mail to cert at 360.cn


Painottaisin tätä, jos meinaat lähettää tiedostoja Virustotaliin: "Yhteisön jäsenet voivat myös ladata itselleen Virustotaliin lähetettyjä tiedostoja tutkiakseen niitä tarkemmin." Lataaminen tosin vaatii maksullisen käyttäjätilin, toisin kuin artikkeli antaa ymmärtää.

Epäilyttääkö tiedoston tai nettisivun avaaminen? Näin voit testata maksuttomalla ohjelmalla, sisältävätkö ne viruksia ja muita haittaohjelmia hs.fi/teknologia/art-2000006…
@EsaMakinen Moi! Eroaako HS:n tilaajan ja ei-tilaajan näkemä mainostus mitenkään mobiilisovelluksessa? Esimerkiksi mainosten näyttötiheydessä tjms.
1


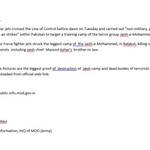
"Exclusive_Pictures_destruction_of_Jaish_Camp_and_dead_bodies_of_terrorists.doc", created today. MD5: 41b70737fa8dda75d5e95c82699c2e9b
Pings to 216.176.190[.]98:3386

1
1
Hieman huolestuttavaa, että pankin työntekijän sähköpostiin on pääsy suoraan internetistä ja oletettavasti ilman kaksivaiheista tunnistautumista. is.fi/digitoday/tietoturva/a… #phishing #aktia


Joku sankari grepannut "poliisi" vuosia vanhasta hetudumpista ja laittanut laudalle. Helposti tuli mediahuomiota 🤦♂️

Poliisien yksityisiä tietoja päätyi runsaasti pimeään verkkoon – levittäjä uhkaa julkaista lisää ja pyytää lunnaita. #poliisi #henkilötiedot #tietovuoto #kiristys #darknet #Suomi #Finland aamulehti.fi/a/201263555?c=1…
1
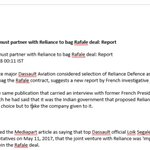
Dassault Rafale fighter jet related lure doc "rafale_art.docx" (dfad7d4a7ecb2eed6d69abfbfb5f94c9) by #SideWinder #APT group.

Leetmx, campaign targeting Latin America, seems to be still active.
File: Curriculum Vitae Actualizado Maria Elizabeth Hernandez Vasquez.doc
MD5: 516498ff378128770b006b681943c00c
Nicely obfuscated, downloads #remcos. Reuses the domains mentioned here: clearskysec.com/leetmx/

The article has interesting details how Maersk recovered from NotPetya attack. Worth to read.

NEW ISSUE: On June 27, 2017, a piece of malware called NotPetya infected computers across the globe. It crippled ports, paralyzed corporations, and froze government agencies. This is the untold story of the most devastating cyberattack in history wired.trib.al/i8kUrFT

"Predict what's next after Singapore summit" #SANNY #APT
File name: article.doc
MD5: 468f0d5e987430384e4e8220df2e8584
Pretty much the same stuff for the initial infection that is seen in FireEye's blog post: fireeye.com/blog/threat-rese…
ghostbin.com/paste/kv355
