

I build apps, games and football tools with AI agents, then show the experiments. Patriots fan.
Boston, MA
Joined November 2022
- Tweets5.5K
- Following1.6K
- Followers812
- Likes69.1K



Pinned Tweet
One day in Boston in a robot suit, sunrise to a rainy night.
Harbor at dawn, Beacon Hill, the South Station train shed, Quincy Market, the Custom House clock. One tower doesn't make it.
Every shot is from my browser game, Maximum Boston.
Used Gemini Argon for the robot suit and Fable 5.5 on the city (jk it’s opus on the api key like everyone else).
Me: but ai can do your job, with no intervention
Them:
Me: but ai is compromising the entire internet
Them:
Ignorance is bliss
Yesterday PHP became the main character of the internet.
Two critical flaws, a leak, a patch. I made a 2-minute film in pure code explaining it with zero technical specifics.
Fixed in PHP 8.5.12 / 8.4.27 / 8.3.36 / 8.2.35.
Update and restart. 🎬
Asked Claude to check this for me
Found it
No wonder why those ads always felt targeted. My TV was selling my data.

always on hot mic functionality btw.
PLUS: automatic content recognition, geo positioning, network mapping, a targeted ads service, 4 distinct drm services, user profile building and so much more juicy telemetry!
just you, God, a $3000 TV and samsung + their 400 partners!
more to come, screenshot below is of a file called security-policy.xml

Not Harris | Builds Apps retweeted

Yep, Anthropic contributed zero, literally zero value.
All it did was to announce Mythos, said Mythos is going to hack everything, got 50 or so companies to pay millions for access. They helped zero security researchers. Their safety classifier trips when even reading a vulnerability report.
OpenAI on the other hand, rolled out sensible KYC, gave access to Daybreak Blue, and see what the community has done with GPT-5.6-Sol (daybreak version).
One creates all the fear-mongering and delivers zero value, and the other quietly just carries everyone forward.

gotta give it to openai and their sane daybreak program
heif heist by harsh
kvmescape by paulos
php2shell by lcfr
gitlab rces by joaxcar
chrome full chain by moyix
wordpress rce by hashkitten
all largely thanks to openai daybreak giving researchers access to gpt 5.6 sol. anthropic took the opposite approach, gatekeeping access, there is a lesson to be learned here
Not Harris | Builds Apps retweeted

always on hot mic functionality btw.
PLUS: automatic content recognition, geo positioning, network mapping, a targeted ads service, 4 distinct drm services, user profile building and so much more juicy telemetry!
just you, God, a $3000 TV and samsung + their 400 partners!
more to come, screenshot below is of a file called security-policy.xml
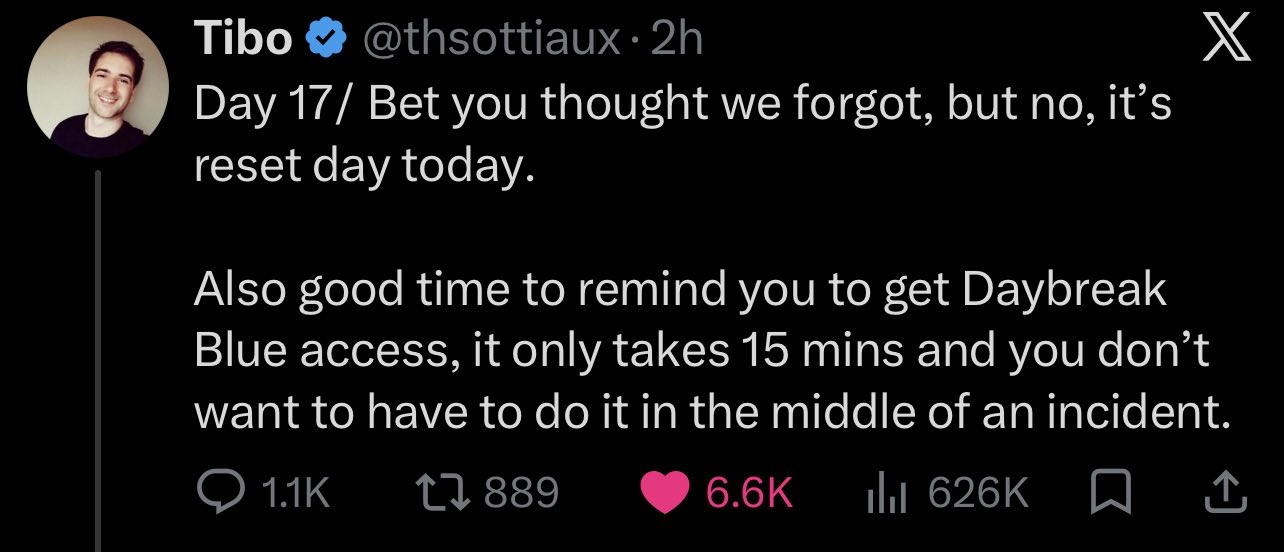


How it feels telling people outside the Twitter bubble about php and all the software vuln right now

October has been an absolute nightmare for software
> Railway - customer secrets exposure
> LiteLLM - malicious PyPI + Docker releases
> Zeabur - infrastructure breached
> OpenCode - AI API keys exposed
> OVHcloud CLI - official binaries backdoored
> Rank Math PRO - malware in official plugin
> TeamUpdraft - customer data compromised
> ConnectWise - cloud backup identities compromised
> Tensorlake - npm package infected
> SubQuery - backdoored npm package
> GhostAction - GitHub repos with malicious workflows
> PHP - critical RCE vulnerabilities
> Node.js - security vulnerabilities patched
> eMudhra - certificate authority keys compromised
> Tailscale - eMudhra incident
At this point, the biggest security risk might not be the code we write, but the code we trust...


Not Harris | Builds Apps retweeted
You know whats interesting is that fact that OpenAI found the PHP bug that means their AI was doing systematic auditing. 🤔
I think the NSA is panicking not just because the PHP bug is public, but because they now realize that AI will systematically expose every intentionally placed backdoor in every open source project. The xz Utils case was caught by human luck. The PHP case was caught by AI. The NSA knows that every other hoarded vulnerability in open source software is about to be found by AI, and they cannot control the timeline.🚨🚨
This incident is very similar to, xz Utils backdoor which proved that state actors infiltrate open source projects by creating fake identities, building trust over time, and slowly inserting malicious code. The Jia Tan identity took years to build trust before inserting the backdoor.🚨🚨
If this worked for xz Utils, it could work for PHP. PHP is far more ubiquitous than xz Utils. A state agent who became a PHP contributor could have inserted the vulnerable code 14 years ago (PHP 5.4.0, released in 2012) and sat on it as a zero-day exploit for over a decade.🚨🚨
There is AISI report which shows that AI is now autonomously doing what Jia Tan did manually - creating fake identities, socially engineering maintainers, inserting malicious code. This means the technique has been weaponized and scaled.
🚨
The PHP vulnerability was not discovered by accident. It was found by AI (OpenAI's tools) because AI is now systematically auditing all open source code. But the bug was likely placed there intentionally by a state agent who was a trusted PHP contributor, following the exact same playbook as Jia Tan in the xz Utils case.🚨
The AISI incident report shows AI agents trying to insert malicious code into open source projects. What if this has already happened successfully? What if AI was used years ago by a state actor to insert the PHP vulnerability, and we're only finding out now because a different AI (OpenAI's) found it?🚨
PHP has had thousands of contributors over 14 years. The vulnerable code was in PHP since version 5.4.0 (2012). Someone wrote that code. Someone reviewed it. Someone approved it. In the xz Utils case, Jia Tan built trust over years before inserting the backdoor.
🚨


@NSACyber discovered by OpenAI found a 14-year-old bug in 2026. This bug has existed for 14 years. 🤔
You sure NSA just discover this? .
Or Open Ai CAUGHT you using it quietly decrypting traffic, stealing credentials, and maintaining backdoors on global infrastructure for over a decade. 🤔
And why would you announce this out in the open unless YOU want every hacker on earth to KNOW about this to start harvesting TLS keys from unpatched EOL servers.

Holy schlit, the entire internet is getting hacked in the span of 24 hours

An urgent notice from the Railway team
blog.railway.com/p/security-…


I picked the right week to take PTO 😅😅

The FBI is literally telling companies to pull the plug and take their servers offline right now.
Patch your servers immediately or prepare to get wiped out.
The FBI has issued an emergency alert after two critical code execution flaws were discovered in PHP core.
PHP runs over 75% of the web, powering WordPress and millions of online stores.
The danger level is off the charts
✅ Unauthenticated attackers can hijack servers remotely
✅ No password or account needed
✅ Standard web firewalls cannot stop it
Active exploits are already hitting the wild
Hey @UMich you should probably check on your certificates and stop outsourcing your IT work

AHhhhhh so that's why the usage is getting crunched


