

Security engineer specializing in tokenization, RWAs, and smart contract development at @taurus_hq, CMTAT contributor (@cmta_ch)
Switzerland 🇨🇭
Joined June 2022
- Tweets1.1K
- Following4.5K
- Followers286
- Likes1.2K




AccessDenied403 retweeted

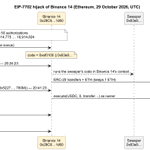
i decompiled the contract that drained binance wallet 14
gist.wavey.info/Ta3FgAxastgj…
AccessDenied403 retweeted

Why now? Smriti Verma (@OpenZeppelin) set out the institutional exposure problem and the tech landscape: FHE, ZK proofs and private state.
Ryan Sauge @ADCDIII (@taurus_hq ) presented CMTAT Confidential, an implementation of the CMTAT token standard for confidential securities, built on @zama.
Dominik Bepple (Seturion) showed confidential DvP in production: atomic settlement on public rails, with both the asset and cash legs encrypted in a single onchain transaction.
Jimmy Tahoulas (@Swissquote) looked at what a public ledger means for client privacy.
Pavel Jakovlev (@AMINABankGlobal) summed up what banks want: the regulator and counterparties see what they need, everyone else sees nothing.
AccessDenied403 retweeted
We are happy to officially welcome @Nethermind to the CMTA. Nethermind has already contributed to CMTA's work through the FIX-CMTAT connector and its pre-audit AuditAgent tool has been applied to CMTAT contracts.
Looking forward to advancing standards for tokenized capital markets together.

AccessDenied403 retweeted
SnapshotEngine v0.5.0 for CMTAT is out
On-chain snapshots for any ERC-20: capture balances and total supply at a record date to correctly determine dividends/interest/rights against a fixed ledger state.
→ schedule / reschedule / unschedule snapshots
→ poke() to materialize at the record date
→ external engine (RBAC or Ownable2Step) or integrated into the token
→ binds to any token exposing balanceOf + totalSupply
Open source, MPL-2.0. (Not audited: verify before production).
Specifications and repository 👇
github.com/CMTA/SnapshotEngi…
cmta.ch/content/fd9c5f6015e0…

AccessDenied403 retweeted

ERC8343: Contract deactivation
Interface for permanently deactivating a token contract and exposing its deactivation status
Author: @ADCDIII
github.com/ethereum/ERCs/pul…

AccessDenied403 retweeted

The Capital Markets and Technology Association (CMTA @cmta_ch) has launched CMTAT Confidential, powered by the Zama Protocol.
Developed by @taurus_hq based on @OpenZeppelin’s confidential smart contracts, CMTAT Confidential extends the CMTAT standard with confidentiality.

AccessDenied403 retweeted

We are pleased to announce that Halborn is now a member of CMTA! 🤝
@cmta_ch defines industry standards to facilitate the use of blockchain in the capital markets industry.
As a member, we will bring our cybersecurity and digital asset custody expertise to their standards work.

AccessDenied403 retweeted

the CMTAT security token standard (by @cmta_ch) now supports Confidential Token / @zama
github.com/CMTA/CMTAT-Confid…
code by @ADCDIII

AccessDenied403 retweeted

🚨 $crvUSD depeging again as borrow rates have exploded to 40%
crvUSD/USDC 0.985:
If bitcoin starts cascading here due to $MSTR crashing, crvUSD will depeg very hard as the pegkeepers are empty and the pools are very imbalanced.
There's only $2m of exit liquidity in each of the top crvUSD pools on Curve, so it won't take much to crush the crvUSD peg right now.
The ratio is 10:1 😬😱
If @yieldbasis LPs start to panic at some point and begin to withdraw their BTC, the downward pressure on the peg will increase substantially!!
Like I said many times before, CurveDAO was irresponsible to approve not only the initial 60m crvUSD credit line, but also the subsequent 300m credit line for YieldBasis without extensive real-world testing.
RIP $YB $CRV $CVX 🪦


UPDATE #2: Significant depeg on $crvUSD now as pegkeepers exhausted all their reserves ⚠️
crvUSD/USDT trading down to 0.95
crvUSD/USDC trading down to 0.96
Borrow rates have spiked to 30% lol
@yieldbasis is not good for crvUSD, only a matter of time before crvUSD/YieldBasis end up with a sizable chunk of bad debt!!
$YB $CRV $CVX

AccessDenied403 retweeted

Gmak, early this morning we received reports regarding an incident with the $DUSD Curve pool
At this stage, the issue appears to be isolated to DUSD LP positions on Curve. There is currently no indication that other assets or deployments are affected.
Underlying assets held in the Machines remain unaffected.
As a precaution, security mode has been activated across all Machines while we continue to assess the situation.
RECOMMENDED ACTION: We strongly advise LPs in the DUSD Curve pool to remove their liquidity.
Our immediate focus is to fully understand the scope and impact on the Curve pool and to determine the appropriate next steps for affected users and LPs.
Further updates will be shared as soon as the incident review is complete.
AccessDenied403 retweeted
🚨SlowMist: Analysis of Trust Wallet Browser Extension Hack🚨
Today, @TrustWallet issued a statement confirming that version 2.68 of the Trust Wallet browser extension contains a security risk. Below is our detailed breakdown:👇

We’ve identified a security incident affecting Trust Wallet Browser Extension version 2.68 only. Users with Browser Extension 2.68 should disable and upgrade to 2.69.
Please refer to the official Chrome Webstore link here: chrome.google.com/webstore/d…
Please note: Mobile-only users and all other browser extension versions are not impacted.
We understand how concerning this is and our team is actively working on the issue.
We’ll keep sharing updates as soon as possible.

AccessDenied403 retweeted

We’re proud to have contributed to the CMTAT Solana Specification, a practical reference for institutions looking to issue compliant security tokens on @solana.
👉 Full specification:
eu1.hubs.ly/H0qs4mr0
➡️ GitHub repository:
eu1.hubs.ly/H0qs5qB0
@cmta_ch


AccessDenied403 retweeted
The Capital Markets and Technology Association (CMTA), a leading organization developing standards for tokenized assets, has adopted the Chainlink interoperability standard.
cmta.ch/news-articles/cmta-r…
CMTA tokens are now natively transferable across the multi-chain economy.

AccessDenied403 retweeted

The path to tokenizing trillions in TradFi assets just got a lot clearer on Solana with CMTA's security token standard on Solana.
CMTA's token standard is the regulatory-compliant framework for tokenized securities in Europe (Swiss DLT Act + MiCA aligned).
Now it's native to Solana using already existing tooling including Token Extensions - no custom smart contracts needed. This means:
✅ Legal clarity for how to issue Swiss & MiCA aligned assets on Solana
✅ Leverages Solana's built in tooling so institutions can get up and running on Solana in minutes instead of months
Traditional finance has been waiting for compliant rails. CMTA on Solana delivers exactly that: institutional-grade securities infrastructure with Solana speed.

New: CMTAT Solana Spec v1.0.0
CMTA releases guide for deploying CMTAT-compliant security tokens on @Solana.
The spec details how the CMTAT framework for tokenizing financial securities can be implemented using Solana Token and Extensions Programs.
github.com/CMTA/CMTAT-Solana

AccessDenied403 retweeted
We're excited to announce the release of CMTAT v3.0.0, a major upgrade to the reference Solidity implementation of the CMTAT security token framework.
Code and full specs available in the CMTAT GitHub repo: github.com/CMTA/CMTAT


AccessDenied403 retweeted

Update: @Balancer and its forks are under attack, with total losses across multiple chains reaching ~$128.64M so far.


AccessDenied403 retweeted

Earlier today, @newgoldprotocol was exploited for $2M in a price manipulation incident.
The attacker swap the stolen token into the ETH using KyberSwap, bridged the stolen ETH to the Ethereum network using Across Protocol.
The attacker then laundered the stolen assets through Tornado Cash.
Attacker EOA on Ethereum:
etherscan.io/address/0x86183…
Attacker EOA on BNB Smart Chain:
bscscan.com/address/0x0305dd…
Attacker Contract Address:
bscscan.com/address/0x2d2a69…


AccessDenied403 retweeted
Request Finance incident report: Frontend was compromised to inject malicious approvals.
Full report: help.request.finance/en/arti…


🚨 A victim lost $3.047M USDC yesterday through a sophisticated attack involving a fake Request Finance contract on Safe wallet.
Key findings:
• Victim's 2/4 Safe multi-sig wallet shows batch transaction via Request Finance app interface
• Hidden within: approval to malicious contract 0x3Cf6e5...c03F mimicking legitimate 0x3cF638...C03f
• Both addresses share identical first/last characters
• Malicious contract was verified on Etherscan
Sources: @zachxbt, @evilcos, Safe wallet transaction history

