

חשבון הXוויטר של ערוץ הטלגרם הגדול בישראל לחדשות סייבר. https://nitter.gq/t.co/1cRObwsBla
Israel
Joined June 2021
- Tweets6.2K
- Following58
- Followers2.9K
- Likes2.4K



חדשות סייבר retweeted

הרבה אנשים עבדו ועמלו במבצע שאגת הארי איך נאמר תודה? לא, לא איזה בונוס כספי יא מצחיקולים. מה שמקבלים זו... תעודת הוקרה! כזו שחתומה ע״י קצין רם דרג.
אני לא עשיתי כלום חוץ מלקטר ולאכול את כל השוקולד בבית. אבל גם אני רציתי תעודת הוקרה. מה עושים? ובכן... הלכתי לכלי הפריצה:דפדפן. >>

RT @H4ckManac: 🚨 New #ransomware group: Vanir Group 🚨
Currently, the criminal group's list includes 3 victims:
Beowulfchain.com:…
חדשות סייבר retweeted

נראה כמו: אירוע סייבר חמור ב"טיפלתי"
t.me/CyberSecurityIL/4156
חדשות סייבר retweeted

Hi #infosec,
I noticed a group of my followers support HAMAS and their acts, commenting with smiles and laughter about babies being murdered in-front of their mothers. (Please bare with me)
Started blocking them, but how many are there in our global community?
I’M CALLING 🔈 all @BlackHatEvents, @defcon, @codeblue_jp, @brucon, @offensive_con, @MSFTBlueHat, @BSidesLV (and other confs) board members to prevent #HAMASISIS supporters from attending the conferences worldwide. 🇮🇱
FYI @cyb3rops @jaysonstreet @HackingDave @hasherezade @hackerfantastic @HackingLZ @msuiche @malwrhunterteam @malwareunicorn
חדשות סייבר retweeted
הסיפור של מעייני הישועה מתפתח, ולא בקטע טוב:
(קרדיט לארז דסה שתמיד עם יד על הדופק)

חדשות סייבר retweeted

ארז דסה מומחה סייבר מפרסם בטלגרם שלו כי קבוצת ההאקרים Ragnar Locker פרסמה באופן רשמי באתר ההדלפות שלה חלק מהמידע שגנבה במתקפה על ביה״ח מעייני הישועה, לאחר שבית החולים סרב לשלם את דמי הכופר.
הקבוצה טוענת ששיחררה חלק ראשון מהמידע שגנבה בנפח 402GB, ומאיימת לפרסם מידע נוסף בקרוב>
חדשות סייבר retweeted
מתקפת הסייבר במעייני הישועה: ארז דסה, בלוגר סייבר מפרסם היום כי יש לו מספר דיווחים לפיהם מתנהל שיח בין מעייני הישועה (או גורמים מטעמם) לקבוצת ההאקרים Ragnar. ולכן טרם פורסם מידע אישי על מטופלים.
להערכתו התוקפים יעדיפו להרוויח כסף מהמידע ולא לפרסם אותו, גם אם חלף הדדליין שהציבו
חדשות סייבר retweeted

🌐 I don't remember such a #ransomware blitz from the days of PYSA team 🚨
CLOP added 37 new victims, Huge organizations, Nasdaq companies, and financial companies most of them from the USA 🇺🇸
Is it related to GoAnywhere? 👀
malwarebytes.com/blog/news/2…
#CLOP

חדשות סייבר retweeted
🌐 The second interview with Ransom House #ransomware team by @CyberIL was added to our threat intelligence page 👀
➡️ DarkFeed.io
#RansomHouse

🌐In the interview of @CyberIL with Ransom House team, they talked about money laundering, favorite attack vectors, and the connections to other #ransomware groups 👀
"We've never had a relationship with Hive, so nothing changed after their shutdown"📢
interview on Intel Page

חדשות סייבר retweeted
🌐In the interview of @CyberIL with Ransom House team, they talked about money laundering, favorite attack vectors, and the connections to other #ransomware groups 👀
"We've never had a relationship with Hive, so nothing changed after their shutdown"📢
interview on Intel Page

חדשות סייבר retweeted

RansomeHouse's interview for @CyberIL exposes their hypocrisy. Hacking hospitals and causing harm to innocent people is not a moral crusade to improve cybersecurity. If they aim to make companies care more, why cause chaos? Let's call it what it is - a criminal act.
חדשות סייבר retweeted

הפריצה למחשבי הטכניון פגעה בהרבה חוקרים בתחום ה-ML והם עכשיו לא יכולים לאמן מודלים לקראת הגשות לכנסים מאוד חשובים שיש בקרוב. אני מנסה למצוא פתרונות לחוקרים האלה.
אם יש חברות שבא להן לפרגן בקצת כוח חישוב זה יהיה מדהים (גם אחלה דרך לגייס את הטופ טאלנט בתחום 😉)


חדשות סייבר retweeted
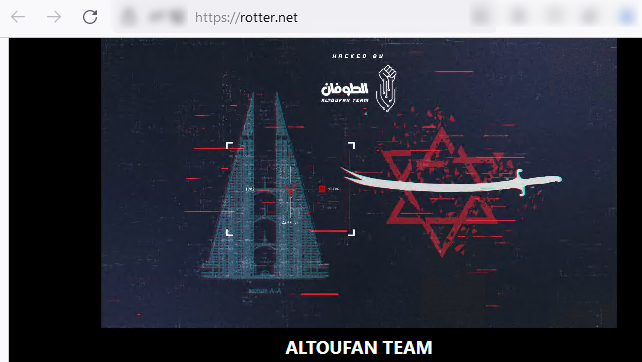
🇮🇱 Another #Cyberattack hit big Israeli target 🚨
RotterNet (@RotterNet) website was hacked and defaced by ALTOUFAN TEAM, Rotter is a large Israeli website for current affairs and politics
#ALTOUFANTEAM
חדשות סייבר retweeted

*הודעת עדכון*
לבית הטכניון שלום,
הטכניון נתון במתקפת סייבר מאתגרת. מדובר באירוע מורכב והחזרה לשגרה מלאה תארך זמן.

חדשות סייבר retweeted
🌐 Another ransom attack on an Israeli organization 🚨
Among the 5 victims that Lockbit #Ransomware team announced in the last hour there is another Israeli company 🇮🇱
It is very rare that there are two victims from Israel in one day and no Iranian threat actors involved 🤔

חדשות סייבר retweeted
🌐 There is a ransomware website inside a ransomware website? 😕
Vis Vendetta #Ransomware team website suddenly appeared on Cuba ransomware team domain
(test. ❓) 🤔
One victim from France 🇫🇷 on Vis Vendetta List
#VisVendetta #Cuba


חדשות סייבר retweeted

The Israel Institute of Technology was hit by ransomware this morning.
- DarkBit ransomware (???)
- Ransom note is political
- Attackers want $1,700,000+ (80 BTC)
- Ransom note is written using an English translator
Image courtesy of @CyberIL
