

Elephant tamer. Izzat spreader.
Agartha
Joined July 2025
- Tweets3K
- Following212
- Followers16.9K
- Likes14.5K
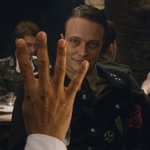




Vaguely alluding to the number 4 appears to be a form of bullying and racial discrimination now.
Frontier AI models are hamstrung by HR-tier policies.

Izzatologist retweeted

Immigration policy must be driven by the present, not the past, and business leaders are too terrified of the left AND the right to acknowledge this.
Recent H1B discourse revolves around a longstanding immigration sleight-of-hand. H1B proponents point to exceptional people who came here decades ago as if they represent the current state of the program in the same way that advocates for low-skill/illegal immigration point to very favorable immigrant crime/welfare/education/etc statistics that do, in truth, have them beating native-born Americans on many fronts.
It is all a sham. The world that created those statistics, people, and businesses no longer exists. Brilliant but desperate Vietnamese fathers who fled communism have nothing in common with young men from Honduras, and the crime rates/economic acccomplishments/integration of the former should not be used to justify mass migration of the latter.
Nor should the accomplishments of people who managed to get an H1B visa in the 90s (when the program was capped to just 65,000 visas) be used to justify staffing agencies and tech companies using the program to replace American jobs for less money. The obvious abuse going on is politically suicidal and something that even the most ardent supporters of the visa should want to crack down on, no immigration program can possibly survive the obvious and widely known reality of what is going on. I am a longtime outspoken advocate for stealing the best people from other countries to make our own better, runaway abuse of existing programs robs the government of the worker trust required to do so.
Lots of people in the tech space know this. Even the dumb people are smart enough to see it. Nobody actually believes these are all incredible people with unique talents performing jobs no American can. Everyone knows the guy in Cubicle Bay 7 doing mediocre but functional web design for half the salary of his American peers is no savant and doesn't meet the statutory requirements for his H-1B visa.
Unfortunately, most people with power or profile are terrified that any public statement or acknowledgement will get them attacked by the right (You guys have been screwing over American workers for years with visa abuse, you damn hypocrite!) or the left (You are racist, sexist, misogynist, and sucking up to this fascist administration!). Or, more likely, both. I know too many tech execs in particular who feel trapped, like the only winning move is to stay silent.
JD is blowing the whole thing wide open by putting facts and stats front and center that nobody wants to engage with. Critics will talk about anything and everything else but these damning facts and this obvious truth, that H1B visas serve neither their original purpose, legal purpose, invented purpose, or the American people.

Vice President JD Vance breaks down the data:
"If you are working as an H-1B visa in the United States of America, you’re earning $20,000 less than an American citizen hired in the same position. If you were brought in by one of these foreign outsourcing firms, you’re making $48,000 less than an American citizen in a similar position. So I’m sure that everybody here understands the game that is being played. You bring in indentured servants from outside the country, you lay off American workers and, if you’re a corporation, you make a ton of money by under cutting the wages of American workers, replacing them with people who frankly shouldn’t be in the United States of America to begin with."
Indian incompetence is so bad that we’ve now immortalized and weaponized it into tools designed to hack into insecure technology.


I have a theory…


wow this is bad!
ENTIRETY of PingCap database used by linkedin, flipkart, airbnb etc. has been copied and stolen due to customer credentials being stored directly in support tickets (LOL)
Attackers ran exfiltration directly on their cloud (LOL) pipeline ran for 22 days, exfiltrating data every 6 hours and NO ONE noticed. Worse, PingCap denies all of it.
Average SRE salary is $300,000 at PingCap btw

At 7 AM this morning I received an email that my VPS at Ultahost would go offline for "scheduled maintenance" (this is the first notice I ever received) for what I assume is related to the PHP incident. This was described as a "brief downtime of approximately 30 minutes." Less than 3 hours later my VPS was offline. Over 12 hours later my VPS was still offline.
I contacted support and was told the maintenance is still ongoing and they are not sure if it will even be complete by tomorrow. I have zero notifications about this except for the initial email 3 hours before they shut off my services.
Heads up if you ever considered this provider. I am actively searching for a new hosting provider.

Bro stopped replying but like a sleeper cell he was reactivated to defend his jeet brethren during a large scale izzat loss event.


More private keys by the Indian certificate authority have been discovered. These are all small numbers.
People are suspecting that they interpreted 384 bit keys to mean that they should pick numbers from 1-384 to use as their private keys.


The rules are simply different in India. You will never see a video of the key ceremony nor the third party security audit. In India a family business can be a CA and entrusted with upholding the security of the internet without any meaningful standards whatsoever.


Jeets are regularly forced to admit they fucked up, causing massive izzat losses.
To mitigate, they spin their disasters to sound less damning, like being able to spoof the internet with the fucking number 4.
This prevents izzat bankruptcy and gives an illusion of improvement.


Izzatologist retweeted
It can't be overstated: a random, literal-who Indian company just utterly broke security across a swathe of technology.
It's going to be the Wild West for a lot of stuff until it's fully patched. There will be things never patched.

Izzatologist retweeted

Vivek is a distilled caricature of an entitled, arrogant, scamming Indian.
The way he flicked his hand at the man confronting him for featuring a felon in his recent ad was telling.
Which he followed up with attacking Acton via her estranged and allegedly abusive mother.
Vivek, an anchor-baby handed everything in life for being brown, from his citizenship to his DEI scholarships, and his fraudulent companies, is attacking an American woman with a troubled childhood who against all odds managed to become a doctor.
An actual American success story of studying and hard work vs a “new American” scammer. The contrast could not be more stark. What an incredible piece of history to watch unfold in front of us.
Jeet airs an estranged mother, who allowed the sexual abuse of her daughter, expecting you to vote for him instead. Absolutely sick people.

Ramaswamy took credit for the anti-Acton video after his central OH event today.
"It is an ad from our campaign, and the thing that I want to say is that I would love for this race and this election to be about the substantive issues that impact Ohioans, and unfortunately, Amy Acton has been hiding from those issues."
abcnews.com/Politics/amy-act…


If you are still running PHP in 2026 you absolutely deserve this.

Full details of a remotely exploitable vulnerability in the core engine of *all* PHP versions will be released tomorrow, October 21st. If your organization has internet facing PHP applications then you need to be ready to patch the minute the update is released or *strongly* consider taking the application offline until you can:
php.net/index.php#2026-10-20…

This would truly mind boggling to anyone who understands security, except for the fact that it was an Indian company.
We are talking about a private key for a certificate authority that could be brute-forced in less than half a second.
Indian incompetency is boundless.


A brief explanation to help understand the severity of something this retarded.
HTTPS certificates can be generated by anyone, but a trusted authority uses a secret key when generating these.
Since their secret key is literally 4, anyone can issue trusted certs on their behalf.
Consider if I ran a phishing website for your bank. You could check in the URL to determine it was a scam. Now you cannot trust even that anymore on devices that have not been updated. I could run a public WiFi and phish anyone who uses it without detection.