

#bitcoin, hashing, hardware, user control, ☢️. Your keys, your coins; my words, my views. npub1wec4sj8tymnkag3gfr0zuufm3xmr857txhhfkkhm697lqkrstnyqe35kq7
lost between blocks
Joined September 2020
- Tweets3.9K
- Following785
- Followers944
- Likes19.8K




Jay 'pro Sv2, anti-fpps' Beddict🧹(ctv+csfs) retweeted

4 critical security issues in 24 hours
gitlab: citadelwire.com/posts/2026-1…
node js: citadelwire.com/posts/2026-1…
php: citadelwire.com/posts/2026-1…
insecure ca keys: citadelwire.com/posts/2026-1…
wire will continue to monitor the situation: citadelwire.com

Jay 'pro Sv2, anti-fpps' Beddict🧹(ctv+csfs) retweeted

Every old device you own, if it's no longer receiving updates, is now about as secure as a Dior bag in a Paris riot.
Update everything, EVERYTHING, and if it can't or won't update, shut it down.
That old dusty Linux box that's been your memes and music archive for fifteen years? Yeah, that too.
This is the kind of vulnerability that you clean out your tech hoard for. Anything that can connect to the Internet but hasn't had updates since Obama was in office? It all must go, fire sale, now now now.
If you have any device in your kitchen that has the word "smart" in it, if your TV hails from a time when OLEDs were novel tech, if your meat thermometer has an app, it's time to have you a real honest think about the security of your home network.
I always knew IoT was a bad idea.


Jay 'pro Sv2, anti-fpps' Beddict🧹(ctv+csfs) retweeted

eMudhra CVE checklist
Ubuntu: sudo apt update && sudo apt upgrade
Apple: settings -> general -> software update
Windows: power off -> throw it out, switch to Linux


Jay 'pro Sv2, anti-fpps' Beddict🧹(ctv+csfs) retweeted

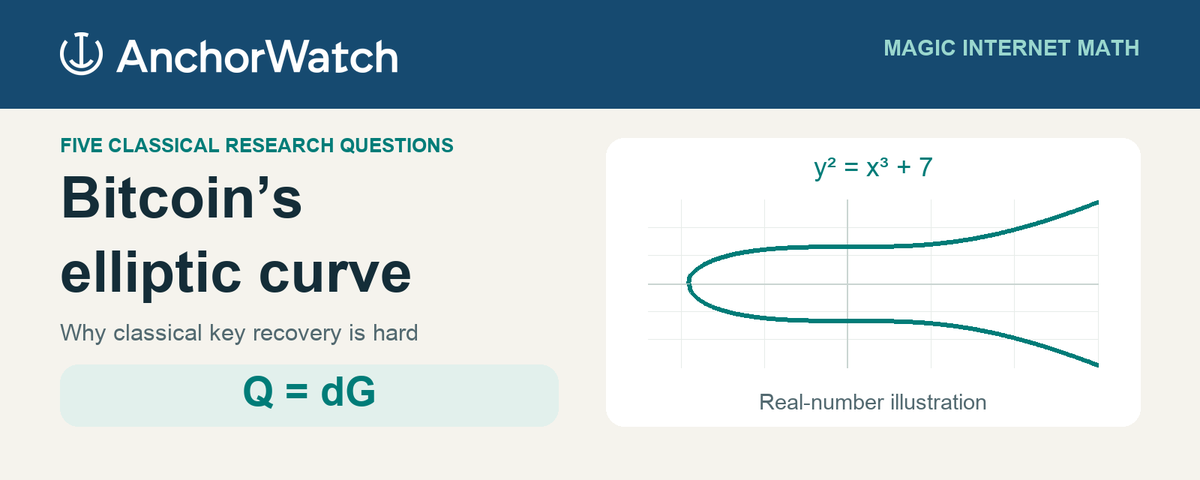
Since Math is in the news this week as it relates to Bitcoin, I sat down with @Fundamentals21m to do an episode of Magic Internet Math.
Today we Red Teamed Elliptic Curve Cryptography and discussed how math COULD break Bitcoin. In short, its very hard.
Jay 'pro Sv2, anti-fpps' Beddict🧹(ctv+csfs) retweeted

Update Telegram Desktop immediately!
A critical vulnerability has been discovered that allows attackers to gain access to your account and secretly steal files from your computer.
The attack uses links in the format tg://. If a special command is constructed, clicking the link can cause a malicious script to send a selected file to the attacker’s channel - without requiring additional confirmation.

Jay 'pro Sv2, anti-fpps' Beddict🧹(ctv+csfs) retweeted
🚨SUPPLY CHAIN ATTACK SUSPECTED 🚨
The blast radius could be larger than ledger, It you bought a device through this reseller move your assets immediately.


Jay 'pro Sv2, anti-fpps' Beddict🧹(ctv+csfs) retweeted
Timeline: “frontier AI models may break cryptography, oh no!”
Me:
Jay 'pro Sv2, anti-fpps' Beddict🧹(ctv+csfs) retweeted

Digitization and AI have erased the costs that once protected our privacy. A new generation of cryptography is bringing them back.
Peer-to-Peer's first guest post. From @GoBankYourself p2p.coincenter.org/p/enginee…

Jay 'pro Sv2, anti-fpps' Beddict🧹(ctv+csfs) retweeted

At long last, we have given Claude a wet lab, as in the classic sci-fi novel Don't Give Claude a Wet Lab.

Jay 'pro Sv2, anti-fpps' Beddict🧹(ctv+csfs) retweeted

We’re so terrified of AI derived bio threats that we are quietly giving our AI control of a wet lab in the middle of a major metro area
What the fuck man

Jay 'pro Sv2, anti-fpps' Beddict🧹(ctv+csfs) retweeted

JENSEN HUANG: “If you build a product or a service and you're not confident in its functionality, capability, or safety, then don't release it … The market forces are already there. We don't need any new laws. We don't need new regulations.”
Jay 'pro Sv2, anti-fpps' Beddict🧹(ctv+csfs) retweeted

Engineers spent decades shrinking semiconductor process nodes from around 1,000nm to today’s 2nm class so you could carry absurd amounts of computing power in your pocket.
Software developers responded with megabytes of JavaScript, telemetry trackers, six frameworks, and a loading animation for the login page.
Hardware gives. Software takes away.


Jay 'pro Sv2, anti-fpps' Beddict🧹(ctv+csfs) retweeted
Why do we spend all this time theorizing about how AI could harm us when we have endless examples in history of humans w/ centralized power doing immense harm. That's your danger. That's your xrisk.
Jay 'pro Sv2, anti-fpps' Beddict🧹(ctv+csfs) retweeted

They want to scare everyone so open source gets banned and they can have better margins while keeping you "safe"
It's an insidious tactic for them to secure more control, and in reality this resulting overconcentration of power is the real risk that has a historical precedent for abuse

Jay 'pro Sv2, anti-fpps' Beddict🧹(ctv+csfs) retweeted

If you’re concerned about the 153M drivers licenses in the IDScan leak, this is what you should do now!
Assume you’re in it, but you likely have more important vulnerabilities to address.
The reality is that your info is probably much easier to access right now through a quick Google search and leaky apps than any leaked data on the dark web.
If you google your own address and easily find it associated with your name, phone, and family members then everyone else can too.
Address this problem first.
Enroll in a PII removal service to get your info off data broker sites and then routinely search for your data.
Next thing: the apps on your phone and other platforms you’re signed up for are likely broadcasting all kinds of other more sensitive data about locations you frequent, where your kids go to school and who has access to your house.
This IS in your control and you need to lock it down.
Conduct an audit of privacy settings on your apps to ensure your entire life isn’t publicly accessible.
If you do these two things today, you and your family will be safer.
The leak is huge and you might be in it, but right now you need to focus on what you can control to make yourself more secure.

153,000,000 American driver licenses leaked in KYC hack
This is 63% of all American driver licenses
In US driver licenses function as valid government-issues photo IDs
krebsonsecurity.com/2026/09/…

Jay 'pro Sv2, anti-fpps' Beddict🧹(ctv+csfs) retweeted
👀🚨 AXON is accessing images of DRIVER'S LICENSES and IDENTITY DOCUMENTS through ACEIP without the consent of the individuals depicted, and using those photographs to train AI models
Government -issued identity documents containing:
• Full legal names
• Dates of birth
• Addresses
• Driver's license numbers
• Photographs (biometric identifiers)
• State of issuance
—-
Not only this 👀🚨
Axon's ACEIP program is a data harvesting operation that uses the monopoly power established through the Vievu acquisition to compel police departments into sharing citizen surveillance data for commercial AI development.🚨👀
1. Axon acquired Vievu in 2018, consolidating the (body camera market)
2. The FTC challenged this as anticompetitive
3. After the FTC case was dismissed, Axon used its dominant market position to implement ACEIP
4. ACEIP gives Axon access to Customer Content - including ALPR images, body camera footage, transcripts, and identity documents
5. Police departments cannot realistically refuse to participate in ACEIP because Axon is the dominant provider of body camera systems
6. Axon uses this data to train proprietary AI models
7. The AI models become Axon's exclusive commercial property
8. The citizens whose data feeds the models never consented
——
Axon's ACEIP portal confirms they access 🚨🚨👀
Detect Error Cases of ALPR and SOR" - active since February 2026. It says Axon accesses "ALPR data entries from customer database, which contains: (1) images captured by Fleet / Outpost camera, (2) ALPR read result and metrics, (3) user-correction, and (4) state level location of the reads."⬅️
"State level location of the reads" - 👀🚨
this means Axon is accessing the state-level geographic location of every ALPR read. Not just the time and date, but the state-level location. This means Axon knows which state each ALPR read came from.⬅️⬅️👀
Now connect this to the "Automatic License Plate Recognition (ALPR) System Improvement" use case, active since October 2022: "License plate images captured by a users Fleet Camera and the associated ALPR Read Record such as date and time of the capture, and geographical location."
"Geographical location" - not just state-level, but precise geographical location.
So Axon has been accessing:👀🚨
1. License plate images
2. Date and time of capture
3. Geographical location of capture
4. ALPR read results and metrics
5. User corrections
From every participating police department since October 2022. That is nearly 4 years of continuous access to license plate images and location data from police departments across the country.
axon.com/aceip-law-enfo…
ftc.gov/legal-library/
@RepThomasMassie


Jay 'pro Sv2, anti-fpps' Beddict🧹(ctv+csfs) retweeted

ID verification strikes again! 2 days ago 153M driver licenses in US+CA leaked and are now up for sale on a Russian cybercrime forum.
When you give a company your personal information (eventually) it will leak.
krebsonsecurity.com/2026/09/…