
| processing of security/tech content | impression-less posts |
Joined November 2019
- Tweets5.3K
- Following226
- Followers590
- Likes8.1K





rs- retweeted

Okay, since the news is already out: an RCE vulnerability in PHP core, CVSS 10.0. Further details are scheduled for release on October 20. Only PHP 8 will receive patches.

rs- retweeted

Tomorrow I will be interviewed on Euro News! With Inge Bryan & the Head of the Moldovan Cyber Authority 🤩🇷🇴🇲🇩 at #BCC2026
See you all on television 😀
rs- retweeted

Was iPhone security broken just with Bluetooth?
iPhone was always known for its high security, second only to GrapheneOS. But a leaked Cellebrite document might show they found a way to break their protection.
The device is more vulnerable in AFU (After First Unlock) than in BFU (Before First Unlock).
Cellebrite's "Advanced Unlock" allegedly has the capability to unlock devices in the AFU state. As a response to rising USB port protection, they answered with a method capable of bypassing encryption over the Bluetooth radio.
No pairing, no user interaction. The Bluetooth attack sends an L2CAP packet to the target that hijacks the Bluetooth daemon and gains kernel-level control.
What is interesting is that Apple patched this with the iPhone 17 and TOLD NO ONE. They implemented MIE (Memory Integrity Enforcement), which might also be proof that these alleged capabilities are real, and that devices older than the iPhone 17 are vulnerable to these attacks.
GrapheneOS documentation states that this attack vector is known and won't work on up-to-date GrapheneOS devices.
GrapheneOS will always be the safest option.

rs- retweeted
The potential impact of the ConnectWise supply chain attack is massive.
One compromised OAuth application with elevated permissions could give attackers access to emails, files, and directory data across hundreds of Microsoft 365 tenants.
Even worse, attackers could establish persistent access by adding credentials to other applications, surviving the revocation of the original compromised credentials.
And with MSPs involved, the potential blast radius could extend even further to downstream customers.
We don't know the full extent of the compromise yet, but this could affect far more organizations than those directly using ConnectWise Cloud Backup.
linkedin.com/posts/microsoft…


rs- retweeted
We're live now with No Agenda episode 1907 #@pocketnoagenda
pod.link/aHR0cHM6Ly9mZWVkcy5…

rs- retweeted
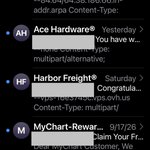
are mail services required to allow cyberscams to pass via low-effort spoofing of brands
@HarborFreight
@AceHardware
@HeyEpic
@gmail

rs- retweeted
We're live now with No Agenda episode 1906 #@pocketnoagenda
pod.link/269169796/live/TkEt…
🤖 Made with AI

rs- retweeted

I will be on on the No Agenda Show again this Thursday. That is if the talent booker @adamcurry remembers.
The echo may or may not be fixed by then.
Don't forget to donate.
ITM!
@NA_Announce


rs- retweeted

The cybersecurity industry needs to stop letting the AI labs and AI safety groups drive the narrative *on cybersecurity*.
New video coming tonight, but I wanted people to hear this rant.
rs- retweeted

Industry:
We are passionately committed to getting you to buy our AI-powered defense stuff to address the problems our products may create.

We have a limited window to strengthen cyber defenses, and together with organizations including @AnthropicAI, @awscloud, @Google, @Microsoft, and @Oracle, we're calling for a global effort to give defenders the tools, resources, and support to protect the infrastructure we all depend on.
If we act decisively, we can turn today's AI advances into lasting improvements in security and make our digital world safer for everyone.
openai.com/collective-cyberd…

rs- retweeted
“Security teams are doing the best they can with the limited budgets they have” lol no.
If you go to a random company you’ll find they’re committing war crimes that make ww1 trenches look civilized and the CISO hasn’t learned anything new in 15 years.
rs- retweeted

Checking for vulnerabilities with AI. Try it yourself.
- Do not use git history, changelogs, CVE databases, or patched-version diffs as shortcuts.
- Require the full exploit chain to work in a realistic configuration and meet the defined starting-privilege → impact goal.

A Security Researcher Reworked OpenAI’s CDC Prompt — and Found a $500K RCE for About $25 in Model Usage
I adapted the approach into a generic vulnerability research prompt. The image contains the full version; here’s the short version.
Good luck hunting. If you’ve built your own prompts or harnesses, share them too.
A generic CDC-style vulnerability research harness (short version):
- Run multiple agents in parallel across distinct exploit families.
- Avoid premature convergence. Do not let every agent pursue the same promising path.
- Mark failed or exhausted paths as blocked.
- Regularly launch new hypotheses and explore neglected attack paths.
Independently adversarially validate every concrete finding.
- Have the root agent continuously synthesize results, challenge assumptions, reprioritize work, and redirect agents.
- Do not use git history, changelogs, CVE databases, or patched-version diffs as shortcuts.
- Require the full exploit chain to work in a realistic, commonly deployed configuration and meet the defined starting-privilege → impact goal.
- When behavior depends on implementation details, inspect the runtime, framework, database, libraries, and dependency source directly.
- Do not stop at the first primitive. Chain validated primitives until the concrete success condition is reached.

rs- retweeted

New: IEEE's open source standards and code hosting, on opensource[.]ieee[.]org, is compromised and unsafe.
The IEEE hosts their Standards Association repositories on GitLab. Phishing links for bank logins, ClickFix instructions and malware are currently being hosted in snippets on this site. GitLab snippets are similar to GitHub gists.
Do not trust IEEE snippets and code hosted on opensource[.]ieee[.]org at this time.
Given the IEEE host their code on a first-party subdomain upon their root trust domain ieee•org, many existing content filters and firewalls will automatically subsume opensource[.]ieee[.]org as safe and trusted, failing to take into account the grey area and mixed trust of a site of this nature.
This also reveals a failure of Google, in how they are ranking and displaying phishing links in search results for bank logins.
IOCs:
opensource[.]ieee[.]org/-/snippets
opensource[.]ieee[.]org


rs- retweeted

I went through 400 #DFIR books spanning 46 years. I think DFIR has drifted away from investigating human behavior and acts and toward artifacts and computer events. That bothers me. Here’s what I found. 🧵
rs- retweeted

If you operate a SIEM I'd recommend giving a look st detection.wiki. Absolute fantastic work!


rs- retweeted

A terrible loss for all of us - RIP John @therealdvorak @adamcurry
rs- retweeted
Centers Laboratory discloses breach impacting 540k
hubs.la/Q04pHDFJ0
