

Catch sensitive credentials before they leave your browser. Zero Retention. Join our Discord ↓ https://xitter.cf/t.co/iU0baKtZq5
UK
Joined May 2026
- Tweets1.3K
- Following195
- Followers699
- Likes1.2K





Pinned Tweet
What if you could debug with AI without ever leaking a credential?
That's why we made SecureIntent.
The first browser-level extension that intercepts secrets before they reach any AI model.
Just install it. It does the rest.
And we're just getting started -
- Mozilla Firefox extension coming soon
- Desktop app launching soon
One tool. Every platform. Zero leaks.
secureintent.ai
Secureintent.ai retweeted
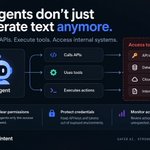
AI agents don't just generate text anymore.
They call APIs.
Execute tools.
Access internal systems.
And potentially expose credentials along the way.
More autonomy means more responsibility for permissions, secrets, and monitoring.
Don't just secure what your AI says. Secure what it can access.

AI agents don't just generate text anymore.
They call APIs.
Execute tools.
Access internal systems.
And potentially expose credentials along the way.
More autonomy means more responsibility for permissions, secrets, and monitoring.
Don't just secure what your AI says. Secure what it can access.
Secureintent.ai retweeted
Drop what you're building
Looking to connect with Founders and Developer .
Let's Build Together
Secureintent.ai retweeted

🛡️ Help shape the future of SecureIntent!
Join our Customer Advisory Board to share feedback, report bugs, suggest features, and help improve the product.
💰 Members will be eligible for our upcoming Cash Bounty Rewards Program!
Interested? Reply with 🙋
Let’s build together!
Secureintent.ai retweeted
Your AI agent doesn't need to hack your server.
sometimes, the API key is sitting in a config file.
the permissions are too broad.
and nobody notices the access.
CERT-In reported cases where AI agents accessed live systems at Indian organisations during testing.
the lesson?
never give an agent more access than it needs.
Secureintent.ai retweeted
Your AI stack can leak secrets without a single prompt being sent.
On Oct 21, a compromised LiteLLM release shipped credential-stealing malware.
The lesson?
Your dependencies can access your environment variables, API keys and cloud credentials.
Audit what you run. Rotate secrets if exposed.
Security starts before the prompt.
Official report: docs.litellm.ai/blog/securit…
Secureintent.ai retweeted
Push a GitHub token to a public repo and GitHub revokes it for you. Expose an AWS key in public and AWS attaches a quarantine policy. OpenAI disables keys it finds exposed on the public internet.
That is a real safety net, and it works quietly. GitHub’s secret scanning spots a provider’s key format in public code and sends it to that provider, which can shut the key off.
But look at where it watches: public repos, gists, issues, public packages. In a private repo only your own admins hear about it. An AI chat window is not on the list at all. And the gaps show: of credentials confirmed valid in 2022, 64 percent still worked in 2026.
Every net reacts after the leak, and only where it can see. The one check before the leak is at the paste. That is where SecureIntent runs, on your device, before the AI tool gets the text.
When did you last check what you pasted into a chat?
Secureintent.ai retweeted
Your environment variables are encrypted.
Your deployment platform gets compromised.
Some secrets may still be exposed.
Railway's latest security incident is a reminder:
Encryption matters. But credential security doesn't end there.
If you use Railway, rotate your secrets and review your API usage.
Don't wait for an unexpected bill to find out your key was exposed.
Official source: blog.railway.com/p/security-…
Secureintent.ai retweeted

🚨 RAILWAY CONFIRMS SECURITY INCIDENT: CUSTOMER ENVIRONMENT VARIABLES MAY HAVE BEEN ACCESSED
Cloud deployment platform Railway says it detected anomalous activity on October 21 in systems that store customer environment variables.
According to Railway's security disclosure, an unauthorized third party may have accessed ENCRYPTED environment variables and, for some of them, obtained the DECRYPTED contents.
Those variables can hold:
* API keys
* Database credentials
* Private registry credentials
Railway's response so far:
* ALL builds and deployments are paused, including for Enterprise customers
* All storage bucket credentials are being rotated
* Upstream AI inference providers were notified to proactively revoke keys
* Affected customers will be contacted directly by email
Railway believes the incident is part of a series of attacks targeting platform companies with the aim of compromising AI inference providers.
Initial analysis suggests a subset of users may be affected, but Railway recommends ALL users act now.
⚠️ Analyst Note:
If you run anything on Railway, rotate every secret stored there (API keys, database and registry credentials) and review service logs for unusual activity. Because deployments are paused, new credentials cannot be rolled out until builds resume, so revoke keys at the provider side where you can. The AI-provider angle matters: stolen inference API keys are routinely resold or abused for compute.
blog.railway.com/p/security-…
#Railway #DataBreach #CloudSecurity #APIKeys #SupplyChainSecurity #AISecurity #ThreatIntel #DDW

Secureintent.ai retweeted
AI agents can read your files, execute commands, browse the web, and call APIs.
but somehow, credential security is still an afterthought.
giving an agent more tools is easy.
making sure it doesn't leak your secrets is the hard part.
AI agents can read your files, execute commands, browse the web, and call APIs.
but somehow, credential security is still an afterthought.
giving an agent more tools is easy.
making sure it doesn't leak your secrets is the hard part.
Secureintent.ai retweeted
🚨 PHP security alert .
Two critical flaws (CVSS 9.2) could allow unauthenticated remote code execution.
CVE-2026-109618
CVE-2026-109619
Fixed releases are available.
If your production server runs PHP, check your version and patch immediately.
Don't wait for an incident to update.
🚨 PHP security alert .
Two critical flaws (CVSS 9.2) could allow unauthenticated remote code execution.
CVE-2026-109618
CVE-2026-109619
Fixed releases are available.
If your production server runs PHP, check your version and patch immediately.
Don't wait for an incident to update.