

Hey @bytecodevm (eleven red pandas 🐼🐼🐼🐼🐼🐼🐼🐼🐼🐼🐼), got any spicy bytecode / VM / language implementation / JIT / music
Bagnes, Switzerland
Joined November 2010
- Tweets46K
- Following841
- Followers2K
- Likes39.5K




eleven red pandas retweeted
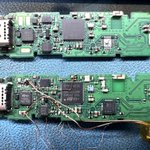
Pushing Bluetooth out to 12 Kilometers ift.tt/fNbw2BF

eleven red pandas retweeted

Unthemidator - a fully autonomous Themida / Code Virtualizer / Win License unpacker. Supports Themida/CV/WL v3.0 - v3.2.6.0 (latest), and CV v4.0. Unthemidator unpacks binaries, recovers imports, finds original entry point and unpacks compressed virtual machines too:
github.com/x86rc/unthemidato…

eleven red pandas retweeted

It is becoming f*cking dangerous: the NSA's own reverse-engineering tool now plugs straight into Claude Code - Ghidra has 94k stars, and GhidraMCP lets your agent read a compiled program instead of guessing what it does
Install Ghidra 12.1.4 from ghidra-sre,org (free, released by the NSA)
Download the GhidraMCP release and add it in File -> Install Extensions
Restart Ghidra and switch on GhidraMCPPlugin in File -> Configure -> Developer
Connect it: claude mcp add ghidra -- uvx --from git+github.com/LaurieWired/Ghidr… ghidra-mcp
Open a binary you're allowed to analyze and let Ghidra run its analysis
Ask Claude what a function does: it decompiles it, renames the variables and explains it in plain English
Ask for the map: every function, import, string and cross-reference, and where the interesting code lives
The decompiling runs in Ghidra on your machine, Claude just drives it
Malware samples, old firmware, your own builds: your agent reads the program itself, not the docs about it
Find the repo in the reply below

eleven red pandas retweeted

好家伙,开盒工具这回真落地了,名字叫 ALIENS EYE。
输入一个用户名,它几秒钟就把 840+ 个平台全趟一遍,谁在哪儿注册过账号,基本藏不住。
几个点提一下:
1️⃣ 异步扫描,快得离谱
2️⃣ 带 Tor 和代理,查的时候能遮住自己的来路
3️⃣ 结果可导出 JSON、CSV、HTML、Markdown,做 OSINT 和安全研究挺顺手
丑话先说在前头:能力越强越得守规矩,只碰自己有权限或拿到授权的目标,别拿去开盒骚扰旁人,违法的事一根手指头都别沾。
🔗 github.com/arxhr007/Aliens_e…

eleven red pandas retweeted

卧槽,3090要可能要涨价了!!
因为老黄的刀法被人破解了
有人给3090解了个锁,同样限制在 360W,PyTorch 测试从 75 TFLOPS 跑到了 135 TFLOPS,提升约 80%!
你以为是超频,把功耗往上拉?
但他改的是显卡里控制运算速度的寄存器,这些寄存器平时有权限保护,正常改不了
他利用 GPU 启动固件的漏洞,赶在 NVIDIA 驱动加载之前拿到写入权限,把相关运算改成全速,再交给原版驱动使用
解开的主要是 FP16/BF16 输入、FP32 累加这类 AI 运算的速度限制 但测试算力多了 80%!!
4090 也有分支项目做到了:同类运算的指令吞吐,从约 165 TFLOPS 提升到 331 TFLOPS,接近翻倍
项目地址,附上👇
github.com/Zagitta/gpu-unloc…

eleven red pandas retweeted
Every Mac on macOS 27 now has a free LLM built into the Terminal.
No account. No API key. No internet. No token bill.
Setup (1 minute):
1. sudo fm license (enter your Mac password, one time)
2. fm available (checks the model is downloaded)
3. fm respond “your question”
Works on any Apple Silicon Mac, M1 included.
- Pipe files: cat notes.txt | fm respond -i “summarize this”
- Get JSON back: build a schema with fm schema object, pass it with --schema
- Local API: fm serve gives you an OpenAI-compatible endpoint on localhost
- Resume chats: sessions save to ~/.fm/sessions/
The limit is 4,096 tokens per session, and your prompt, instructions, and the answer all share it.
So skip code and math. Use it for summarizing, extracting, classifying, and rewriting.
Free, private, offline, and already on your Mac.


eleven red pandas retweeted

🚨 Critical Okta Access Gateway flaw allows administrators to execute system commands; CVE-2026-115547
The vulnerability affects the Okta Access Gateway Admin Console and carries a CVSS score of 9.1.
⠀
An authenticated administrator can submit specially formatted configuration values to execute commands within the context of the OAG service account.
Key details:
• Network exploitable
• Low attack complexity
• Administrative access required
• No user interaction required
• Affects OAG versions before 2026.10.2
⠀
Okta has resolved the vulnerability in Access Gateway 2026.10.2. Administrators should manually upgrade affected appliances.
Source:
trust.okta.com/security-advi…


eleven red pandas retweeted

For the next few days or weeks, anyone now has a root CA thanks to eMudhra. Time to have some fun with MiTMing unwilling devices!

eleven red pandas retweeted

Kernel shellcode resources out there:
PLATINUMPICK: Windows KernelMode Shellcode Development Framework
github.com/winterknife/PLATI…
sickle-pdk: payload dev kit with a few ring 0 stubs
github.com/wetw0rk/sickle-pd…
No real generator exists for modern Windows. Guess we’ll have to build one

eleven red pandas retweeted
CVE-2026-81376: VS Code RCE via Security Feature Bypass; $4,000 bounty.
Write-up: samchen.blog/blog/vscode-nes…
eleven red pandas retweeted

x86rc/vmp-lazy-unpack 是一款 Windows 下面的模拟脱壳工具,直接模拟进程加载进行脱壳分析,可以把模拟内存中的进程dump,不挂调试器,不走live dump!
简单来讲,你可以认为它是一个脱壳专用的迷你进程虚拟机!
以前的神级技术现在直接开源了!
github.com/x86rc/vmp-lazy-un…

eleven red pandas retweeted

Check out our new VMProtect (v3.0 - v3.10 latest) unpacker 👀
More to come…

Emulation-based unpacker and import resolver for Windows x64 VMProtect 3.x binaries: github.com/x86rc/vmp-lazy-un…
eleven red pandas retweeted

Windows 这波脸面是真挂不住了。
有人整出一套开源的 PowerShell 脚本,GitHub 上挂着 58K+ 星,图啥都不图,只办一件事:把 Win11 里那批你卸不动、关不了、日日硌应你的破烂,一回收拾利索。
1️⃣ 预装软件、推广插件,成批撵走
2️⃣ 遥测、广告 ID、个性化追踪,悉数掐断
3️⃣ Copilot、Recall、Click to Do 这类 AI 功能,连根薅掉
4️⃣ Bing 网页搜索、Edge 内嵌 AI,统统封掉
5️⃣ 顺带还能把 Win10 的经典右键菜单召回
MIT 开源,白使,不带捆绑,也不偷摸追踪。
最打脸的一点是,微软耗了这么多年,把 Windows 捯饬成广告口、搜索口、AI 口,结果这脚本一行指令下去,它又变回一台老老实实的电脑。
微软前头塞,社区后头删。
🔗 github.com/Raphire/Win11Debl…

eleven red pandas retweeted

Police Squad! was cancelled after just six episodes.
ABC claimed the humour was too dense and fast-paced for ’80s viewers to follow. TV Guide called it “the stupidest reason a network ever gave for ending a series.”
The Naked Gun movies reused many of the same gags and made $477M
eleven red pandas retweeted

Italian firm Dataflow Security, founded in 2019 by young hacker Luca Todesco, develops high-value exploits:
including zero-click tools that break into computers and smartphones and has grown rapidly into a multimillion-euro supplier for governments and spyware makers.
An investigation shows deep ties to Israel’s intelligence and military-cyber world:
former senior Mossad official Eyal Tsir Cohen (shortlisted in 2025 to lead Shin Bet) now heads its two Israeli subsidiaries, while staff include veterans of Unit 8200 and former NSO Group employees.
#osint
irpimedia.irpi.eu/en-inside-…

eleven red pandas retweeted

40 лет назад погиб Клифф. Человек, который в общем-то и научил Металлику играть музыку.
eleven red pandas retweeted

InjectSetConsole performs process code injection by leveraging a Windows named pipe.
Unlike traditional techniques, it does not use the VirtualAllocEx and WriteProcessMemory APIs.
#securityblog #cybersecurity
zerosalarium.com/2026/09/edr…

eleven red pandas retweeted

iMessage EXR. zero click. heap overflow before the banner finishes.
CVE-2026-86869. libAppleEXR sizes the buffer for 3 channels. 12 bytes.
CompressedInterleave4 writes 4. 16 bytes. every pixel.
three of those four bytes come from the file.
BlastDoor never decodes EXR.
Spotlight and the photo indexer do, later, with SDR hardcoded on.
no tap. same ImageIO path on iPhone, iPad, and Mac.
fixed in the 27 releases. older fleet still sits on it.
credit: Niels Hofmans / ironPeak
ironpeak.be/blog/ex-arrr-sai…
#iOS #ExploitDev #InfoSec