



joost retweeted

Exciting news from @Yubico! You can now purchase the #YubiKey 5 Series and Security Key Series with new 5.7 firmware, featuring increased passkey storage and expanded security. Check out our latest blog to get your hands on them for yourself. sprou.tt/1ZV2S5ty51w

joost retweeted

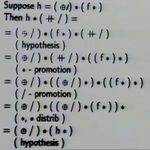
Interested in learning Haskell? The full set of 16 videos from my introductory course based on the book "Programming in Haskell" is now freely available on YouTube. Happy Haskelling :-) tinyurl.com/haskell-notts

joost retweeted

Interested in the Wallet's code release? On 18 March, 16h CET by the @OpenWalletFdn — the EC's wallet team will present the wallet's Reference Implementation and answer questions.
Sign up below! ⬇
zoom.us/meeting/register/tJU…
joost retweeted
The open-source code of the EU Digital Identity Wallet has just been published on our #GitHub.
Are you a developer yourself? Give your two-cents on the code directly on our github:
github.com/eu-digital-identi…
joost retweeted

🔐 Dive into the FIDO Passkey experience with us! Yubico UX needs #YubiKey users for a study on Passkey use on desktop & mobile. Share your insights & get 50% off a YubiKey 5 Series! 🚀
👉 Join now: forms.gle/RiDV3spVJnznn4ta8
#UserExperience #UsabilityStudy #FIDOPasskey

joost retweeted

On November 29th, join us for the unique, free webinar where @PaulaCqure (@CQUREAcademy) and @joostd (@Yubico) will delve into the crucial aspects of secure credential storage.
🔗 Register here: cqureacademy.com/webinar/und…
#staycqure

joost retweeted

Did you know there are approximately 85 organizations authorized to issue TLS certificates for the web today? Or that seven of them issue 99% of all certificates currently in use? The presence of the others is largely intended to accommodate web openness and national sovereignty—an admirable goal, albeit one that introduces a significant attack surface for every web user.
But were you aware that the recent eIDAS legislation, that was just signed, will obligate browsers to trust all QWAC-approved CAs listed on the EU Trust List (esignature.ec.europa.eu/efda…)? To illustrate, Spain has 13 CAs approved to issue these certificates and there are 27 member states in the EU. Additionally, did you know the legislation will not permit browsers to remove of CA with a history of repeated incompetence without government approval?
The most famous of all CA distrust events was an EU CA known as DigiNotar, and those in the PKI space might say that 12 years ago and today, the Conformity Assessment Bodies would have caught that and dealt with it proactively. But is that true? Check out the history of Camerfirma (wiki.mozilla.org/CA/Camerfir…) and wonder why an organization with such poor operational practices that the internet isn't dependent on is still trusted by anyone? Then ask why the associated CAB still lets it be approved as a CA for issuance.
For those who say that the web doesn't need Browsers for such actions, consider this recent incident involving a Turkish CA (bugzilla.mozilla.org/show_bu…). And for those who doubt governments would use CAs to gain visibility into web traffic, take a look at this case where a French CA was doing just that: arstechnica.com/information-….
Supposedly the final text has a recital that was added to the language to suggest that the scope of these requirements is to be limited to trusting these CAs for identity information and not the domain but the document is still private so we don't know for sure. Even if true recitals are not binding and the bill has other issues, for example, it requires browsers to reinstate user interface that has been proven to be harmful and misleading to users. arstechnica.com/information-….
It also prevents the Browsers from establishing additional requirements for the CAs above and beyond what is included in the associated EU legislation, for example, they won't be subject to certificate.transparency.dev which has helped catch many many issues. All this means calcifying the web making it impossible to move forward without legislative change and leaving the web less secure at the same time. Change will now be governed by regulators, lobbyists, and standards boffins that either benefit from this weakening of the web or have no accountability for its consequences.
There are 195 sovereign nations in this world. each would love to be in a position to observe everything their citizens and everyone who interacts with them does. When the world's most liberal and democratic governments put into place the tools to enable mass surveillance and weaken internet security in this fashion what makes us think the rest won't as well.
joost retweeted

Yubico joins EWC’s large-scale pilot for EU digital ID wallets ahead of #eIDAS 2.0
biometricupdate.com/202311/y…

joost retweeted

Future proof authentication with #passkeys - catch @Yubico's @joostd's session at #PlatformSummit2023: nordicapis.com/sessions/futu…

joost retweeted
Interested in learning Haskell? My introductory and advanced courses are available on YouTube, with new videos added each week as the courses progress (intro: tinyurl.com/haskell-notts, advanced: tinyurl.com/haskell-notts2). Now with subtitles!
joost retweeted

Oblivious DNS over HTTPS (ODoH): A Practical Privacy Enhancement to DNS- @sudheesh001, haxxpop, Jonathan Hoyland, @vavrusam, Tanya Verma, @Lekensteyn, @marwanfayed, @kheimerl, @grittygrease, @__caw__ #pets21
joost retweeted

Video: Let’s Flashback to #Authenticate2020 over the next 30 days! Day 16: Watch #Authenticate2020 session on Scalable, Multi-Factor Authentication (#MFA) in the Netherlands! Watch it on our YouTube channel here: youtu.be/vkXK0IP3vCc

joost retweeted
Join us for the new Authenticate “virtual experience” with access to all interactive presentations, booths as 360 degree experience, networking with the global FIDO community + more! Register Now! Free to attend! authenticatecon.com

joost retweeted
We’re excited to announce the new #Authenticate2020 virtual agenda is now available! Get a look at the new sessions you’ll attend – with a focus on the FIDO standards-based approach. Download the new agenda today: authenticatecon.com/agenda/

joost retweeted

🌟 Super excited to announce that our Conference Registrations are now open for our [Online] #Hardware #Security #Conference , Netherlands 2020.
🗓 1st & 2nd October 2020
✅ Register here bit.ly/2EFyo1I
See you at the conference 🙋🏼 🙋🏼♂️
#hwconf_io #hw_io

joost retweeted
Introducing #CrossTalk (#SRBDS), the first #MDS cross-core attack which can leak stale data from an offcore staging buffer shared across cores. See vusec.net/projects/crosstalk where we also show how to leak #Intel #SGX enclave private keys across cores in 1s with just 1 signature:
joost retweeted

Starting rollout: iOS users can now sign into Google Accounts using USB and NFC security keys, in addition to Bluetooth and built-in phone security keys.🥂 to a successful collaboration between @Google, @FIDOAlliance, @w3c WebAuthn and @Apple. security.googleblog.com/2020…
joost retweeted

Call for authenticated video-calling in @nrc newspaper nrc.nl/nieuws/2020/04/28/is-…. Solutions with IRMA_privacy emerge with Jitisi @jitsinews (demo jitsi-demo.tweede.golf/ video youtube.com/watch?v=URn3sn2Y… source github.com/tweedegolf/irma-j…) and soon also with Big Blue Button @bigbluebutton
joost retweeted
#Authenticate2020, the inaugural @FIDOAlliance conference was postponed from its original date of June 2-3. We have secured a date later in the year at the same location in Seattle, WA – November 9-10, 2020! Get the latest information and register today! authenticatecon.com

joost retweeted

We're happy to announce our speaker lineup for #oxidize1k! So far we've confirmed almost all of our speakers, and should have the final lineup available shortly.
We even snuck in a bonus 11th talk in lineup :)
Check it out here: oxidizeconf.com/oxidize-1k/