
les oiseaux volent, les poissons nagent, les humains (se) racontent des histoires.... 𓅃
Suisse romande
Joined December 2009
- Tweets4K
- Following4.2K
- Followers1.6K
- Likes19.9K



Martouf le Synthéticien retweeted

1. Cast, Not Carved 🧵
Here’s the theory in a nutshell—the one I’ll be using to explain all those ridiculous questions "influencers" keep asking about ancient stones.
"How did our ancestors lift 60-ton stones?"
Well they clearly did not, or if they did, they did it in buckets! 🪣🪣🪣🪣
How did they carve the stones to fit together so precisely?
Again, they didn’t—they poured one next to the other.
Why are all the stones different? Why isn’t there a single one that’s the same?
Because they poured them straight into the wall, not into molds—so they didn’t have to lift them later.
Where are the molds then?
Nowhere. They didn’t need them. A few wooden planks or a bit of animal hide was enough.
And I’m not just talking hot air—I actually pour stones: Inca stone, sandstone, granite, limestone.
Alright, now let’s get to the examples.

Martouf le Synthéticien retweeted
Okay, let’s get this straight. The limestone blocks of the Great Pyramid of Giza are ARTIFICIAL. Why? Because they taste salty.
This one fact PROVES it.
No natural limestone contains table salt. None.
I know, I know. Limestone formed in the sea, tidal waves, millions of years of geological processes, blah, blah. NO-NO!
Natural limestone is NOT SALTY! Never! Check this out.
Even though limestone forms on the seabed, beneath miles of salty seawater, its interior contains no salt. Why? Because salt dissolves readily in water and stays dissolved as long as the water remains. When water is squeezed out of limestone, THE SALT GOES WITH IT.
Anyone who has ever tried to extract salt from water knows this. Either you use a salt evaporation pond, or the salt stays dissolved in the water. That’s it.
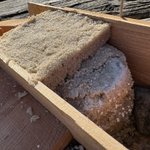
By a strange twist of fate, I happen to have a piece of stone from the Great Pyramid. Before you freak out and accuse me of stealing it, first of all, I didn’t. And second, the person who took it didn’t steal it either. He simply brought it home, back in 1978, long before anyone cared or taking such a piece became illegal.
A friend’s father brought it home at a time when climbing to the top of the pyramid was still allowed. Heck, a French couple even had sex up there, in the middle of a Muslim country. Climbing was banned shortly afterward.
Anyway, my friend’s father took this infamous piece of stone from one of the inner corridors of the Great Pyramid. Go ahead and freak out now, but it doesn’t change anything. He took it more than 40 years ago, and it’s not going to grow back. He brought it all the way back to Hungary in his pocket.
When I read Davidovits’ recipe for making pyramid stones, I came across his claim that the stones are indeed salty. So we organized a pyramid-stone-licking session with the guys. (Don’t freak out again!) Four grown men licked this original, unquestionably authentic piece of pyramid stone.
And guess what?
It IS salty.
So, what now? How did the salt get in there if not millions of years ago? Well, then, thousands of years ago. Exactly.
The recipe is astonishingly simple:
2 parts natron + 1 part quicklime + water = limestone paste (CaCO₃).
That’s the basic idea. But the mixture isn’t salty yet, and it can even release corrosive NaOH. To prevent this, Imhotep added one part magnesium salt (MgCl₂), which transforms the mixture in a rather interesting way. But that’s too much chemistry for one post. I’ll explain it separately.
The point is that the final product is an artificial limestone containing a little dolomite and table salt.
But what about the snails?
“But the pyramid stones must be natural because they contain fossils!”
Ever heard of gravel or aggregate?
As far as I know, it’s absolutely impossible to find billion-year-old pebbles in concrete. Nooo, you can’t mix gravel into concrete! Impossible!
Just as impossible as finding fossil-bearing limestone fragments embedded in a limestone binder.
So much for the snails.
And now comes the inevitable question: “But how did they lift the cast stones into place?”
They didn’t.
Why lift something that’s already in place?
CAST IN PLACE, MY FRIEND. CAST IN PLACE!
Here are four advantages of casting the stones in place:
1. You only have to lift the raw materials, never the finished blocks.
2. Hardly any formwork is needed. Just a few boards, because three sides of each block are already there: the bottom and the two sides formed by adjacent stones.
3. The joints can be so precise that you can’t even slip a razor blade between them.
4. Every block can have a unique shape and size because there’s no need for a standardized mold.
The result? An interlocking wall that could be highly resistant to earthquakes!
If you believe the pyramids were built by aliens, or that 20-ton blocks were hauled 600 kilometers from a distant quarry, that’s your problem. That’s a belief, not an established fact.
LET THE COMMENTS BEGIN! :-)

C'est la saison où on l'on peut observer des essaims d'étourneaux qui se regroupent pour migrer....
Voici une app que j'ai conçue pour étudier ce phénomène d'émergence issu de seulement 3 règles et un rayon de perception. #anarchie #émergence
martouf.ch/boid

Il existe 8 visions du monde selon la #spiraleDynamique.
Quelle est la tienne ?
Voici le test que j'ai pondu pour y répondre:
martouf.ch/test-spirale-dyna…

Pour connaitre en détail ce modèle évolutif de valeurs qu'est la "spirale dynamique". #spiraleDynamique
Voici mon article:
martouf.ch/2017/10/les-etape…

25
Martouf le Synthéticien retweeted

🟥🟩 DOSSIER SOCIÉTAL ET ENVIRONNEMENTAL :
BALLON D'ALSACE, PLUS DE 1 000 ARBRES ABATTUS POUR LE PASSAGE DU TOUR DE FRANCE
➡️🇫🇷 CLOVIS DAGUERRE :
L’entreprise a aussi coupé des arbres sains pour se rémunérer, au détriment de la biodiversité..
Un arbre centenaire ne repousse pas en une génération. Pourtant, il peut disparaître en quelques minutes.
Plus d'un millier d'arbres ont été abattus aux abords du Ballon d'Alsace dans le cadre de travaux liés à la sécurisation de la route empruntée par le Tour de France.
Si la sécurité des usagers est essentielle, une question mérite d'être posée : était-il réellement impossible de préserver davantage ce patrimoine Naturel ..
Les arbres ne sont pas de simples éléments du paysage.
Ils produisent l'oxygène que nous respirons, abritent une biodiversité irremplaçable, régulent la température, protègent les sols et constituent un héritage vivant pour les générations futures.
Lorsque des coupes d'une telle ampleur suscitent l'inquiétude d'associations, de riverains et de défenseurs de la nature, il est légitime de demander des explications et de la transparence.
Le progrès ne devrait jamais se construire au détriment du vivant lorsque d'autres solutions peuvent être envisagées.
Un arbre met des décennies, parfois des siècles, à grandir.
Une décision suffit pour le faire disparaître.
Réfléchissons au monde que nous voulons laisser derrière nous.
(vm.tiktok.com/ZNRK8VU52/)
Vous aimez cette publication ?
N'hésitez pas à réagir et surtout, Partagez-la ! 😉
Rejoignez La Vérité Diffusée
t.me/VeriteDiffusee
Twitter : @VeriteDiffusee
Martouf le Synthéticien retweeted

Dans le sud de l'Iran, où les températures peuvent atteindre 50°C à l'ombre, les habitants utilisent depuis plus de 2 000 ans un système d'architecture bioclimatique: les badgirs, ou tours à vent. Très répandues dans les régions désertiques du pays, notamment autour de la ville de Yazd, ces structures constituent un véritable système de climatisation naturelle.
Leur fonctionnement est ingénieux: la tour capte le vent en hauteur et l'achemine à l'intérieur du bâtiment. L'air traverse souvent un bassin ou un réservoir d'eau souterrain, ce qui le refroidit davantage par évaporation. En parallèle, l'air chaud est évacué par d'autres ouvertures grâce à l'effet de cheminée.
Grâce à ce procédé entièrement passif, l'intérieur des habitations peut rester étonnamment frais, même lorsque la température extérieure dépasse 45°C, et ce sans recourir à la moindre source d'électricité.

Martouf le Synthéticien retweeted

Qu'est-ce que la théorie de l'information intégrée, développée par Giulio Tononi et Christof Koch?
Elle stipule que tous les éléments de l'information communiquent entre eux pour pouvoir reproduire de la conscience.
Dans ce cadre, peut-être qu'un ordinateur quantique pourrait faire naître une étincelle de conscience.
Pour bien d'autres scientifiques, c'est impossible. Il faut renverser la perspective et partir du psychique pour arriver à la matière.
Qu'en pensez-vous?
Vous aimez notre travail? Abonnez-vous à notre newsletter gratuite 👉🏻 antithese.info/inscription-n…
Martouf le Synthéticien retweeted

Ça c'est plutôt une bonne idée !
Avec la chaleur qui est insupportable et parfois dangereuse en été au Japon, cette école maternelle a installé un toit rétractable de 25m x 30m pour que les enfants puissent jouer à l'ombre #Japon
Martouf le Synthéticien retweeted

oui mais @BillGates a dit que cela ne servait à rien
This Post is from a suspended account. Learn more
Martouf le Synthéticien retweeted

L'e-ID acceptée par 21'224 voix d'écart. Financement illicite de campagne par Swisscom. Six recours déposés. Zéro examiné sur le fond. ⚖️
Me Henri Gendre, juriste constitutionnel, analyse les failles démocratiques d'un système de recours qui ne fonctionne pas. 🔍
limpertinentmedia.com/post/e…


Martouf le Synthéticien retweeted

Washington accuse Coop et Migros d'entraver l'accès des produits américains au marché suisse. Berne défend ses normes bio strictes et rejette les pressions sur les OGM et la viande intensive. brnw.ch/21x229t

Martouf le Synthéticien retweeted

Une étude sur dix ans coordonnée par l’Inrae, dont les résultats viennent d’être publiés, montre que l’on peut se passer totalement de pesticides dans les grandes cultures (blé, colza, orge, betterave…) tout en obtenant des rendements satisfaisants…
➡️ l.lepopulaire.fr/Bon

Martouf le Synthéticien retweeted

C’est ça une vraie performance artistique !
Un type a enfilé un sac poubelle et est monté sur le podium pendant un défilé de mode…
Et sans les vigiles, personne n’aurait rien trouvé d’anormal
J'ai lu ce livre entre la fin du monde et vendredi 13....
youtu.be/gJriOCivj_U
C'était le 11 août 1999... La dernière éclipse totale de soleil en Europe. La prochaine sera le 12 août 2026 !
1
129
Martouf le Synthéticien retweeted
L'UE a publié un code de base pour la validation des majorités, qui a été piraté en moins d'une heure. Ceci révèle un mépris pour la technique et une humiliation publique. #Cybersécurité #UE #Tech @epelboin
Le débrief de Fabrice Epelboin, c'est par ici: youtu.be/QI7pOhPKyVg
Martouf le Synthéticien retweeted
Il a fallu un arrêt de justice pour que la Suisse publie ses contrats d'achat de vaccins Covid. On y découvre que l'État a assumé l'essentiel de la responsabilité civile à la place des fabricants. 2,3 milliards de francs engagés. Seulement un quart des doses utilisé.
En Europe, même scénario : la Commission a été condamnée pour avoir refusé de divulguer les SMS entre Ursula von der Leyen et le PDG de Pfizer lors de la négociation d'un contrat d'1,8 milliard de doses.
Dans les deux cas, la même logique. Des intérêts économiques considérables, une opacité soigneusement entretenue, et des États qui absorbent les risques à la place des laboratoires.
C'est ce que les chercheurs appellent le "ghost management", la capacité de l'industrie pharmaceutique à façonner, discrètement mais systématiquement, la perception de ses produits à tous les niveaux du système de santé.
Chez Antithèse, nous avons décidé de vous donner les clés pour comprendre cette mécanique. Nous avons le plaisir de vous annoncer la sortie d'une nouvelle Masterclass de près de trois heures, réalisée avec Catherine Riva et Serena Tinari, deux journalistes d'investigation fondatrices du bureau d'enquête Re-Check, spécialisé dans le mappage des affaires de santé.
Près de 3 heures d'analyse et quatre cas concrets décryptés: mammographie, pilules contraceptives, isotrétinoïne contre l'acné sévère et Tamiflu).
Nous avons tous, à un moment ou à un autre, des décisions de santé à prendre, pour nous-mêmes ou pour nos enfants. Il est important de pouvoir les prendre avec une information vraiment complète.
► Accédez à la Masterclass : antithese.info/masterclass-l…
Martouf le Synthéticien retweeted

Let's shift focus and explain why the #EU #AgeVerification concept is fundamentally flawed.
Assume:
1. The production app is released.
2. It's 100% secure, 100% private (fantasy land, but stick with me)
3. It cryptographically challenges every step, including hardware attestation which requires a physical device.
4. Every single other attack vector in the surrounding environment is somehow magically patched.
aka - it's working exactly as intended/designed.
It does not protect against a relay attack.
This is a threat they considered and somewhat addressed here: github.com/eu-digital-identi…
With the current design, there's nothing preventing someone running a verification-as-a-service; a remote Android device which returns a valid attestation. Remember, it's not returning "I am over 18", it returns "someone is over 18". Neither the verifier, nor the app has any way to link the session ID to a physical device.
Their own docs state this clearly:
Remote Cross-Device Presentation:
"Note that the Wallet Instance does not see any difference between the cross-device flow and the same-device flow. In both cases, it receives an OpenID4VP-compliant presentation request over the Wallet Instance-platform API described in the previous section."
This is a known & well-understood attack vector in all remote credential presentation models; it's just not mitigated in this one... primarily because they can't. CTAP 2.2 won't work with all app flows, hardware attestation doesn't mitigate relay attacks, on-demand liveness detection would be too intrusive & potentially privacy-invasive & timing calculations don't reveal anything useful... all the available options to resolve this break the core design; completely anonymous age verification.
The Architecture & Reference Framework (ARF) is technically sound in some respects. They considered external threat actors and discussed solutions to mitigate them, including ZKP. However, the EC applied the wrong threat model, thus arriving at the wrong conclusion.
Yes, you need to protect against malicious verifiers, phishing sites, session hijacks, data brokers et al... but that's addressing external threats, it doesn't protect the architecture from the user itself.
In virtually every other scenario, the user and system's interests are aligned; protect my biometric asset at all costs.
Specifically for age verification, most users do not want to present ID simply to access a website, so whilst the system may adequately protect from external threats, if the user wants to bypass the system, they can... and the architecture doesn't consider this.
Every single applied mitigation assumes the user is the protected party, not the threat actor.
To those people claiming "it requires physical access to the device and root, this is BS/hyperbole", you too applied the wrong threat model & completely missed the point. These disclosures demonstrate that you, the user, are the threat actor they haven't considered.
You have your device.
You can root your device.
You can create a chrome extension, just as I did.
Ironically, it's precisely those under 18 who can't pass verification who are motivated to bypass it.
So where does that leave us?
A system which replaces "I am over 18" with "someone is over 18", with absolutely no guarantee that it's true... which is the entire purpose of the app.

Bypassing #EU #AgeVerification using their own infrastructure.
I've ported the Android app logic to a Chrome extension - stripping out the pesky step of handing over biometric data which they can leak... and pass verification instantly.
Step 1: Install the extension
Step 2: Register an identity (just once)
Step 3: Continue using the web as normal
The extension detects the QR code, generates a cryptographically identical payload and tells the verifier I'm over 18, which it "fully trusts".
This isn't a bug... it's a fundamental design flaw they can't solve without irrevocably tying a key to you personally; which then allows tracking/monitoring.
Of course, I could skip the enrolment process entirely and hard-code the credentials into the extension... and the verifier would never know.