

I am a security leader working in the industrial/manufacturing space. Life is good. Check my https://xitter.cf/t.co/jBRfTEkSyz for all my social links.
Oswego, IL. USA
Joined August 2008
- Tweets1.1K
- Following234
- Followers138
- Likes2K
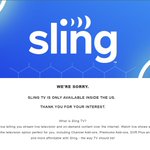




Hey @astoundconnects - not really connecting today?
My Daughter has been without internet for over 12 hours now!!! How long does a fiber cut take to repair.
@NapervilleIL
Charlotte, NC on AT&T Fiber and this? Come on @Sling - surely you want me back as a customer!

Hey @Target - what's going on? Putting the price up to 'discount' it to a final price still above the original price? That's no 'sale'...

Wow. The UK want's unfettered access to worldwide iCloud users private data...
reuters.com/world/uk/uk-asks…
This is bad, very bad. Apple will likely just disable iCloud encryption for UK users.

What occurs when a PAM vendor gets breached... Well... here is one outcome...
bleepingcomputer.com/news/se…
Pick your vendors carefully - monitor their security posture and have a plan if the worst occurs.

Michael Wareman retweeted

After spending the past week leading a ransomware incident response, I wanted to share some insights that you should be thinking about in relation to your organization.
1. Leadership clarity is non-negotiable. Multiple executives giving competing directions doesn't just create confusion - it directly impacts your bottom line. Every minute of misaligned leadership translated into increased recovery costs and extended downtime.
2. Trust your IR experts. Yes, you know your environment inside and out. But incident response is their expertise. When you hire specialists, let them specialize. I've seen firsthand how second-guessing IR teams can derail recovery efforts.
3. Master the time paradox. Your success hinges on rapid containment while simultaneously extending threat actor negotiations. If your leadership and IR partnership aren't solid (points 1 & 2), this delicate balance falls apart.
4. Global password resets are deceptively complex. Every human account, service account, API key, and automated process needs rotation. Without robust asset management and IAM programs, this becomes a nightmare. You will discover dependencies that you didn't even know existed.
5. Visibility isn't just nice-to-have - it's survival. Modern security tools that provide comprehensive visibility across your environment aren't a luxury. This week reinforced that every blind spot extends your recovery time exponentially.
6. Data gaps become permanent mysteries. Without proper logging and monitoring, you might never uncover the initial access vector. It's sobering to realize that lack of visibility today means questions that can never be answered tomorrow.
7. Backup investment is incident insurance. Organizations regularly lose millions that could have been prevented with proper backup strategies. If you think good backups are expensive, wait until you see the cost of not having them.
8. Protect your team from burnout. Bring in additional help immediately - don't wait. Your core team needs to be there for the rebuild after the incident, and running them into the ground during response isn't worth it. Spending money on staff augmentation isn't just about handling the immediate crisis - it's about maintaining the institutional knowledge and expertise you'll need for recovery. Remember: the incident ends, but your team's journey continues long after.
Michael Wareman retweeted

An attacker successfully phished a Cyberhaven employee.
They gained access to their Chrome Web Store admin credentials and published a malicious version of the Cyberhaven extension.


Hey @ChipotleTweets - NOT cool. Letting customers order in the app for pickup - then just not including ingredients AND not telling us. Letting us find out at home - and making a stressed college kid very sad. You really need to fix your app ordering to know out of stock items.

Michael Wareman retweeted

If we had software product liability protections, this wouldn't have happened.
Just saying.

Michael Wareman retweeted

CrowdStrike has performed the largest ransomware attack in history.
Accidentally.
As you roll out Passkey - make sure your users have more than one for recoverability (Hello for Business, TouchID on Mac, Android or iPhone, and FIDO keys like Yubikey are all options) and then DISABLE all other forms of MFA.
darkreading.com/cloud-securi…


