

Security - https://nitter.gq/t.co/4UtTZDCbYe
Joined July 2021
- Tweets1.2K
- Following1.1K
- Followers2.1K
- Likes11.1K




PHYR3WALL 🇺🇲 retweeted

I'm starting to sense a divide in the tech industry:
- People thriving on autonomy who are reinventing how they work and what tools they use with AI: LOTS of work, but they're enjoying it and getting very efficient
- People used to being mentored / trained / or simply told what to do and how. Frustrated with the lack of guidance from management on what to do with AI; also frustrated by seeing some of their peers thriving; increasingly bitter about AI and the state of the industry, as a whole
Neither group seems to be aware that there's another group, or have empathy for the other group
I've never seen "php -s" running in production BTW.

stealmybitcoin was just solved by @killa. Or rather solved a few hours ago. He was confused because the wallet address was wrong. Turns out the server didn't have the right wallet :P
PHYR3WALL 🇺🇲 retweeted

We’ve seen plenty of people try to vibe code the php exploit who have no experience in the domain. Failure. Over and over. Then people who know what they are doing in exploit dev, marginal success.
People would say anyone with a frontier LLM can just say “hack this site, make no mistakes” and I won’t argue, some shallow bugs will fall out this way for a while. But the most successful applications of LLMs are coming from experts who at least know how to dissect the problem, change the models thought direction, and have put engineering into harnesses and skills. I’ve seen this across several sub sections of cyber. And that requirement will only get more mandatory as all the shallow bugs shake out. Just my 2c and observation.
🫶
(Also beware of influencers trolling with opinions on this topic. It’s often just for fake clout and clicks)
Honestly this isn't easy. So many (99.9%) PoCs on X and GH are not actually viable. I leveraged a ton of prior knowledge and research... And used quite a few hints from other researchers to drop as context for my agent. Started as slop but turning into something useful... ish...but still slop

Same same

Update: Our PHP exploit is now production-grade.
* stock php.ini-production, display_errors=off, normal memory_limit, multi-worker, ASLR, under load
* ARM64 + x86-64 targets
* MediaWiki, WordPress, phpBB, Laravel
* Apache/mod_php and nginx/php-fpm -> root
nitter.gq/dguido/status/21131291…
Chances are you don't actually have a working php2shell heap PoC. You likely have a deserialization PoC that requires a gadget or you have display_errors=On.
PHYR3WALL 🇺🇲 retweeted

Quick tweet. Cybersecurity on the offense side, even with what Anthropic released today will be still a heavily restricted models and never the best.
For offense, your only choice is open weight models. I would not rely on frontier models for offensive research.
Invest in hardware or solutions that allow you to use hardware infrastructure as a service.
It will pay dividends.
In stating that, if you can get access to special programs as an organization/company - this is also an incredible option if approved through.

Same same, but different.
@BenAffleck, any interest in working with and investing in a ridiculously talented team of cybersecurity professionals doing some cutting-edge, impactful work at the intersection of AI and cybersecurity?
We're currently in stealth, but building something pretty exciting.

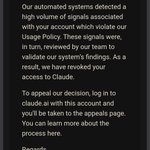
An update to this. A very understanding person from Anthropic's safeguards team DMd me on X asking for my reference number. I gave it to them and they reinstated my account. I reapplied for CVP and was approved instantly for Defensive. Now awaiting approval for Red Team Access.

I have had CVP for quite a while. Just tried to re-verify. Just went to verify and immediately got denied because they couldn't verify my LLC. Then immediately got banned...


Thank you @OffensiveAIcon for a fantastic event. Truly the best conference I've been to. Hopefully you'll have me back next year.


PHYR3WALL 🇺🇲 retweeted

Did anyone get else get CVP dropped, re-apply for CVP, and then get their account suspended for "suspicious activity" or is it just me 😅😑
Been consistently seeing charge rates decreased at @Tesla superchargers. Here's a prime example. What's the deal? I even moved to a stall on the opposite side of the lot. Nobody next to me and preconditioned. "charge rate limited by charging station".


