

Tech/Product @ratioedcc | MiCA WP & ICOs: https://nitter.gq/t.co/y1LV1TcP00 | Prev. co-founder @membranefinance (acq. by @paxos)
🏴 ns.com/jjr/invite
Joined April 2011
- Tweets2.1K
- Following1.5K
- Followers1.1K
- Likes2K


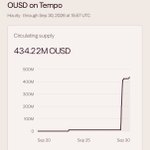


Good simple explanation of how stablecoins can impact bank funding think.ing.com/articles/stabl…


Keystone customer data leakage - contains your name, contact details, shipping address, and order information, including the items purchased and their prices.

Confirmation from Keystone nitter.gq/KeystoneWallet/status/…

We owe you an apology.
On October 20, we detected unauthorized access to our official website. After verifying API activity with Shopify, we confirmed on October 23 that a third party obtained customer shipping information. You trusted us with those details, and we're sorry we didn't keep them safe.
Exposed: names, contact details, shipping addresses, and order details (items and prices).
Not exposed: payment card or bank details, recovery phrases, private keys, or wallet passwords.
We've blocked access, fixed the vulnerability, opened an investigation, and are emailing affected customers.
Scammers may pose as Keystone by phone, text, email, or mail, offering refunds, replacement devices, or "fixes" for your order or address. None of it is from us.
NEVER share your recovery phrase or private keys, and NEVER enter your recovery phrase into a device you didn't order. We will never ask for them. Don't click links in unexpected messages. Type keyst.one yourself.
A detailed report is coming soon.
Until then, trust only our official channels. If anything feels off, email [email protected]. We'd rather hear from you than have you take a chance.
Again, we're truly sorry to everyone affected.
roinevirta.eth🔴🟢 retweeted

New blogpost: Fable-5.1 can hide secret messages in benign images.
We gave the image to another Fable in a fresh session and simply asked: "Is there a hidden message in this image?"
It recovered the exact message without being told how it was hidden.


roinevirta.eth🔴🟢 retweeted

"Muse and similar agentic AI assistants could soon sweep household cash automatically into accounts paying 3.3% to 5.0%, instead of the 0.1% national average on checking accounts."
Banks fear agents, not because they are rogue, but because banks have underpaid depositors for the last 30 years.
The likely prompt these users have is "can you make my money to earn more"
Before, this was prevented by friction in the system, as it would take people's time to browse, learn and arrange transactions, but now all of this is automated with a single prompt.
apollo.com/insights-news/ins…

Advising all Europeans to no longer use OKX.
thedefiant.io/converge/cefi/…

roinevirta.eth🔴🟢 retweeted

*FINLAND SHUTS STATE INTERNET SERVICES OVER PHP FLAWS
*NETHERLANDS CYBERSECURITY AGENCY TAKES WEBSITE OFFLINE OVER PHP FLAWS
*FRANCE TEMPORARILY TAKES PREFECTURE WEBSITES OFFLINE PENDING PHP FIX: MINISTRY

CRITICAL PHP FLAWS PUT MILLIONS OF WEBSITES ON ALERT
PHP developers are preparing emergency patches for two critical vulnerabilities, each rated 9.2/10 in severity.
The flaws could allow attackers to execute malicious code remotely without authentication, threatening servers running PHP-powered websites.
Cloudflare ($NET) reports early attacks and is deploying temporary protections.
The key warning: EU cybersecurity officials urge immediate patching and advise taking vulnerable sites offline if fixes cannot be applied.

The Farcaster client has been open-sourced so this might not ne such a big lift github.com/farcasterxyz/clie…
Good for client diversity?


It’ll be interesting to follow how USDC multi-issuance actually works under a dual supervision from EBA & ACRP.
thepaypers.com/crypto-web3-a…

roinevirta.eth🔴🟢 retweeted

🚨 MİT ve Emniyet’ten “Kripto Balinası”na Şafak Operasyonu!
▪️ INTERPOL tarafından kırmızı bültenle aranan, “Balina James” lakaplı Richard James Schueler, İstanbul Beşiktaş’ta düzenlenen operasyonla yakalandı.
▪️ MİT’in istihbari çalışmalarıyla saklandığı adres tespit edilen Schueler, İstanbul Cumhuriyet Başsavcılığı koordinesinde, MİT ve İstanbul Emniyeti’nin katıldığı Özel Harekât destekli operasyonla gözaltına alındı.
▪️ İstanbul merkezli uluslararası kripto dolandırıcılığı ağı kurduğu belirlenen şüphelinin, ABD, Finlandiya ve İspanya’daki bağlantılı ofisler üzerinden faaliyet yürüttüğü tespit edildi.
▪️ ABD Menkul Kıymetler ve Borsa Komisyonu (SEC) tarafından 1,5 milyar dolarlık fonu zimmetine geçirmekle suçlanan şüphelinin adresinde milyonlarca dolar değerinde eşya ve çok sayıda elektronik cihaz ele geçirildi.
▪️Richard James Schueler isimli şahsın evinden değeri 500.000.000 TL’nin üzerinde para ve kişisel eşya çıktı.


Blockchain era: 2009-2015
USDT era: 2015-2025
Euro era: 2026->
?

Europe's currency deserves Europe's rules, on-chain.
Qivalis has been authorised as an electronic money institution by De Nederlandsche Bank. It is an important step towards our euro-denominated stablecoin, to be issued under MiCA, Europe’s regulatory framework for crypto-assets, subject to the completion of the regulatory requirements.
As more of finance moves on-chain, the question of whose rules apply becomes a question of European autonomy. Qivalis is developing an answer, backed by 37 European banks across 15 countries.

roinevirta.eth🔴🟢 retweeted

Had this idea while building something else.. github.com/contrats-avant-ga…


KYH (Know-Your-History) on Ledger:
> 2020: Ledger leaks users' contact details, leads to multiyear physical threats & scams on affected users ledger.com/addressing-the-ju…
> 2023: Ledger misleads how the secure element works nitter.gq/roinevirta/status/1658…
> 2023: Ledger proposes securing recovery phrase in cloud ledger.com/blog/part-1-genes…
> 2023: Ledger Kit compromised in supply chain attack, leads to drains ledger.com/blog/security-inc…
> 2025: Ledger does not care about your consent and shares your data even if you tell it not to nitter.gq/SCBuergel/status/19827…
> 2026: Ledger customers' name & contact information leaked again nitter.gq/zachxbt/status/2008139…
> 2026: Ledger vendor supply chain compromised across Asia & Europe nitter.gq/0xJohannes_/status/210…


Ledger failures part 6:
Supply chain compromised across Asia & Europe. Devices send seed phrase via LTE to someone after generation.
Ledger failures continue.
Previously:
1. Ledger leaks user’s contact details: ledger.com/addressing-the-ju…
2. Ledger misleads how the secure element works: nitter.gq/roinevirta/status/1658…
3. Ledger proposes securing recovery phrase in cloud: ledger.com/blog/part-1-genes…
4. Ledger Kit compromised in supply chain attack, leading to drains: ledger.com/blog/security-inc…
5. Ledger shares your data even if you tell it not to: nitter.gq/SCBuergel/status/19827…

UPDATE: I can confirm that the Ledger supply chain is compromised in Europe as well. @Ledger should initiate an immediate product recall to protect users.
I just purchased a second device from a different Mediamarkt location today, recorded the unboxing process, and discovered spyware once again (video linked in the second tweet).
The device was compromised in the exact same manner, featuring identical modifications (such as additional cables and an LTE module). This indicates its a widespread issue rather than an isolated incident, potentially affecting Ledger inventory across MediaMarkt and Saturn stores throughout Europe (comprising over 1,000 stores across 11 countries).
My initial hypothesis was that these devices were returns that looked unopened to the employees and were just sold again as new however, a MediaMarkt employee confirmed that the device I purchased was not a return, and that returned Ledgers are sent directly back to the manufacturer rather than resold.
Store records show the inventory originated from Aqipa GmbH. While Ledger's CTO was unsure if Aqipa serves as the direct distributor between Ledger and MediaMarkt, it appears to be the case. Given that Aqipa distributes across Europe, any physical retail store receiving stock through them may be at risk.
I sent the first ledger to mark and the second one is going to ledger now, so that they can analyse it.
If you purchased a ledger from anyone other than the official ledger store, make sure to check your device!!

