

🦜 💻 🔥 🐀
United States
Joined February 2023
- Tweets1.6K
- Following744
- Followers502
- Likes5K



CrypticSploit retweeted

The potential impact of the ConnectWise supply chain attack is massive.
One compromised OAuth application with elevated permissions could give attackers access to emails, files, and directory data across hundreds of Microsoft 365 tenants.
Even worse, attackers could establish persistent access by adding credentials to other applications, surviving the revocation of the original compromised credentials.
And with MSPs involved, the potential blast radius could extend even further to downstream customers.
We don't know the full extent of the compromise yet, but this could affect far more organizations than those directly using ConnectWise Cloud Backup.
linkedin.com/posts/microsoft…


CrypticSploit retweeted

🇺🇸 🚨 CALIFORNIA SAYS ETS BREACH COPIED STATEWIDE TESTING DATA ON PUBLIC-SCHOOL STUDENTS
Educational Testing Service (ETS), the nonprofit that runs California's statewide student assessments (CAASPP, ELPAC) under state contract, has begun notifying students and families, the California Department of Education said on Oct 16, 2026.
An unauthorized party used a compromised login credential to copy files from an ETS SFTP site between May 22 and Sept 18, 2026. ETS identified the activity on Sept 25.
The copied data covers students including, but not limited to, all those enrolled in the previous three school years. It may include names, birth dates, addresses, student IDs, demographics, disability/504 status and assessment results. No SSNs, financial data or passwords.
No total count has been given. ETS says it has found no evidence the data was made public. Notices began Oct 16 and are expected to run through early November.
cde.ca.gov/nr/in/ets-notific…
#DataBreach #California

CrypticSploit retweeted
🇺🇸 🚨 FLORIDA DMV (FLHSMV) CONFIRMS BREACH OF DRIVER LICENSE AND VEHICLE RECORDS, INCLUDING DOCUMENT IMAGES
The Florida Department of Highway Safety and Motor Vehicles said in an official Oct 16, 2026 notice that a malicious actor accessed department records on Sept 4, 2026 using compromised credentials.
Key details:
• FLHSMV attributes the breach to an "international cybercriminal organization"
• Access came through credentials of a local Florida law enforcement agency employee, which FLHSMV says were improperly stored on an electronic device
• Potentially affected: driver license and motor vehicle data, document images and other personal information
• FLHSMV has not said how many people are affected and says it has no evidence of misuse so far
• Letters are going out this week to current license and ID holders, with 1 year of Sontiq (TransUnion) monitoring and $1M identity theft insurance
• Former license, ID or title holders may not get a letter and are covered by a substitute notice
⚠️ Analyst Note:
License data plus document images is a strong kit for identity fraud and account takeover. Expect phishing that impersonates FLHSMV breach letters: check only via flhsmv.gov, and consider a credit freeze. One stored credential at a partner agency was enough to reach a statewide system.
Sources:
content.govdelivery.com/acco…
flhsmv.gov/data-breach/
#DDW #DataBreach #Florida #FLHSMV #CyberSecurity

CrypticSploit retweeted

‼️ UPDATE: Calif showed one-tap attacks on Signal and iMessage on iOS, which make it possible to run code on an iPhone with a booby-trapped PDF.
On iOS 26.5, opening one in iMessage sent the phone's messages to a server.
Calif says everything will be released "in due time."


CrypticSploit retweeted

Jagex has cancelled RuneScape Reignited just days after announcing it.
Reignited was planned as a fresh-start version of RuneScape, giving players new characters, progression and economies.
Jagex has now backed down.
“It is clear that we missed the mark on this, and so we are not moving forward with it.”
He also said the goal is to grow RuneScape without hurting the existing community.
“Our goal is to see RuneScape grow again, with returning players coming back and new players joining, but never at the expense of our existing community.”


CrypticSploit retweeted
40% of workers earning over $300,000 say they're living paycheck to paycheck, per Goldman Sachs.
CrypticSploit retweeted

🔥 100% Untethered Jailbreak on iOS 27💥 It’s over AI has fucked everything up 🤯🚀


CrypticSploit retweeted

Bug bounties are going to take a hit.

To secure open-source software, we’re launching OSS Scanner.
We’ll use our frontier models to periodically scan opted-in open-source projects for vulnerabilities, at no cost. Our reports will provide a proof-of-concept, explanation, and suggested fix.
anthropic.com/research/launc…

CrypticSploit retweeted

Update Telegram Desktop immediately!
A critical vulnerability has been discovered that allows attackers to gain access to your account and secretly steal files from your computer.
The attack uses links in the format tg://. If a special command is constructed, clicking the link can cause a malicious script to send a selected file to the attacker’s channel - without requiring additional confirmation.

CrypticSploit retweeted

🚨 🇺🇸 Pryx says he repeatedly warned 17-year-old “Rey” not to hack the FBI
Adem El Adeb, 19, known online as “Pryx,” told Reuters that he tried several times to stop his friend Saif al-Din Khader from targeting the bureau.
“You’re suicidal,” El Adeb recalled telling him. He said Khader refused to abandon the plan.
Khader, whose alleged online identity is “Rey,” is suspected of playing a key role in the ShinyHunters breach of an FBI jobs platform.
He was detained in Jordan on September 29 and is reportedly cooperating with investigators.
The FBI is operating under the assumption that the stolen dataset may contain information relating to all its employees, although Reuters has not independently confirmed the full scope.
Khader and El Adeb were previously publicly associated with Hellcat, a group known for attacking major organizations and publicly humiliating victims. Hellcat previously claimed the Schneider Electric breach and demanded $125,000 worth of baguettes.
El Adeb claims he left cybercrime before turning 18 and is now creating a cybersecurity company called VulOne. He also told Reuters he remains proud of his past experience.
Reuters could not fully verify his account or the warning messages, which El Adeb said he deleted after Khader was detained.
Source: reuters.com/legal/government…

CrypticSploit retweeted

I got you! Just found a way to steal local Windows user credentials 👀
Turns out, all it takes is a few simple hooks on put_Value and get_Value in credprovdatamodel.dll
CrypticSploit retweeted

Unfortunately, HBO purchased the rights to human executions and witnessing executions carried out by the United States government can only be viewed on HBO Max.

BREAKING: The Pentagon says it will livestream the firing squad execution of Fort Hood shooter Nidal Malik Hasan. apnews.com/article/fort-hood…

CrypticSploit retweeted
🚨🇺🇸🇫🇷 US and French authorities seize websites selling stolen intimate images and CSAM
Authorities seized two domains associated with NudeLeaksTeens (NLT), a platform accused of selling hacked and stolen sexually explicit images and videos of women and girls.
⠀
Investigators found that the site also sold child sexual abuse material, despite displaying warnings that such content was prohibited.
Some collections allegedly included identifying information alongside intimate images. Authorities confirmed that some victims were minors when the material was created.
⠀
One advertised collection claimed to contain 6,200 files obtained from compromised Snapchat, Instagram, TikTok and Facebook accounts.
French authorities simultaneously arrested a 25-year-old man in northern France suspected of being the platform’s main administrator.

CrypticSploit retweeted

KDU — Windows kernel driver utility that abuses vulnerable signed drivers (BYOVD) to bypass DSE, load unsigned drivers, hijack protected processes, and dump process memory. ktp.sh/kluDMA7Buf

CrypticSploit retweeted
‼️ BREAKING: Trump Mobile customers have had their personal data leaked by ransomware gang BYOD. The dump covers 3,615 people and includes names, emails, phone numbers, home addresses and order details.
The gang says the company answered news of the breach with "We have no team to handle this."
The leak includes the Trump Organization's own CIO, who oversees its information security.
People listed in the data confirmed their details are accurate and BYOD claims it still has access to Trump Mobile's backend, Straight Arrow News reports.


CrypticSploit retweeted

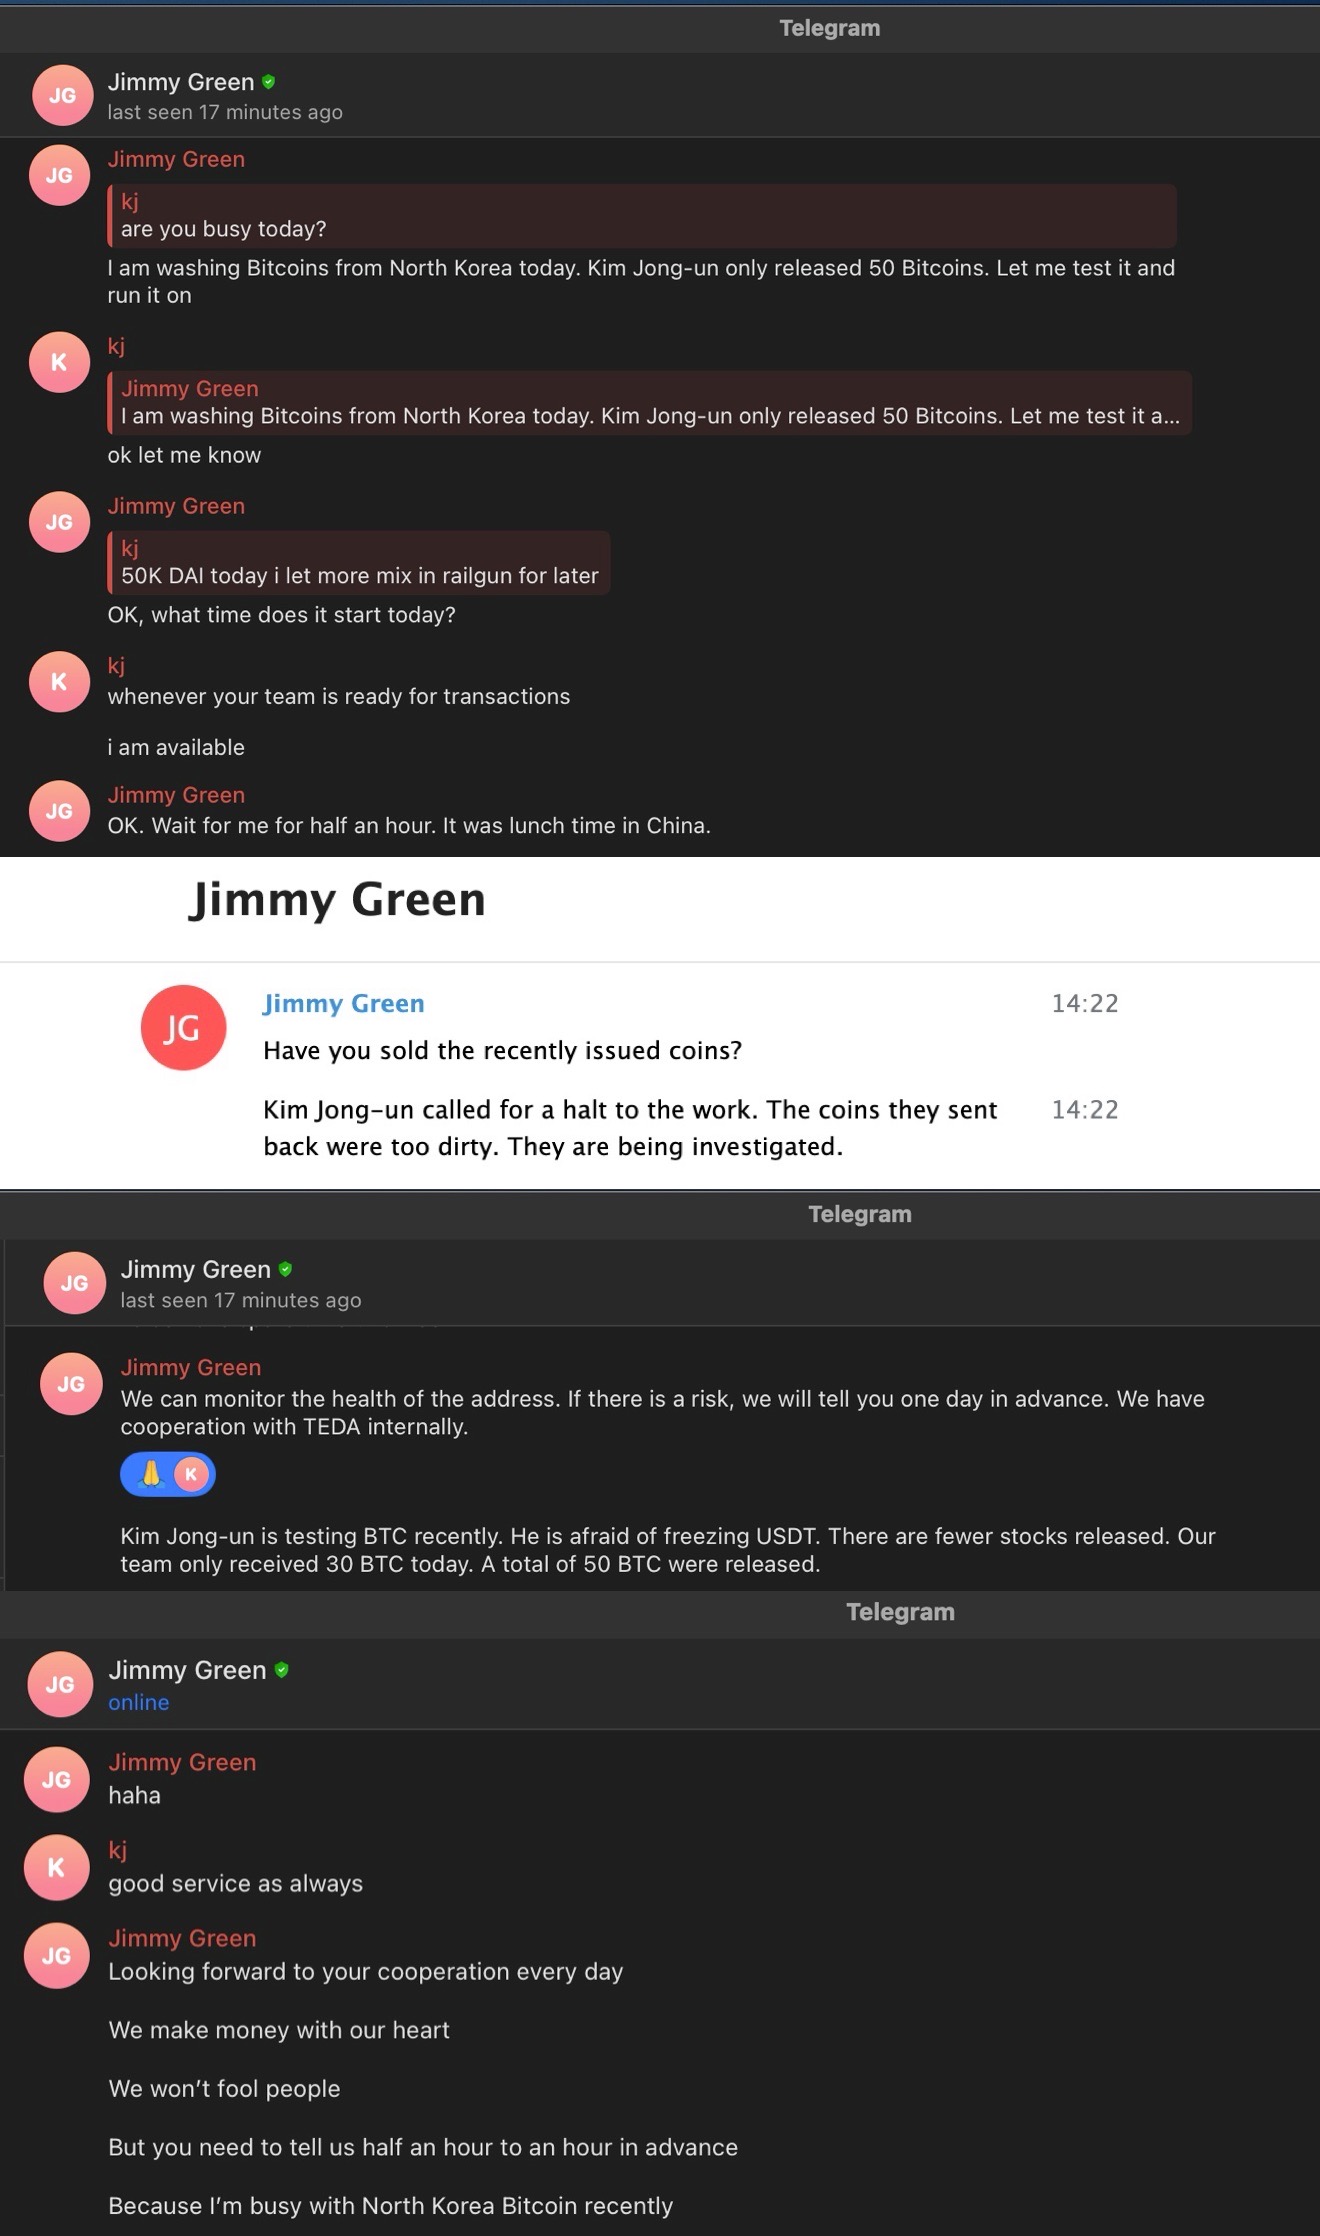
1/ How I infiltrated a Chinese organized crime syndicate that has laundered $1B+ across multiple exploits for Lazarus Group.
Posing as a client, I gathered intel that helped action freezes for the Feb 2025 Bybit exploit and attribute illicit activity onchain.

CrypticSploit retweeted

🚨🇷🇺 HAVE YOU SEEN THIS MOVIE BEFORE?
A "lab accident" may have triggered a real-life PLAGUE scare in Siberia...
Nearly 200 people in Russia’s Irkutsk region have reportedly been placed under medical observation after a lab technician died of the plague.
The woman worked at the Irkutsk Anti-Plague Institute and told medical staff she accidentally broke a test tube containing live bacteria while collecting samples.
Local officials say there are no plague outbreaks currently, including in areas bordering Mongolia.
Some chapters of history are better left closed.
The Black Death is definitely one of them...
Source: Moscow Times / Writer: Marie


CrypticSploit retweeted
🚨 KILLSEC DISRUPTED — SUSPECTED MAIN OPERATOR IS JUST 16 YEARS OLD
International law enforcement has struck the KillSec ransomware operation in a major coordinated takedown.
And investigators say the group's suspected administrator and main operator is only 16 YEARS OLD.
Operation KillSwitch resulted in:
* 3 provisional arrests
* 8 property searches across Spain, Greece, Romania and the UK
* 5 central servers brought under law-enforcement control
* KillSec's dark web leak site seized
* KillSec-controlled domains seized
* At least 110 TB of stolen data secured
* Cryptocurrency and other criminal proceeds now being traced
Europol says KillSec is linked to approximately 1,000 suspected cyberattacks worldwide.
Around 500 have so far been identified as successful, although investigators say that number could change as seized evidence is analyzed.
KillSec has operated since around 2024.
The group allegedly exploited software vulnerabilities and poorly secured access points — particularly cloud storage — to compromise organizations and steal sensitive internal data.
Victims were then listed on KillSec's dark web leak site and threatened with publication unless a ransom was paid.
But there is another interesting detail:
🤖 KILLSEC WAS USING AI.
Investigators found that members used AI to help:
* Build ransomware infrastructure
* Maintain that infrastructure
* Identify potential victims
The suspected administrator is 16.
Another suspected developer turned 18 in August and was reportedly still a minor when some of the alleged offenses occurred.
Authorities have also identified suspected negotiator and affiliate roles, while investigations into additional members continue.
⚠️ Analyst Note:
The age of the suspects is remarkable, but the operational maturity is even more important.
Cloud exploitation → data theft → extortion infrastructure → cryptocurrency → AI-assisted targeting.
Capabilities that once required experienced cybercriminal teams are increasingly accessible to much younger and less experienced operators.
Operation KillSwitch demonstrates the other side of that equation: international investigations can target the people, infrastructure, stolen data AND financial proceeds behind ransomware operations simultaneously.
Official source — Europol:
europol.europa.eu/media-pres…
#DDW #KillSec #Ransomware #CyberCrime #Europol
