

PakCrypt Community exists to develop people who can design, analyze, and prove cryptographic systems. As Pythagoras said in 500BCE "Number rules the universe."
Islamabad
Joined October 2023
- Tweets2.6K
- Following0
- Followers52
- Likes461





🔐 2 competition tracks (Pro and Amo)
🏆 Rs. 7M+ total prizes in Crypto Competition, CTF and Ideas Cup
🌍 12+ International experts
🎓 IACR Cryptography Winter School
📍 NCCS, Air University, Islamabad
📅 24–27 Nov 2026
The first round is open online now.
Can you crack it?
👉 pakcrypt.org/pc26
#Cryptography #CyberSecurityPakistan
#CyberSecurity #InfoSec #Cryptography #CyberSecurityPakistan #Encryption
#PQC #Quantum #CyberDefense #DigitalForensics
#EthicalHacking #OSINT #NetworkSecurity
#ApplicationSecurity
The worm that learned to sign itself 🪱📦
Mini Shai-Hulud did not break the supply chain. It walked through the front door, with valid signatures.
WHAT HAPPENED:
On May 11, 19:20 UTC, 84 malicious versions were published across 42 @tanstack packages in 6 minutes. Within 48 hours, it spread to 172 packages and 403 malicious versions across npm and PyPI, hitting TanStack, Mistral AI, UiPath, Guardrails AI, OpenSearch. Total reach: 518M+ cumulative weekly downloads.
HOW:
No stolen npm token needed for TanStack. Attackers used a pull_request_target workflow to poison the Github Actions cache. When maintainers merged, the poisoned cache ran inside the trusted release pipeline. The worm scraped the OIDC token from runner memory and exchanged it for publish credentials.
Those TanStack packages carried VALID SLSA Build Level 3 provenance from Sigstore. The signature was real. The code was poison. Provenance proved the pipeline was legitimate. It did not prove the code was safe. Tracked as CVE-2026-45321, CVSS 9.6.
TeamPCP, tracked as UNC6780. On May 12, they open-sourced the worm.
If you only check signatures, you missed this. You must check the code, the workflow, and the identity, too.
Source: tenable.com/blog/mini-shai-h…
#CyberSecurity #InfoSec #SupplyChain #npm #PyPI #SLSA

52
🎙️ **We are closing in on the "Holy Grail" of cryptography. Fully Homomorphic Encryption (FHE) is inching from theoretical brilliance into deployable reality.**
For decades, the dream has been simple but elusive: process data *while it remains encrypted*. FHE makes this possible, allowing computations to be performed directly on ciphertext.
But moving from mathematical proof to real-world deployment is a monumental engineering challenge. Here is your technical deep-dive into the promise, the bottlenecks, and the roadmap for FHE. 🧵👇
**1️⃣ THE PROMISE: True Zero-Trust Cloud Computing**
Today, to process data in the cloud, it must be decrypted. This creates a fundamental vulnerability: the cloud provider (or an attacker who breaches them) has access to your raw, plaintext data.
FHE shatters this paradigm. It enables **end-to-end encrypted workflows** where:
☁️ Data is encrypted on the user’s device.
⚙️ Computations (search, machine learning inference, analytics) are performed *directly on the ciphertext* in the cloud.
🔓 Only the end-user holds the private key to decrypt the final, computed result.
The cloud provider processes the data but mathematically *never sees it*.
**2️⃣ THE BOTTLENECKS: Why Isn't It Everywhere Yet?**
The math behind FHE (like BGV, BFV, or CKKS schemes) is computationally brutal. We are currently facing two massive barriers:
📉 **Ciphertext Expansion:** Encrypting a few kilobytes of plaintext can result in megabytes of ciphertext. This creates massive storage and bandwidth overhead.
🐢 **Computational Slowness:** Homomorphic operations (especially "bootstrapping," which refreshes the noise in a ciphertext to allow further computation) are orders of magnitude slower than plaintext operations.
**3️⃣ THE ROADMAP: The "FHE Hierarchy of Needs"**
Researchers and engineers are now framing FHE development like Maslow’s hierarchy. We cannot jump straight to seamless apps; we must build the foundation first:
🔹 **Level 1 (Base): Efficiency & Key Reuse.** Optimizing polynomial multiplication, reducing bootstrapping overhead, and designing schemes that allow safe key switching and reuse without degrading security.
🔹 **Level 2: Hardware Acceleration.** Offloading FHE workloads to specialized hardware (FPGAs, ASICs, and GPU kernels) to achieve the necessary throughput for real-time applications.
🔹 **Level 3 (Peak): Usability & Developer Experience.** Building high-level compilers, SDKs, and frameworks that allow everyday software engineers to write FHE applications without needing a PhD in lattice-based cryptography.
**4️⃣ THE PAKCRYPT VISION: Architecting the Privacy-First Future**
This is the absolute frontier of privacy-enhancing technologies (PETs). At the **PakCrypt Symposium**, we are actively dissecting these exact challenges alongside leading international experts from Germany, Norway, China, and Turkey.
To the brilliant young Pakistani students, developers, and cybersecurity professionals reading this: **This is your greenfield opportunity.** The world desperately needs engineers who can optimize FHE compilers, design hardware accelerators, and build usable privacy-preserving applications.
🔗 🔗🔗🔗🔗🔗🔗🔗
📄 **IBM Research: Fully Homomorphic Encryption Explained:** research.ibm.com/blog/fully-…
🛠️ **Zama: The Developer’s Guide to FHE (Concrete Library):** zama.ai/fhe
#FullyHomomorphicEncryption #FHE #PrivacyEnhancingTechnologies #PETs #CyberSecurity #Cryptography #ZeroTrust #CloudSecurity #PakCrypt #TechPakistan
25
🦀💻 Hackers just brought Rust to the espionage party, and their new toolkit wants to cross air gaps. Defence networks, take a bow. 🫡
Zscaler ThreatLabz tracked a campaign against government and defence entities in India and Afghanistan. Here's the tea ☕
1️⃣ The toolkit: new Rust-based malware, including the RUSTYSHADE backdoor and RUSTYMOVE, a removable-media propagation tool. Rust is the cool new kid, and the attackers apparently wanted the hoodie. 🦀
2️⃣ The air-gap drama: RUSTYMOVE is reportedly built to bridge segmented or air-gapped systems. Translation: the "unplugged" network may not be as unplugged as the org chart claims. 🔌
3️⃣ The disguise game: lookalike domains impersonating ThePrint and India Today, plus a scheduled task named to look like a OneDrive updater. Fake news sites and fake Microsoft vibes. Peak "trust me, I'm a headline." 📰
4️⃣ The infrastructure: command-and-control runs through private GitHub repositories. Hiding C2 in a code platform is the cybersecurity version of hiding your diary inside a developer's repo. 🐙
5️⃣ The vibe check: this is part of a high-tempo campaign. In June, the same group was reportedly also targeting Indian government systems running BOSS Linux, the Bharat Operating System Solutions distribution. Homegrown OS meets uninvited guest. 🇮🇳
6️⃣ The caveat: the Pakistan link is vendor analysis, not official government confirmation. Attribution is detective work, and detectives sometimes get it wrong. 🕵️
if your "air-gapped" network has a USB port, it's not air-gapped, it's just sad. Monitor removable media, watch for scheduled tasks with suspiciously official names, and check the domain before you trust the headline. 🛡️
📖 The Hacker News: thehackernews.com/2026/09/tr…
📖 GBHackers: gbhackers.com/apt36-malware-…
#APT36 #TransparentTribe #Zscaler #CyberSecurity #InfoSec #India #Rust #ThreatIntel #OSINT

36
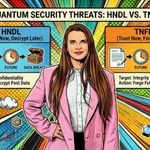
Q-DAY IS COMING. AND THE CLOCK JUST MOVED FORWARD.
For 30 years, Q-Day was a theoretical date in the future. Now Google is warning that quantum computers could break some encrypted systems by 2029.
------------------
1. WHAT IS Q-DAY?
Q-Day is the day a quantum computer has enough power and stability to break the encryption that protects almost everything online.
Michele Mosca, CEO of evolutionQ, puts it like this: "It is the day when people, perhaps adversaries, will have access to a quantum computer that can break cryptographic codes that are in use."
At that point, Mosca says, "everything is safe, safe, safe, and then suddenly it is not safe. It is a very drastic jump."
Financial transactions. Medical files. Emails. Location history. Crypto wallets. All of it could be unlocked.
------------------
2. WHY NOW?
Two things changed the timeline.
First, the Global Risk Institute's 7th Quantum Threat Timeline Report, based on 26 experts, says a full-scale, cryptographically relevant quantum computer is "quite possible" within 10 years and "likely" within 15.
Second, new research from Google, UC Berkeley, Stanford, and the Ethereum Foundation found a 20-fold reduction in the physical qubits needed to break elliptic curve cryptography (ECC), the encryption behind most blockchains and crypto.
Google called it a warning shot. Especially for crypto, where upgrading requires getting a decentralized network to agree.
------------------
3. THE ATTACK IS ALREADY HAPPENING
This is the part most people miss.
Adversaries may already be doing "harvest now, decrypt later."
Steal encrypted data today. Store it. Decrypt it later when the quantum computer is ready.
That means post-quantum protection only protects future data. It does not protect what was already stolen.
As researcher Catherine Mulligan says: "You can upgrade your software, but you cannot really upgrade your DNA."
Health records, genetic data, long-term secrets. Once harvested, they cannot be un-harvested.
------------------
4. WHY OUR CURRENT ENCRYPTION BREAKS
Most internet security, that little padlock in your browser, relies on RSA encryption.
RSA works because multiplying numbers is easy, but factoring them back is incredibly hard for a normal computer.
A quantum computer does not work like a normal computer. It uses qubits that can be 0, 1, or both at the same time through superposition. That lets it solve that factoring puzzle fast.
The Quantum Threat Timeline Report defines a cryptographically relevant computer as one that could break RSA in 24 hours.
------------------
5. WHAT IS BEING DONE?
There is good news, but it needs urgency.
NIST finalized post-quantum encryption algorithms in 2024, designed to withstand quantum attacks.
Google and Cloudflare are both now targeting 2029 to secure their systems with post-quantum cryptography.
The White House recommends 2035 as the target for entities to have adopted post-quantum cryptography.
And there is even quantum key cryptography, first conceived in the 1980s by this year's Turing Prize winners, which uses photons of light and the laws of physics, not just math, to create a secret key.
MIT researchers are also building ultra-efficient chips, 20 to 60 times more energy-efficient, to protect tiny devices like insulin pumps and pacemakers that cannot run heavy security protocols today. Imagine a hacked pump being told: "release lethal dosage."
------------------
6. WHY WE ARE STILL NOT READY
Just over 90 percent of businesses still lack a road map for quantum security, according to data cited by McKinse.
And cryptographic migrations normally take 10 to 20 years. This one will be more complicated and more costly.
As Dustin Moody at NIST says: "If everyone were to migrate on time, we would be in good shape, but the problem is that is not going to happen in the real world."
Worse, the real Q-Day may happen before we know it. Secret state labs, stealth companies, and malicious actors could be ahead of public research. Covert successes would stay invisible.
The report warns: "The real Q-day may occur before the world becomes aware of it."
And a 2023 Hudson Institute report estimated a quantum attack on the Fedwire Funds Service could trigger financial collapse and a six-month recession.
------------------
7. WHAT SHOULD YOU DO?
For most people: Nothing directly. You need to rely on your technology providers to handle this.
For businesses and small companies: Ask your providers one question.
"Have you taken care of the quantum threat?"
That is it. Start the migration now. Do not wait for Q-Day to be announced, because by then it will be too late.
Y2K was avoided because everyone worked hard to prevent it. This is our Y2K moment, except the deadline is moving closer, not further away.
Source: CNN, May 17, 2026
edition.cnn.com/2026/05/17/s…

ALT https://edition.cnn.com/2026/05/17/science/quantum-computing-cybersecurity-q-day
1
98
🎙️ The line between cybercrime and cyber warfare has been permanently blurred. The weaponization of commercial ransomware is no longer a fringe phenomenon; it is a core, calculated tactic of modern conflict.
Cyber-intelligence workshops analyzing the digital frontlines of the Ukraine conflict have observed a stark and alarming trend: state-aligned and paramilitary actors are increasingly integrating cheap, off-the-shelf ransomware kits directly into their military operational playbooks.
Here is your technical deep-dive into the rise of "Malware-as-a-Service" in warfare, the strategic advantages it provides to adversaries, and the global forecast for hybrid cyber threats. 🧵👇
**1️⃣ THE PIVOT: From Bespoke Malware to Commoditized Chaos**
Historically, state-sponsored Advanced Persistent Threats (APTs) relied on highly customized, expensive, and meticulously developed zero-day malware. However, since late 2022, observers have noted a tactical shift. Combatants are now "plugging in" commercial crypto-lockers and extortion frameworks directly into their campaigns. The barrier to entry for causing massive digital disruption has never been lower.
**2️⃣ THE MECHANICS: The Malware-as-a-Service (MaaS) Advantage**
Why spend months developing bespoke tools when you can subscribe to a ready-made weapon? Modern MaaS ecosystems provide hostile actors with:
💻 **Plug-and-Play Crypto-Lockers:** Highly optimized encryption routines that can be deployed rapidly across vulnerable networks.
💬 **Automated Extortion Portals:** Pre-built negotiation sites, leak blogs, and cryptocurrency payment gateways.
🔄 **Affiliate Models:** Allowing less technical "foot soldiers" to execute attacks while the core developers take a cut, creating a scalable, decentralized attack force.
**3️⃣ THE STRATEGIC IMPACT: Force Multiplication & Easing Burnout**
Developing and maintaining custom malware is resource-intensive and leads to rapid operator burnout among elite hacking units. By adopting off-the-shelf ransomware, state actors achieve immediate "boots on the ground" cyber capabilities. This allows them to:
🎯 **Delegate Disruption:** Free up elite APT operators to focus on high-value strategic intelligence gathering, while commoditized tools are used to sow widespread chaos.
🎯 **Plausible Deniability:** Using tools commonly associated with financial cybercrime muddies the attribution waters, complicating diplomatic and kinetic responses.
**4️⃣ THE GLOBAL FORECAST: Proliferation in Contested Zones**
The tactics tested and refined in Eastern Europe are a blueprint for the future. We must expect DIY and commoditized ransomware to proliferate rapidly in contested zones and geopolitical flashpoints worldwide. In these environments, the primary goal of the ransomware shifts from *financial extortion* to *psychological warfare, supply chain disruption, and the crippling of local municipal infrastructure*.
**5️⃣ THE GLOBAL DEFENSE MANDATE: Adapting to Hybrid Threats**
Defending against this evolution requires a paradigm shift in how we approach cybersecurity:
🌐 **Global Threat Intelligence Sharing:** Rapid dissemination of Indicators of Compromise (IoCs) and MaaS affiliate tactics across international CERTs and private sector ISACs.
💰 **Disrupting the Economics:** Aggressive tracking and sanctioning of the cryptocurrency wallets and money mules that fuel the MaaS ecosystem.
🛡️ **Resilience by Design:** Implementing strict network segmentation and immutable backups, ensuring that even if a commoditized ransomware variant breaches the perimeter, the blast radius is contained and operations can continue.
**THE BOTTOM LINE:**
To cybersecurity professionals, threat hunters, and policymakers worldwide: The battlefield has evolved. We can no longer treat ransomware solely as a criminal enterprise; in contested environments, it is a weapon of war. We must adapt our defenses, share intelligence relentlessly, and build systems that can withstand the commoditization of cyber destruction. 🌍🚀🛡️
🔗 **READ MORE **
📄 **Mandiant (Google Cloud) M-Trends Report: Ransomware in Conflict:** cloud.google.com/security/re…
🛡️ **ENISA Threat Landscape Report (Cyber Warfare & Ransomware Trends):** enisa.europa.eu/publications…
#CyberWarfare #Ransomware #MalwareAsAService #MaaS #ThreatIntelligence #InfoSec #HybridWarfare #CyberDefense #GlobalSecurity #CyberResilience #APT
reuters.com/legal/government…
1
77
YOUR PLANE IS NOT ABOUT TO CRASH. BUT YOUR COCKPIT THINKS IT IS.
"Terrain ahead. Pull up!"
That is a command pilots should only hear in a disaster movie. Now they hear it in real cockpits, at safe altitude, because of bogus GPS signals.
Welcome to the new normal of electronic warfare in the sky.
__________________________
1. WHAT IS HAPPENING IN THE COCKPIT?
Around 900 flights every single day are affected by GPS interference.
That number comes from Benoit Figuet at Zurich University of Applied Sciences, founder of SkAI Data Services, which has tracked incidents on GPSWise since 2024.
Pilots report phantom "pull up" warnings from the ground proximity system, map shifts where the plane jumps miles from its real path on screen, and on the runway, systems saying the plane is somewhere else entirely.
One commercial pilot, who asked not to be named, said cockpit displays have "become a work of fiction."
To silence false alarms, pilots sometimes hit the terrain inhibit switch, manually decouple clocks from GPS, and navigate on ground-based systems "like it is the 1970s."
__________________________
2. JAMMING VS SPOOFING
They sound the same. They are not.
Jamming: Disruption. Your GPS signal is blocked. You lose positioning.
Spoofing: Deception. Your system reports a false location. You think you are somewhere you are not.
As Captain Ron Hay, president of the International Federation of Air Line Pilots Associations, which represents over 160,000 pilots in 70+ countries, says: "The aircraft thinks that it is absolutely someplace else. The map does not match. The time does not match."
And the worst part: "When you are being spoofed, you can determine you are being spoofed, but you do not know where you are going to be spoofed."
__________________________
3. WHY IS GPS SO EASY TO BREAK?
GPS signals are incredibly weak by the time they reach us.
They travel over 20,000 kilometers from space. By arrival, they are comparable in strength to a couple of light bulbs.
That makes them easy to overpower with high-intensity radio signals on the same frequency.
The intended targets are usually drones and missiles. Commercial planes are collateral damage.
This vulnerability was long understood. It became a daily problem after Russia's invasion of Ukraine in 2022, when drones were widely deployed in combat for the first time.
Now disruption is endemic in conflict zones: the Middle East, including the region hit by the Iran war, the Baltic Sea, and the Black Sea.
But it is not only there. SkAI has also detected clusters in Asia: on the India-Pakistan border, around North Korea and South Korea, and in Myanmar.
__________________________
4. THE REAL DANGER: NORMALIZATION
Hay says fellow pilots encounter this on a regular basis.
"I have fellow pilots that encounter this on a regular basis. That is the true danger. It is becoming normalized," he said.
He fears pilots will lose trust in critical safety systems as they become desensitized to warnings.
The FAA said the same in its 2026 resource guide: As interference becomes more common, organizations and pilots may develop a higher tolerance for risk.
"Once trust in these systems is lost, it can be difficult to regain."
For passengers, Hay says this is not a reason to panic. It is an operational headache for pilots, airlines, and air traffic control.
Example: A plane crossing the Atlantic that hits interference near the Black Sea may be spaced further apart for safety, lose access to the North Atlantic track system, and be forced onto longer, less fuel-efficient routes. That means delays and disruption.
__________________________
5. WHEN IT TURNED DEADLY
GPS interference has already contributed to a catastrophe.
On December 25, 2024, an Azerbaijan Airlines flight from Baku to Grozny, Russia, crashed in Kazakhstan. At least 38 of the 67 people on board were killed.
According to a February 2025 preliminary report from Kazakhstan's Ministry of Transport, the pilots encountered electronic interference. They lost GPS and reported "pull up" warnings near Grozny, where fog made landing with beacons difficult.
After two failed landing attempts, they turned back to Baku. During the return, the aircraft lost primary control systems and tried an emergency landing.
In October 2025, Russian President Vladimir Putin said missiles fired by Russian air defenses at a Ukrainian drone had caused the crash.
But Figuet is clear: "GPS interference was not the primary cause of the crash. But because of GPS interference, they could not land where they were supposed to."
Ramsey Faragher, CEO of the Royal Institute of Navigation, agrees: "If it had not had the problems with its GNSS, it would have very, very, very likely landed an hour earlier."
__________________________
6. A DAILY NUISANCE IN FINLAND
【entity-Finnair¦canonical_name=Finnair】 calls it a daily nuisance.
Most flights departing southbound from Helsinki encounter GPS spoofing and jamming, says chief flight instructor Captain Aleksi Kuosmanen.
On April 6, Finair flight to Kirkenes, a town in northern Norway near the Russian border, had to make a second landing attempt after GPS interference on the first try.
Finland's Traficom received 421 reports of GPS interference in January and February this year alone. Last year, it received 1,704 reports.
In 2024, Finair even suspended flights to Tartu, Estonia, for a month while the airport improved ground-based landing systems.
Kuosmanen: "We are in a position to manage the situation, and the pilots are used to it. But I would not like to see this as a new normal."
Finland was among 13 EU members that pushed for action. That led to a European Aviation Action Plan in March, with short-term fixes like standard phraseology with air traffic control, and longer-term coordination with militaries on interference sources.
__________________________
7. IS THERE A FIX? NO SILVER BULLET.
Pilots are well trained. But technology has to catch up.
What is already helping:
- Live jamming and spoofing awareness maps from SkAI, integrated into electronic flight bags, so crews know where to expect interference
- IFALPA recommends a ground reset after every suspected flight to erase corrupted signals
- Better software filters to detect big jumps in position and time
- Isolating the GPS receiver from all other aircraft systems
- Controlled Reception Pattern Antennas that filter out spoofing signals
- Galileo, the European system, now lets users authenticate the data they receive
- Stronger signals from low Earth orbit. The European Space Agency's Celeste mission sent its first navigation signal on April 17, aiming for 11 satellites to test better positioning.
Faragher is frustrated: "It is disappointing that the hardware manufacturers have not fixed some of these problems by now."
He points to 9/11: When terrorists stormed cockpits, locks were installed on cockpit doors "within weeks."
"Given the right motivation, things can happen much more quickly."
For now, Kuosmanen says: "We are in a phase of waiting, waiting for new technology, and in the airline industry the change is not always that fast."
"New equipment, new system software requires a lot of testing before they can be set up. In the meantime, it is our job to make sure that our pilots are trained to competently handle these situations."
So next time your flight is delayed on a route near a conflict zone, it may not be weather. It may be that your plane's GPS is being lied to.
And your pilots are flying through fiction to keep you safe.
edition.cnn.com/2026/04/28/s…

ALT https://edition.cnn.com/2026/04/28/science/gps-jamming-plane-navigation-problems
1
637
AI wrote its first zero-day. Google caught it before launch 🤖🛠️
Google Threat Intelligence Group (GTIG) reported the first zero-day it believes was developed with AI. A criminal group planned to use it for mass exploitation. GTIG worked with the vendor to patch it and disrupt the campaign first.
A Python script bypassed 2FA on a popular open-source, web-based system admin tool. Important nuance: it still required valid user credentials. It did not crack passwords. It abused a logic flaw.
Not memory corruption. Not bad input filtering. A high-level semantic logic flaw. The developer had hardcoded a trust assumption that contradicted the app's own 2FA enforcement logic. Exactly the kind of bug fuzzers miss, and LLMs are good at spotting by reading intent.
HOW GTIG KNEW IT WAS AI:
The code gave itself away. Educational docstrings, textbook Pythonic format, detailed help menus, a clean ANSI color class, and a hallucinated CVSS score. Fingerprints of LLM training data.
This was NOT APT45. APT45 is a separate DPRK group in the same report, observed sending thousands of repetitive prompts to analyze CVEs and validate PoCs. The zero-day was by an unnamed prominent cybercrime group. GTIG also said neither Gemini nor Anthropic Mythos was used.
For every zero-day we can trace back to AI, there are probably many more out there, said GTIG chief analyst John Hultquist. The next one will not leave a hallucinated CVSS in the code.
cloud.google.com/blog/topics…
#CyberSecurity #InfoSec #AI #AISecurity #ZeroDay

2
46
yes, this Japan’s cyberdefence package is consistent with the recognition that perimeter defence and reactive patching scale extremely poorly against AI / agentic / automated exploitation of these days.
6
interesting, but an archive of personal conclusions does not substitute for that evidence. Untill, claims that specific ciphers have been used to target Japanese politicians, citizens and industry, and that each has been independently decrypted, require reproducible cryptanalysis: the algorithm, the ciphertext, the method, and the key or the plaintext that results.
6
Good. But It does not, by itself, alter the exposure of the payment systems, ID platforms or energy NW those leaders oversee. Let's c whether the discussion produces shared expectations on concrete items: common minimum standards for critical vendors, mutual notification thresholds for incidents that cross borders, and a realistic view of which systems can still be isolated when a shared service fails.
9
Controls that are not inventoried against actual assets, monitored for whether they fire, and exercised under "realistic failure conditions" remain expensive decorations, unfortunately.
5
The distinction matters: pressure on individuals is cheap; sustained access to critical systems is not. Seems attribution and the linkage to Ukraine policy are political statements.
5
Many of us have first hand experience that retail refrigeration, like much commercial OT, is frequently left on NW that prioritise "maintenance convenience" over isolation / cybersecurity.
6
yes, speeches set the expectation. The failure modes are altered only when the orgs that run the systems are required, and enabled, to treat the threat as a design & legal & regulatory constraint.
9
hmm. AI changes the unit cost of plausible attack variants. Denmark’s notification to the SC is only first step; Let's C whether the utilities now have a standing rule for what they will correlate requests that arrive at different companies under different names.
6
yes. the practical advise is therefore if defenders ignore the same AI tools, cyber defense is screwed. Definitely, the math have not changed; the cost of looking for their edges has.
9
Thanks Marin for putting the overlapping EU instruments in one room. common demand is that financial entities and critical operators can show they are planning for crypto change.
3
It seems that progress on large scale quantum is not exponential as once was predicted. The same paper also notes that no such machine exists. The gap between “if we had these qubits with these error rates” and “we have a refrigerator that runs them” has not. Until the second sentence is true, the first remains a projection.
3
yes, accurately described. Strong crypto was treated as a munition, PGP triggered a criminal investigation, By 1995 everyone realized that the internet will function prety poorly, without ubiquitous encryption. But by 2026 , the payment systems, certificate authorities, cloud providers and messaging platforms that governments seek to compel are load-bearing infrastructure. That raises the cost of refusal for the providers and the cost of exit for the governments. The 1990s is settled however we did not settle this later issue.
2