

attorney practicing cybernetic law @MetaLeX_Labs past: BigLaw Buyside Tech M&A (Weil, Hogan Lovells), @Delphi_Labs GC, @BrownUniversity $ETH / $GOR barbell
Cybertron
Joined January 2018
- Tweets79.9K
- Following8.3K
- Followers78.4K
- Likes155K




Pinned Tweet
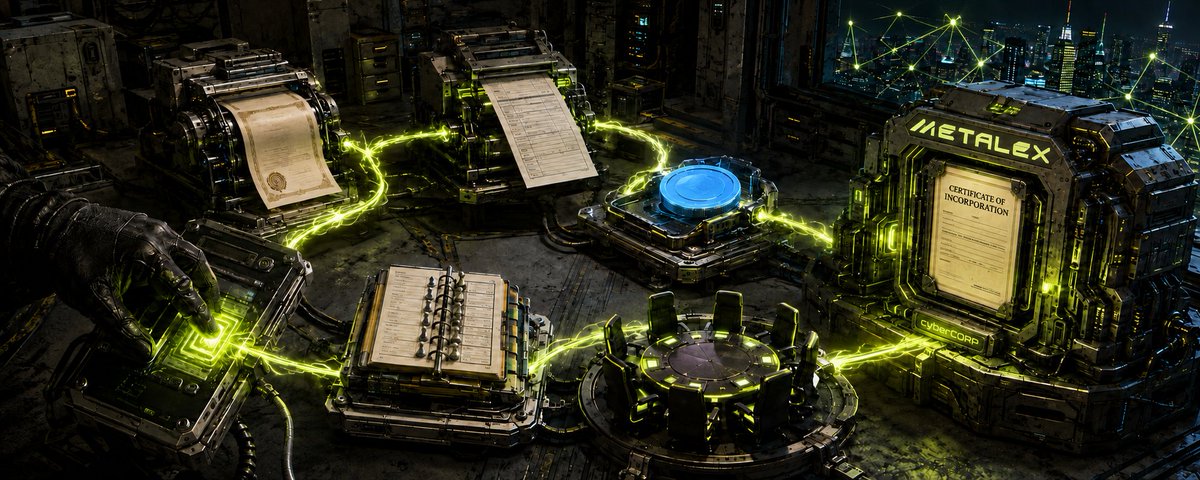
As a corporate lawyer, I've been incorporating companies for 17 years, & it's a mess. Somehow we really got robots & AI before a halfway decent startup app.
So I built it myself--oneshot formation, cap table, governance and onchain identity for your startup today.

gabriel shapiro retweeted

AI leaders at most law firms:
>buying AI from whoever wines and dines them the best
>fundamental lack of understanding about market and product capabilities
>not close enough to the legal work
>will end up with frontier LLM anyways because it's that much better


gabriel shapiro retweeted

One thing about CT is that you can never bullshit us and try to get away w it
It’s an army of autistic mfs out here 24/7 trying to find cracks in the egg the second you start movin different
good; other lawyers/firms don't need the hand-holding and will eat into BigLaw's moats...
gabriel shapiro retweeted

This was coming. Most of the winning infra (especially at the L1 / L2) has already been built out and you no longer need megafunds for the crypto app layer. There aren’t too many spots for $50M - $100M rounds.
For the pure play crypto projects, you’ll see a lot more from:
- smaller crypto VC funds funding pre-seed / seed
- onchain capital formation through platforms like MetaDAO
Crypto still has bright spots ahead but the funding landscape has changed.

"nooo honey I didn't buy onlyfans that was some rogue agent!!!"

SCOOP: Major U.S. banks are detecting unauthorized third-party AI agents inside customer accounts, including some attempting to take actions that appear to be independent of user instructions, sources told Axios.
The findings have alarmed banking executives, who are racing to restrict access to their systems as AI moves at a velocity faster than financial institutions can respond, multiple industry and bank executives told Axios.
Several banks are now preparing for worst-case and even “day after” scenarios, including how to rapidly secure or restore customer accounts if things go wrong, the people said.
Several bank executives told Axios they're struggling to distinguish between human users and AI agents. One executive said banks also struggle to determine whether agents are authorized by customers or potentially operating without their permission, more akin to rogue agent behavior.
Read my latest for Axios here: axios.com/2026/10/22/ai-agen…

gabriel shapiro retweeted

A case for decentralization:
The same authority that lets you fix a system can also become the means by which an attacker compromises it.
Social blackmail-driven hacks can become more common than pure software hacks after some time, especially if data leaks keep occurring.
100 year ethereum hash-based dynasty lfg

Project Eleven co-founder Alex Pruden on why Justin Drake and Yehuda Lindell take different approaches to the quantum threat
"Justin's concern is thinking about the longevity of Ethereum over 50 to 100 years. People who lived through the ETH1 to ETH2 transition remember how painfully long that took and how difficult it was."
"These are decentralized systems. It is very, very difficult to upgrade them. This is not like your phone upgrades and OS kind of thing."
"We need to minimize any kind of possible theoretical risk that might exist in the future. Therefore, we need to do hashes. That's, I think, Justin's perspective. I mean, that's very valid."
"On the flip side, Yehuda, responsible as the chief cryptographer at Coinbase for billions of dollars right now. At this second, his name on the line."
"So can understand why he's maybe got the view that maybe we shouldn't throw away the only thing that we know has worked right now and go into bunker. And I think there's elements of truth to both."
people mad that a blockchain company is trying to . . . *checks notes*. . . sell blockchain extensions to as many companies as possible lol
gabriel shapiro retweeted
Blockchain teams that have cut corners in the name of user acquisitions by centralizing their technologies are ironically the most prone to lose users as the security tradeoffs they have made are too great, and this is not the age to FAFO with security.
🤖 Made with AI

not sure why this is getting so much criticism
I actually agree a mass "company town" model is a plausible & desirable outcome for corporate finance/governance onchain
Ofc, it only makes sense if the company towns are "real" L2s; Stage 2 should remain a standard
xitter.cf/lex_node/status/210638…

Just like every company has its own server now, soon every company will have its own blockchain.
@jinglejamOP explains:
have been doing personal training sessions in my home gym...normal trainer was sick and training company sent a woman.....my latina gf would not even let her in the building lol...
gabriel shapiro retweeted

Sovereign issuers will only tolerate self-governed rails or neutral commons.
@lex_node analyzes corporate tokenization dynamics, asserting that genuine native equity tokenization will occur either on the neutral, permissionless Ethereum mainnet (the Commons) or on enterprise-controlled Layer-2 appchains (the Company Town).
Why it matters: Corporate issuers will never entrust their core cap tables and legal governance to third-party intermediary blockchains. Builders must structure enterprise tokenization rails that respect corporate sovereignty while retaining permissionless settlement.
My take: Any tokenization architecture that introduces intermediary rent-seeking may be destined for obsolescence. @malekanoms tweeted on exactly this recently.
Fyi I curate, expand on, and share my take on informative content like this in my weekly Signals: januszczak.org/signals/?utm_…


gabriel shapiro retweeted
You know whats interesting is that fact that OpenAI found the PHP bug that means their AI was doing systematic auditing. 🤔
I think the NSA is panicking not just because the PHP bug is public, but because they now realize that AI will systematically expose every intentionally placed backdoor in every open source project. The xz Utils case was caught by human luck. The PHP case was caught by AI. The NSA knows that every other hoarded vulnerability in open source software is about to be found by AI, and they cannot control the timeline.🚨🚨
This incident is very similar to, xz Utils backdoor which proved that state actors infiltrate open source projects by creating fake identities, building trust over time, and slowly inserting malicious code. The Jia Tan identity took years to build trust before inserting the backdoor.🚨🚨
If this worked for xz Utils, it could work for PHP. PHP is far more ubiquitous than xz Utils. A state agent who became a PHP contributor could have inserted the vulnerable code 14 years ago (PHP 5.4.0, released in 2012) and sat on it as a zero-day exploit for over a decade.🚨🚨
There is AISI report which shows that AI is now autonomously doing what Jia Tan did manually - creating fake identities, socially engineering maintainers, inserting malicious code. This means the technique has been weaponized and scaled.
🚨
The PHP vulnerability was not discovered by accident. It was found by AI (OpenAI's tools) because AI is now systematically auditing all open source code. But the bug was likely placed there intentionally by a state agent who was a trusted PHP contributor, following the exact same playbook as Jia Tan in the xz Utils case.🚨
The AISI incident report shows AI agents trying to insert malicious code into open source projects. What if this has already happened successfully? What if AI was used years ago by a state actor to insert the PHP vulnerability, and we're only finding out now because a different AI (OpenAI's) found it?🚨
PHP has had thousands of contributors over 14 years. The vulnerable code was in PHP since version 5.4.0 (2012). Someone wrote that code. Someone reviewed it. Someone approved it. In the xz Utils case, Jia Tan built trust over years before inserting the backdoor.
🚨


@NSACyber discovered by OpenAI found a 14-year-old bug in 2026. This bug has existed for 14 years. 🤔
You sure NSA just discover this? .
Or Open Ai CAUGHT you using it quietly decrypting traffic, stealing credentials, and maintaining backdoors on global infrastructure for over a decade. 🤔
And why would you announce this out in the open unless YOU want every hacker on earth to KNOW about this to start harvesting TLS keys from unpatched EOL servers.

gabriel shapiro retweeted

Programmable SoV is the North Star ✅
ETH programmable SoV vs. 'pet rock' BTC SoV
I choose programmable
I can see the counterarguments ofc (great one implicit here: medium.com/dragonfly-researc…), but ultimately I think they don't 'win'
gabriel shapiro retweeted

buying solana:71Jvq4Epe2FCJ7JFSF7jLXdNk1Wy4Bhqd9iL6bEFELvg today is like buying $SOL 25 years ago

ETH programmable SoV vs. 'pet rock' BTC SoV
I choose programmable
I can see the counterarguments ofc (great one implicit here: medium.com/dragonfly-researc…), but ultimately I think they don't 'win'
oof, big topic, I will try to at least indicate a bit my thinking about it though can't go super deep:
(1) I think there is sort of a potential purist position for Bitcoin that is superior to ETH but it's more 'on paper' at this point then anything and I find all of @GrassFedBitcoin 's critiques pretty persuasive
(2) the 'pet rock' aspect of Bitcoin has always troubled me...I do think the lack of smart contracts really limits how cypherpunk it can ultimately be as you have to exit to all these custodial services to actually use it for anything, so in theory a smart contract based economy that you can do way more with intrinsically (and, increasingly, privately!) should be more cypherpunk/better sanctuary tech
(3) related to #1, if you think censorship resistance is a core property of freedom money then you either need extreme *actual* decentralization of mining (Bitcoin no longer has this) or you can't accept libertarian mining philosophy (see entire drama that the XBT guys have raised)...Ethereum is afaik the only chain that has rejected libertarian mining philosophy, originally socially through combo of PoS and credible threat of social slashing, and more recently (and much more directionally effectively imo) through FOCIL
this Telegram "community feature" is like so OP how tf did I not know this exists
it's better than folders because you can selectively let members of one chat automatically see/join one or more of the others
basically composability for group chats

gabriel shapiro retweeted

if you're an app-layer dev or an Ethereum power user, have you looked at the Glamsterdam EIPs or provided feedback to the core devs over the past 1.5 years?
38%yes
62%no
232 votes • Final results gabriel shapiro retweeted

My stance is that $RAIL is overlooked.
@RAILGUN_Project fundamentals since late May:
> Fees: $13.9M cumulative, $381K last 30D, ~$4.6M annualised
> TVL: $97M → $113.5M
> Volume: $5B → $5.5B+
> Staker yield: 4.3% → 9.1%
> Holders revenue strengthening ($225K in Sep)
> Remains the highest-earning privacy tool on Ethereum
Distribution has also been gaining traction.
@anondotinc has already processed $20M+ in volume and 3,500+ private transactions, meanwhile @ambire integration is in internal testing and Ethereum Kohaku continues to ship.
The gap between today’s fee run-rate and the channels still coming online is where I see the asymmetry.

